3 The inner-product polynomial commitment
This section constructs the inner-product polynomial commitment that opens the commitments of §2.9 at the verifier’s point. It states the problem, performs one halving step, recurses it into the full argument with both parties’ tables, gives the verifier’s closing computation, proves knowledge soundness under the discrete-logarithm assumption, proves honest-verifier zero knowledge of the masked opening, runs the running example’s polynomial through every round on a curve of prime order , and in the last subsection gives the parameters, the normalisation, the opening, the bytes and the deferred check of the deployed Halo 2. Beyond the Math Guide, the section relies on these parts of the Crypto Guide: the Pedersen vector commitment (§“Pedersen vector commitments”), extractors and the tree extraction of Sigma-protocols (§“Knowledge soundness and extractors”, §“The Schnorr identification protocol”, §“Sigma-protocols”), the simulation paradigm (§“The simulation paradigm and zero knowledge”), hashing to a curve (§“Hashing to a curve point”) and the standing assumptions (§“Standing assumptions”). From this volume, the generic argument takes only the cue of §2.9; the toy reuses the running example’s advice polynomial and random point (§2.2, §2.4), restated where used; the last subsection takes the deployed circuit’s field from §1.2 and the advice, permutation, lookup and quotient objects from §2, and forward-references §4 for the row count and the remaining objects of the proof; the other references to §2 mark where the argument is used.
3.1 The problem: an inner product in fewer than group elements
The prover holds a vector of field elements. She has published one group element,
the Pedersen vector commitment of with blinder under the public generators and (Crypto Guide, §“Pedersen vector commitments”; the mixed inner product of a scalar vector with a vector of group elements is the Math Guide’s, §“The mixed inner product with group elements”). The verifier holds , a public vector of his own, and a number the prover claims. He wants to be sure that
There is a trivial protocol: the prover sends and ; the verifier recomputes from them, which the binding of the commitment makes a meaningful check, and then computes himself. It costs field elements and reveals . Neither is acceptable here: the vector is the prover’s secret advice, and the verifier of §2.4 asks for evaluations rather than polynomials because a polynomial is long, so a proof as long as the vector gains nothing. The problem is therefore:
Convince the verifier that for the vector committed in , using fewer than group elements, and without revealing .
Why this is polynomial evaluation.
Let be the polynomial with coefficient vector , and let be a point. Then
Evaluating a committed polynomial is therefore exactly the problem above, with the public vector of powers of the point. The running example makes it concrete. The advice polynomial of §2.2 is over , so and ; the random point of §2.4 is , so in ; and the value the verifier needs is . Everything the random-point check of §2.4 asks of the prover, “open , , and at ”, is four instances of this one problem.
Where the difficulty sits.
The commitment is linear in the vector: adding two commitments commits to the sum of their vectors, and scaling one by commits to (Crypto Guide, §“Pedersen vector commitments”, the remark that linearity survives). The inner product is linear in too. But the two linear maps land in different places, one in the group and one in the field, and by the hiding of the commitment no public operation takes to . A claim about a vector of length one is checked by sending the scalar and its blinder. The argument that follows reduces the length by halving. Each halving step turns a claim about vectors of length into a claim of the same shape about vectors of length , at a price of two group elements, and after steps the claim is about a single scalar. The argument uses exactly this linearity.
The relation.
Throughout, is a cyclic group of prime order and its scalar field, so that is a one-dimensional -vector space (Math Guide, §“The mixed inner product with group elements”).
Definition 3.1 (The opening relation).
Fix public generators and in . To open the committed polynomial at with claimed value is to prove membership in
where is the public statement and the witness. The condition is the degree bound : a commitment under generators can only hold coefficients.
Notation for the section.
The following conventions hold from here to the end of §3.
-
•
The vector length is , and is also the exclusive degree bound and the number of generators. The round count is . The letter , the row count of Definition 2.7, is not used until the deployed parameters at the end of the section, where ; the constraint degree stays as §2.5 fixed it. The Crypto Guide’s sketch of this argument indexes its generators from to and bounds the degree by inclusively; nothing changes but the labels.
-
•
Generators are indexed from , , so that the coefficient of multiplies ; the Crypto Guide’s “Pedersen vector commitments” indexes its generators instead, a shift of labels only.
-
•
The letter names the blinding generator of the Pedersen commitment; the evaluation domain of §2 does not appear in this section. The letter names the group order, and with an argument, , the committed polynomial.
-
•
The letter is the running example’s opening point, , and the generic one. The deployed protocol has a second challenge which its description also calls ; this volume writes it .
- •
-
•
In the byte count of §3.8, is the number of Actions, an integer, not the vector .
-
•
A vector of length splits into its low half, the first entries, and its high half, the last : , and likewise for and .
3.2 One fold, every step written out
One halving step is called a fold. This subsection performs one fold on a vector of length .
Carry the claim inside the group element.
The commitment says nothing about or . Bring them in: after is fixed, the verifier samples a further generator uniformly from and sends it. Both parties form
| (11) |
If the prover is honest, : a single group element carrying three kinds of information on three independent sets of generators, the vector on , the blinder on , and the inner product on . The claim “ commits to and ” has become the claim that has this one shape, for some and , with the -coefficient tied to the -coefficients by the inner product with the public . The fold preserves exactly this shape while halving the vectors.
Split into halves.
Write , and , each half of length . An inner product splits along the halves:
The fold.
Let be a nonzero challenge, and define the folded vectors of length ,
| (12) |
entry by entry: , and for . The coefficient vector is folded with the weights and the generator and evaluation vectors with the inverse weights ; this is the symmetric fold of the Halo paper and of Bulletproofs, and the reason for the inverse weights appears in the next computation.
The inner product of the folded vectors.
Expand using bilinearity of the mixed inner product (Math Guide, §“The mixed inner product with group elements”), one term per pair of halves:
The two diagonal terms, low with low and high with high, have weight and reassemble the original : that is what the inverse weights were for. The two cross terms, low with high and high with low, survive with the weights and . The same expansion for the scalar inner product, with folded by the same weights as , gives
The cross terms do not depend on the challenge.
The four cross inner products , , and involve only the halves, not . The prover can therefore commit to them before the challenge is drawn. She samples two fresh blinders and sends the two group elements
| (13) |
each of the same three-part shape as : a vector part on the generators, a blinder on , and the matching scalar inner product on . Only then does the verifier draw .
The fold identity.
Now add the cross terms to with the weights the expansion produced and regroup by generator set:
where and the last line substitutes the two expansions. Written as one equation, the fold identity is
| (14) |
What has been achieved.
Compare the two sides of (14) with (11). The element has the same shape as , over vectors of half the length: its -part is the folded coefficient vector, its -part a blinder, and its -coefficient the inner product of the folded vectors. The verifier can compute , and entirely on his own from , , , and the public data. The prover computes and . The claim about of length has been replaced by a claim about of length , and the exchange cost exactly two group elements and one field element of challenge. Figure 7 shows the fold and identity (14). Only completeness is claimed here; that a prover who cannot open cannot open either is proved in §3.5.
The evaluation vector folds into a power vector.
When , the high half is the low half scaled: , since . Hence
the folded evaluation vector is again a vector of powers of , scaled by the scalar . The verifier never needs to store ; he needs one scalar per round. This is the seed of the closed form of §3.4.
The fold at , symbolically.
For the running example’s length, the halves are , , , , and , so the cross terms of (13) read
and the folded vectors are , and . Section 3.7 fills these in with numbers.
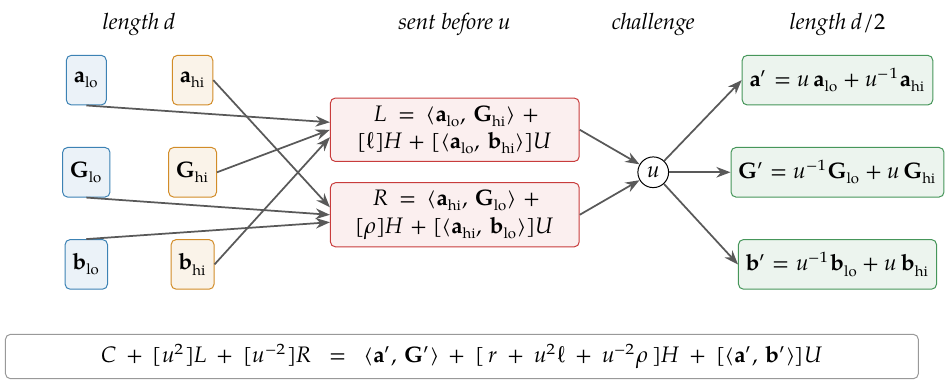
3.3 The recursion: rounds to a single scalar
The folded claim of §3.2 has the shape of the original claim, so it can be folded again. After folds the vectors have length one, and a length-one claim is checked by sending the scalar and its blinder. That is the whole protocol; this subsection writes it out as a construction, numbers the rounds, and lays the two parties’ work side by side.
Construction 3.2 (IPA-based polynomial commitment).
Let be a cyclic group of prime order in which the discrete logarithm problem is hard (Crypto Guide, §“Standing assumptions”), and let . Choose and sample the generators and independently and uniformly from , as in the Crypto Guide’s Construction “Pedersen vector commitment” (§“Pedersen vector commitments”). Deployed generators are instead hash-to-curve outputs on public labels, uniform when hash-to-curve is modelled as a random oracle into (Crypto Guide, §“Hashing to a curve point”, Remark “Why NUMS generators are binding-safe”).
Commitment. For and a blinder ,
Opening. To prove , the two parties proceed as follows.
-
1.
Setup. The verifier samples uniformly from and sends it. Both parties set , and ; the prover sets and .
- 2.
-
3.
Final message. After round every vector has length one. Write , and for the single entries. The prover sends the scalar and the aggregated blinder
-
4.
Check. The verifier accepts if and only if
(15) where the left-hand side is and , are computed as §3.4 describes.
The round index descends so that round begins with vectors of length ; round is the first round and round the last. The scheme instantiates the polynomial-commitment interface of the Crypto Guide (§“Polynomial commitment schemes”, the inner-product alternative), and the opening protocol is the inner-product argument of Bootle, Cerulli, Chaidos, Groth and Petit as refined in Bulletproofs by Bünz, Bootle, Boneh, Poelstra, Wuille and Maxwell, in the symmetric normalisation those papers use.
Completeness.
The honest prover always passes. By induction on the rounds,
| (16) |
at this is (11) with the honest , and the step from to is the fold identity (14) applied to the round’s vectors, challenge and blinders. At the vectors have one entry each, the inner products are products of scalars, and (16) reads , which is (15). The only way an honest run can fail is a challenge , which the verifier excludes.
Proof size.
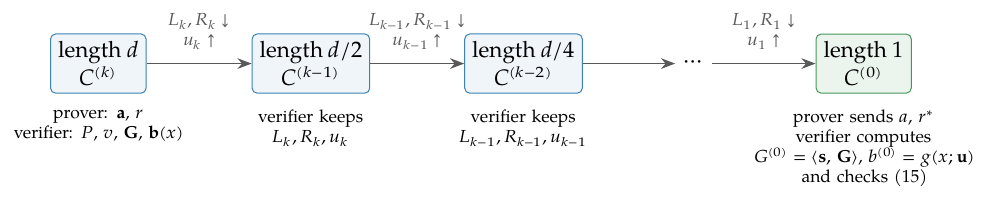
The prover sends two group elements per round and two field elements at the end: group elements plus , against the field elements of the trivial protocol. The verifier keeps only the challenges and the received points; he need not fold round by round, as the next subsection shows. Figure 8 draws the rounds, and Tables 2 and 3 list, one row per message, what each party holds, computes and sends, so that a reader can play either role; §3.7 refills the same rows with numbers.
| step | receives / holds | computes and sends |
|---|---|---|
| setup | holds , , , ; receives | sets , , , |
| round | vectors of length , split into halves | samples ; sends , as in Construction 3.2 |
| receives | folds , , ; | |
| final | one entry each: , | sends , |
| step | receives / holds | computes and sends |
|---|---|---|
| setup | holds , , , , | samples and sends it; sets |
| round | receives , | samples and sends it; keeps ; optionally |
| final | receives , | computes and (one length- multi-scalar multiplication), ( field operations), and checks (15) |
3.4 The verifier’s work: structured scalars and the final generator
The check (15) needs two quantities the verifier has not yet been told how to obtain cheaply: the final generator and the final evaluation scalar . Folding round by round costs scalar multiplications (two per entry of each folded vector), and folding likewise many field operations. Both have closed forms in the challenges.
Theorem 3.3 (Structured scalars and the polynomial ).
For write the binary expansion with digits , and define the structured scalars
| (17) |
Then, after the folds of Construction 3.2,
| (18) |
where
| (19) |
a polynomial of degree in .
Proof.
Follow one original generator through the folds. Claim: after the rounds have been performed, contributes to exactly one entry of , the entry at position , with coefficient , where is the digit of at position . At nothing has happened and the claim says sits at position with coefficient . For the step from to : round folds the length- vector by for . The position lies in the low half exactly when the digit of is , in which case it moves to position with the extra factor ; and it lies in the high half exactly when , in which case it is the entry with and moves to position with the extra factor . Either way the new coefficient is the old one times , which is the claim for . At every sits in the single entry with coefficient , which is the first half of (18). The vector is folded with the same weights, so the same argument gives .
For the closed form, expand the product (19): choosing from the -th factor either (when ) or (when ) produces, for each , the monomial , and every arises from exactly one choice. Hence , whose value at is , and whose degree is since the top monomial has coefficient . □
At the scalars are , , and , and : the digit of weight selects the exponent of , the round that folded pairs of neighbours, and the digit of weight selects the exponent of , the round that folded the two halves of the whole vector.
The final equation, and why it checks.
The verifier’s closing work is now explicit. He evaluates from the challenges; he computes , one multi-scalar multiplication of length ; he adds up the left-hand side of (15) from , , the received points and the challenges, scalar multiplications; and he compares it with the right-hand side, three more scalar multiplications. For the honest prover the two sides agree by the invariant (16). That a dishonest prover cannot make them agree except by knowing an opening is §3.5.
The cost of the final check.
Evaluating at costs field multiplications: products , squarings to produce the powers , and multiplications of the factors together; at that is four multiplications, and at Orchard’s it is . But is a linear combination of all generators, and computing it is a multi-scalar multiplication of length , at Orchard’s some scalar multiplications: the one part of the verifier’s work that is linear in the size of the committed vector, and the check “linear in ” that §2.6 deferred to this subsection. Everything else the verifier does is logarithmic. The asymmetry has a name in the closed form: is nothing but , the unblinded commitment to the polynomial whose value the verifier just computed in operations. Checking a value of is cheap; checking its commitment is not. This asymmetry is the seed of the accumulation scheme of §7, and of the deferral described at the end of this section.
3.5 Why it is binding: extraction from three transcripts
This subsection shows that any prover that makes the verifier of Construction 3.2 accept knows an opening of with , in the operational sense of the Crypto Guide (§“Knowledge soundness and extractors”): an extractor that runs the prover as a subroutine, rewinds it to an earlier state and feeds it fresh challenges computes the pair from its answers. The mechanism is the one that makes Schnorr’s identification protocol a proof of knowledge (Crypto Guide, §“The Schnorr identification protocol”): a single transcript reveals nothing, but two accepting transcripts with the same first message and distinct challenges are two linear equations, and subtracting them cancels the unknown commitment and leaves the witness. Here each round has three unknown group elements instead of one, so three transcripts are needed per round, and the rounds stack the three-way branching into a tree, the tree special soundness of the Crypto Guide (§“Sigma-protocols”). The single-round step is pure linear algebra and is proved in full; the tree is an induction on it; the discrete-logarithm assumption enters once, at the root.
Representations.
Fix a level with generator vector of length . A representation of an element over is a triple with
Call the representation well formed at level if its -coordinate is the inner product of its -coordinates with the round’s evaluation vector, . The invariant (16) says exactly that the honest prover holds a well-formed representation of at every level. A representation over folded generators lifts to one over the generators of the level above: if with , then by bilinearity
| (20) |
and the lift preserves well-formedness, since . Under the discrete-logarithm assumption a prover can know at most one representation of any : two of them differ by a nontrivial relation among , and , which is the binding argument of the Crypto Guide (§“Pedersen vector commitments”). Nothing below uses this until the root is reached.
Lemma 3.4 (Single-round recovery).
Fix one round of Construction 3.2 at level : the verifier’s element , the generators and evaluation vector , and the prover’s cross terms , . Let be three challenges for this round, and suppose that for each a representation of the folded element over is known. If the squares are pairwise distinct, then representations , and of , and over are obtained by solving one linear system with rows , and they satisfy, for each ,
| (21) |
If the three given representations are well formed at level , so is the recovered representation of .
Proof.
Write the three known representations as vectors and the three unknown ones as . The three group equations
suggest the linear system
to be solved coordinate by coordinate. Multiplying the row of by the nonzero scalar turns it into , which does not change the kernel. If , the polynomial of degree at most vanishes at ; when these squares are pairwise distinct it is zero (Math Guide, §“Roots and the factor theorem”, Theorem “At most roots”), so is invertible. When two squares coincide, two rows of coincide and is singular. Define as the unique solution. Because it solves the system exactly, for each , which is (21) read coordinate by coordinate. That the solutions are representations of , and follows by taking the same linear combinations of the group equations: let be the middle row of , so that and . Adding times the first group equation, times the second and times the third gives, on the left, , and on the right, by bilinearity, . The first and third rows of do the same for and . For well-formedness, set and , , . Subtracting the inner product of the first identity of (21) with from the third gives for each , that is, . If the given representations are well formed the right-hand side is zero, and invertible forces ; in particular . □
Theorem 3.5 (Knowledge soundness of the opening protocol).
Let be a group of prime order in which the discrete logarithm problem is hard, and let and be uniform in as in Construction 3.2 (for hashed generators: hash-to-curve modelled as a random oracle into ). The opening protocol of Construction 3.2 is knowledge sound for : there is an extractor which, given rewindable access to any prover that makes the verifier accept with non-negligible probability, runs in expected polynomial time and outputs either a witness with and , or a nontrivial discrete-logarithm relation among , and the verifier’s generators , . Its knowledge error is .
Proof.
The proof is given at the level of this volume: the single-round step is Lemma 3.4, the tree is an induction on it, and the rewinding that supplies the sibling transcripts is the Crypto Guide’s (§“The Schnorr identification protocol”, the remark on extraction by rewinding, and §“Sigma-protocols”, the tree-extraction theorem cited there, which also gives the expected running time). The trees it assembles have children with pairwise distinct challenges (the Crypto Guide’s Definition “Tree special soundness”), while Lemma 3.4 needs pairwise distinct squares. A square has at most two square roots, so any five pairwise distinct challenges contain three with pairwise distinct squares: the rewinding assembles five children per node, and the extractor uses three of them. From a tree the extractor computes a witness or, at the root, a discrete-logarithm relation; that definition asks for a witness alone, and the difference is where the assumption enters.
Leaves. Rewind the prover to the moment after it sent and obtain three accepting final messages for three challenges with pairwise distinct squares. An accepting final message is, by (15), a representation of over , namely , and it is well formed at level : its -coordinate is the inner product of with the length-one vector . Lift it to level by (20): .
One node. The three lifted leaves are well-formed representations of the three folded elements over . Lemma 3.4 at the round- node returns a well-formed representation of (and representations of and , which are not needed further).
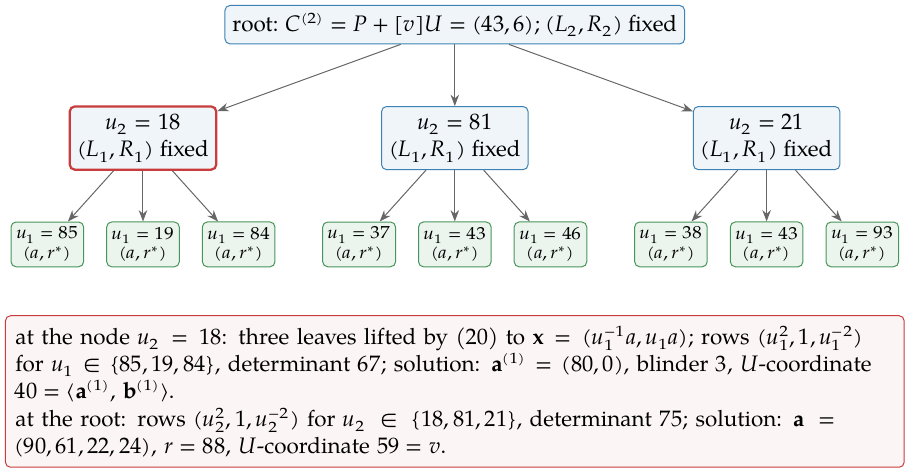
Induction. Rewind to the moment after , obtain three challenges with pairwise distinct squares, and under each of them repeat the two steps above. That yields, after lifting to level , three well-formed representations of the elements , and the lemma at the round- node returns a well-formed representation of . Continuing upward, after levels the extractor holds a well-formed representation of over , with . The tree of transcripts consumed has three children at every node and depth , hence leaves (Figure 9).
The root, where the assumption enters. The root representation says . If then is a witness: and . If , the extractor rewinds once more, to the setup step at which the verifier sampled , and repeats the whole extraction under an independent sample , obtaining . If the witness is . Otherwise subtracting the two expressions for gives
with the nonzero coefficient on : a nontrivial relation among the independent uniform generators , , , , which the every-generator embedding of the Crypto Guide (§“Pedersen vector commitments”, the proof of binding) turns into a discrete logarithm, the reduction embedding its challenge in the public generators and in the verifier’s samples alike. This is the only place the assumption is used.
The error. The figure does not come from a union bound over the tree. At each node the extractor needs three siblings whose challenges avoid values: for each earlier sibling’s challenge , so that the squares stay pairwise distinct. Each of the rounds therefore contributes , and the rounds together with the resampling of give , the theorem’s figure. Collisions among the challenges resampled inside the -leaf tree cost the extractor a rewind and a fresh sample; they affect its expected running time, not the knowledge error. A naive union bound over the roughly sibling draws would bound the tree-wide collision probability by , still negligible, but that is not the source of the figure. The weaker sometimes quoted for this argument is implied by the proved bound; a larger protocol whose own error is already linear in loses nothing by quoting it. □
What the theorem does not say.
The theorem concerns the interactive protocol; the compiled argument is treated in §5. In the algebraic group model the extractor does not rewind for the representations at all: an algebraic prover hands them over with every group element it sends, and the tree collapses to a single transcript (§5, “The algebraic group model”). After the Fiat–Shamir transform has replaced the verifier’s challenges by hashes, the rewinding above must be re-proved against a prover who can query the hash adaptively and resume from any earlier transcript state (for one round, the Crypto Guide’s forking lemma, §“Security in the random oracle model and the forking lemma”; the multi-round case in §5), and its cost cannot be obtained by multiplying every node of the tree by an independent factor. Nor does the theorem restate the binding of the commitment itself: that a single cannot be opened as two vectors is the Crypto Guide’s theorem, cited in §2.9 and not reproved here.
The assumption, and what breaks it.
The extractor’s alternative output is a discrete-logarithm relation among , and the verifier’s , , so the argument is binding as long as discrete logarithms are hard in and the generators are uniform; hashed generators are uniform when hash-to-curve is modelled as a random oracle into (Crypto Guide, §“Hashing to a curve point”, Remark “Why NUMS generators are binding-safe”), a hypothesis of Theorem 3.5. For the deployed instance the group is the Vesta curve (§3.8), and the assumption that carries the argument is the discrete logarithm on Vesta, the first of the Crypto Guide’s standing assumptions (§“Standing assumptions”), against which the generic attacks cost about operations (§“Instantiation on elliptic curves; the Pasta curves”); a quantum adversary running Shor’s algorithm lies outside those assumptions, which fix a classical adversary. Suppose the assumption fails: an algorithm computes discrete logarithms on Vesta. Then it computes the logarithms of the hashed generators to one base, and every commitment opens to every vector: for any whatsoever, the blinder satisfies , and the honest protocol run on convinces the verifier of , a value the cheat chose. One commitment then opens to two vectors and to two values at one point; binding and evaluation binding fall together, and with them the premise of Theorem 2.5 that the polynomials were fixed before was drawn.
Example 3.6 (The extractor run on the toy).
The extractor is run against an honest prover for the running example’s vector opened at with , on the prime-order- curve and generators of §3.7, with the blinder , so and . It fixes , branches over three round- challenges , and under each fixes and branches over three round- challenges: , and , nine leaves in all. At the node the system has determinant and returns the representation with blinder and -coordinate , well formed as the lemma promises; the other two nodes return and likewise. At the root the system in has determinant and returns , and -coordinate : the extracted witness is the committed vector, its blinder, and the true value. Figure 9 draws the tree with the node called out.
3.6 Zero knowledge: what the blinders hide and what they do not
The transcript of one opening consists of group elements, challenges and two final scalars. The group elements are hidden by the blinders: the commitment blinder makes uniform in whatever is (perfect hiding, Crypto Guide, §“The Pedersen commitment” and §“Pedersen vector commitments”), and the round blinders make every and uniform and independent of everything else for the same reason, since each carries its own fresh or . The aggregated blinder is uniform too, being plus a combination of the fresh and . The final scalar is not hidden by these blinders.
Remark 3.7 (Folding alone is not zero knowledge).
The final scalar is a linear form in the committed coefficients whose coefficients the verifier knows. Follow one coefficient through the folds exactly as the proof of Theorem 3.3 followed : the coefficient side folds with the weights , the inverse of the generator side’s , so reaches the single final entry multiplied by , the factor when the digit of is and when it is . Writing for this vector, entry by entry, and
| (22) |
In the toy of §3.7, with and , the vector is , the entrywise inverse of the structured scalars , and the final scalar is . One opening thus hands the verifier one linear equation in the four secret coefficients; every further opening of the same commitment under fresh challenges hands him another, and of them determine outright. Four openings of the same vector, with challenge pairs , , and , end in the scalars , , and , and solving the system recovers . Blinding the commitment and the round points hides those points, not this scalar. The masked opening below therefore does not fold itself: it first masks the polynomial by an independently random polynomial vanishing at the opening point, so that the linear form is taken of a vector the verifier cannot relate to . The mask’s commitment and the challenge that follows it are essential to the zero-knowledge argument below.
The masked opening.
The masked opening runs Construction 3.2 on a masked statement.
-
1.
Mask. Before any folding, the prover samples a polynomial of degree below with : she draws the coefficient vector uniformly from and then replaces by , which makes uniform on the hyperplane . She samples a blinder and sends
-
2.
Challenge. The verifier sends a uniform .
-
3.
Opening. By linearity of the commitment (Crypto Guide, §“Pedersen vector commitments”, the remark that linearity survives),
(23) a commitment to the coefficient vector of the polynomial , whose value at is . The parties run Construction 3.2 on the statement with the witness , the verifier sampling in its setup step, after and .
-
4.
Final message and check. The prover sends the final scalar and the aggregated blinder . The verifier accepts if and only if
(24) which is (15) for the masked statement.
Completeness is that of Construction 3.2, since the witness satisfies for the masked statement; the mask leaves the opened value unchanged because . The transcript of one opening is
The hiding argument.
The final scalar is the linear form (22), taken of the masked vector:
| (25) |
In the toy, with , for which , and , the masked vector is , its inner product with is , and under the challenges , of the unmasked run the final scalar is with ; a second mask under the same challenges ends in , and both runs are accepted (§3.7). The same form, on a different masked vector, gives an unrelated scalar.
Proposition 3.8 (Honest-verifier zero knowledge of the masked opening).
Let have prime order , and let the verifier draw uniformly from , uniformly from and each uniformly from . There is a simulator which, given but not , outputs challenges and a transcript whose distribution lies within statistical distance (Math Guide, §“Statistical distance”) of the honest one. The masked opening is therefore statistical honest-verifier zero knowledge, not perfect, in the sense of the Crypto Guide (§“The simulation paradigm and zero knowledge”).
Proof.
Call a challenge tuple good if and is not a multiple of . The vector is uniform on the hyperplane , a subspace of dimension . The linear functional (Math Guide, §“Bilinear forms and the inner product on ”) restricted to that subspace is nonzero unless is a scalar multiple of . If , the first entries force , and the entry at , whose only nonzero digit is , reads , that is, ; each of these equations has at most two solutions , so at most challenge tuples among are excluded. A nonzero linear functional on a vector space is onto , and its fibres are the cosets of its kernel, all of equal size, so it carries the uniform distribution to the uniform distribution on . For good challenges is therefore uniform, and by (25) so is , independently of .
In an honest run with good challenges, and every , are uniform and independent (fresh blinders), is uniform and independent of them (the mask), and is the unique scalar that makes (24) hold once everything else is fixed, generating . The simulator produces the same distribution in the reverse order, the way the Schnorr simulator chooses its commitment after the challenge (Crypto Guide, §“Sigma-protocols”): it draws the challenges as the verifier does, draws , all and all but uniformly from , draws and uniformly from , and sets to the one point that satisfies (24), namely . Both distributions are uniform on the solution set of the one equation: the honest run parametrises that set by the points and , with determined; the simulator parametrises it by points and the two scalars, with determined; and each parametrisation is a bijection onto that set, with points on each side since and both have elements, because the determined coordinate is unique in each case. For good challenges the simulated transcript is therefore distributed exactly as the real one. The challenges have the same distribution in both, and the tuples that are not good have probability at most ; the statistical distance is at most that probability. □
The gap, stated.
This argues one opening in isolation. The proof system opens many committed polynomials at once, under shared challenges, and the mask is one of several blinding devices it uses; whether the joint transcript reveals nothing is a separate question, addressed under “Zero knowledge: hiding the witness in Halo 2” in §4, where the mask, in the deployed form of §3.8, reappears as the last of those devices.
3.7 A complete toy opening, carried by script
The toy opening commits the running example’s advice polynomial, of §2.2, and opens it at the random point of §2.4 with : the opening the proof system needs, of a column polynomial at the verifier’s random point, never of the statement polynomial at the running example’s secret witness . Every value below is computed by script and can be recomputed by hand in and on a curve with points.
A genuine group of order .
The vector lives in , so the commitment group must have order : scalars of a prime-order group live in the field of its order (Math Guide, §“Base fields, scalar fields, and the Pasta cycle”), exactly as the deployed circuit’s field is the scalar field of the deployed commitment curve. The group has order but trivially computable discrete logarithms, a division, so the toy uses an elliptic curve. For a curve over a prime field to have exactly points, the Hasse bound (Math Guide, §“The group structure of ”) confines the prime to : . The case is excluded on purpose: a curve with as many points as its base field has elements is anomalous, and its discrete logarithm is easy (Math Guide, §“The elliptic-curve discrete logarithm problem”). The first short Weierstrass curve (Math Guide, §“Weierstrass equations”) in lexicographic order of with exactly points is
counted point by point; is prime, so the group is cyclic and every point but generates it, and its trace is not . It is the same kind of object as the Math Guide’s worked curve over (§“A worked toy example”), one size up. With points every discrete logarithm on it is a short search; the toy exhibits the algebra of the argument, never its hardness.
Generators from a hash.
The generators are derived from public labels by hashing to the curve, as the deployed ones are: the label and a counter are hashed to a candidate -coordinate, and the counter is incremented until is a square in . This is a variant of the try-and-increment loop of the Crypto Guide (§“Hashing to a curve point”), which increments itself; its constant-time refinement is irrelevant to a toy. Indexed from so that the coefficient multiplies , the generators are
The hashed point stands in for the verifier’s uniform sample of Construction 3.2. No party chose any of them, so no relation among them is known in advance; a single discrete logarithm between two of them would give one, since yields . On this curve such a logarithm is a short search; on Vesta its infeasibility is the assumption of §3.5.
The instance.
The prover holds , which takes the values on the domain of §2.2, and the blinder ; her commitment is
The verifier holds , the point , hence in , and the claimed value . With there are rounds, numbered then .
The symmetric opening, both sides.
Tables 4 and 5 refill the rows of Tables 2 and 3 with numbers, listing each party’s inputs and computations; the verifier’s table never uses .
| step | receives / holds | computes and sends |
|---|---|---|
| setup | holds , , , ; receives | , , , |
| round | halves , ; , | samples , ; , ; sends , |
| receives () | ; ; ; | |
| round | halves , ; , | samples , ; , ; sends , |
| receives () | ; ; ; | |
| final | , | sends , |
| step | receives / holds | computes and sends |
|---|---|---|
| setup | holds , , , , | sends , a hashed point standing in for his sample; |
| round | receives , | samples and sends it; keeps ; |
| round | receives , | samples and sends it; keeps ; |
| final | receives , | ; ; ; right-hand side : accept |
The verifier’s equation (15) closes: the left-hand side is , and so is the right-hand side . Each fold identity holds along the way: after round , , and after round , . The closed forms of Theorem 3.3 agree with the folds: is the the prover reached by folding, and is her . In a group of elements collisions among the printed points are frequent, and nothing follows from any of them. Here happens to equal and happens to equal ; the masked run below and the runs of §3.8 show more.
A false value is rejected.
Let the prover claim instead of . The prover’s messages are those of the honest run; only changes, by one more . The left-hand side becomes while the right-hand side stays , and the verifier rejects. By Theorem 3.5, a prover accepted on would yield an opening of with value and hence, beside the honest opening, a discrete-logarithm relation among the generators; on a curve of points such relations are a short search, and the theorem gives no security there.
The masked opening of the same polynomial.
The same is then opened at the same with the masked opening of §3.6. The prover samples , for which , and , and sends ; the verifier answers . The masked vector has inner product with , and the rounds run on it with the point , the challenges , and the round blinders of the unmasked run: the prover sends , , and , and ends in and . The final generator and the final evaluation scalar are those of the unmasked run, since they depend on the challenges alone. The verifier’s equation (24) closes at on both sides, and the false value moves the left-hand side to : rejected. A second mask under the same challenges ends in and is accepted as well.
3.8 Halo 2’s specifics: parameters, generators from a hash, the deferred multi-scalar multiplication, and the proof bytes
Everything above holds for any prime-order group and any . This subsection, and only this one, fixes the group, the size, the generators and the normalisation of the deployed Halo 2, states its opening, and counts the bytes an Orchard proof spends on the argument. Nothing earlier in the section depends on it.
The group and the size.
The Orchard Action circuit does its arithmetic in , the base field of the Pallas curve, because the statement manipulates Pallas points and their coordinates live there (§1.2; Math Guide, §“Base fields, scalar fields, and the Pasta cycle”). Its column polynomials therefore have coefficients in , and a Pedersen commitment to such a vector needs a group whose scalar field is : that group is the Vesta curve, whose order is (protocol specification, § 5.4.9.6, “Pallas and Vesta”). The specification uses Halo 2 with the Vesta curve to prove and verify the Action statement (§ 4.1.13, “Zero-Knowledge Proving System”), so every , , , and of this section is a Vesta point and every scalar a Pallas base-field element. The other half of the Pasta cycle, Pallas’s scalar field being Vesta’s base field, is needed only by the optional native recursion of §7; Orchard’s verifier never uses it. The committed polynomials have degree below the row count of the Action circuit (Definition 2.7; the count is given under “From statement to circuit: arithmetisation in practice” in §4), so here and the argument runs rounds.
Generators from a hash.
The vector generators, the blinding generator and the inner-product generator are all outputs of hash-to-curve on one fixed domain-separation label, the vector generators indexed by their position and and by two further tags (Crypto Guide, §“Hashing to a curve point”, Construction “Nothing-up-my-sleeve generators”). With hash-to-curve modelled as a random oracle into they are independent and uniform, and a relation among them yields a discrete logarithm on Vesta (the same section, Remark “Why NUMS generators are binding-safe”). No secret is generated in producing them, unlike the trapdoor of KZG (Crypto Guide, §“Polynomial commitment schemes”, under “KZG: evaluation in the exponent”), the point the closing subsubsection returns to. Because is a fixed parameter rather than a verifier’s sample drawn after each , the deployed opening re-randomises it per opening with a challenge (“The deployed opening in full” below).
Challenges from the transcript.
The interactive verifier of Construction 3.2 draws uniformly from , and the halo2 book’s Protocol Description excludes zero challenges. The deployed verifier is a hash (“Removing the verifier: the Fiat–Shamir transform” in §4), and the transcript of the halo2_proofs implementation squeezes every challenge, , and each , as a full field element with no rejection of zero. A zero would make the fold’s inversion fail, so the honest prover succeeds unless one of the challenges is zero, an event of probability per challenge, about : completeness of the deployed argument is overwhelming, not literally perfect, in the sense fixed in §1.2.
Remark 3.9 (The deployed IPA normalisation).
The deployed opening, stated in full below, is the masked opening of §3.6 with three changes. It folds with the weights on the coefficient vector and on and , with cross terms and , the halves swapped relative to (13), and the verifier’s accumulation ; it scales the cross terms’ -coordinates by a further challenge drawn after ; and it moves the claimed value into the commitment as in place of . Its final scalars are and , and its check is (29). The halo2 book, which the protocol specification (§ 5.4.10.3, “Halo 2”) cites for the proving system, states this opening in its chapter Protocol Description. Its blinding generator is this volume’s , its is , and its second challenge is , renamed because is the running example’s opening point; the book’s comparison with the scheme of Bünz, Chiesa, Mishra and Spooner (chapter Comparison to other work) writes , and for the same three objects. The chapter numbers the round challenges from the first round, , where this volume’s descending index gives , and states the verifier’s evaluation polynomial (its ) as
| in its numbering, | (26) | |||||
| in this volume’s, |
with structured scalars , beside the symmetric of (19) with .
The change of variables. The two folds are one argument. Run both on the same vector, the same generators and the same evaluation vector, with the deployed challenge of every round the square of the symmetric one, . In one round, writing for ,
so , and , and the scalings cancel in every inner product: and . The cross terms agree, up to their -blinders, once the naming is unwound: the deployed carries , which the symmetric presentation calls , and its weight is the symmetric weight on ; likewise for the other cross term. The single-round form holds for one round on identical inputs; over several rounds the change of variables is cumulative, because each round’s inputs already carry the previous rounds’ factors:
| (27) |
with the symmetric challenges of the rounds already run. Each deployed factor of (26) is a symmetric factor scaled, , so after rounds
while and carry the product itself, so that and agree in both normalisations, and the two verifier equations coincide once each run attaches and to the same cross product. Table 6 prints both runs on the toy’s data and keeps the blinder names instead, so the deployed run attaches each blinder to the other cross product, and its equation differs from the symmetric one only in the -term ( against ); with the blinders exchanged, the deployed run also closes at with . What the substitution does not do is identify the challenge distributions: a uniform deployed challenge is not the square of a uniform symmetric one (“Extraction in the deployed rows” below), so the deployed rows are analysed with their own lemma, and the deployed opening is knowledge sound by the argument of §3.5 with Lemma 3.10 at every node and two branchings, over and , in place of the resampled at the root: Corollary 3.13.
| symmetric fold | deployed fold | relation | |
|---|---|---|---|
| round : challenge | |||
| cross terms sent | , | , | halves swapped |
| round : challenge | |||
| cross terms sent | , | , | halves swapped |
| structured scalars | |||
| aggregated blinder | |||
| verifier’s equation | same , |
Extraction in the deployed rows.
The deployed fold changes the rows of the extractor’s linear system.
Lemma 3.10 (Single-round recovery in the deployed rows).
Fix one round at level as in Lemma 3.4, but let the round fold the coefficient vector with the weights and the generator and evaluation vectors with the weights ,
with the cross terms named with the halves swapped relative to (13),
and the folded commitment , so that the fold identity reads by the same expansion as in §3.2. Then the conclusions of Lemma 3.4 hold with rows and the identities (likewise for , ), provided only that are pairwise distinct and nonzero. The deployed cross terms also scale their -coordinates by a challenge drawn before the rounds (“The deployed opening in full” below), which the lemma covers verbatim with replaced by .
Proof.
The fold identity is the expansion of §3.2 with the weights changed: the diagonal terms of carry the weights and , and the cross terms and carry and , which is why they are absorbed as with holding the high-with-low product. The lift (20) becomes , and preserves well-formedness since . The matrix now has rows ; multiplying the row of by gives , and the same root count, now for a polynomial of degree at most in itself, shows that the matrix is invertible exactly when the challenges are pairwise distinct. Everything else is as in the proof of Lemma 3.4. □
The two row shapes impose different hypotheses: two challenges have equal squares, so a triple containing them makes the symmetric matrix singular, while the deployed matrix remains invertible whenever the three challenges are distinct and nonzero. Over the triple , in which , has squares : the symmetric rows are , and , two of them equal, with determinant ; the deployed rows are , and , with determinant . Remark 3.9 shows that the deployed fold is the symmetric fold under the substitution , but that relabelling does not carry the hypotheses across: the squaring map is two-to-one onto the squares, so a uniform deployed challenge is not the square of a uniform symmetric one, and the condition “pairwise distinct squares” is a condition on three symmetric challenges that has no counterpart for three uniform deployed ones. Each shape is therefore analysed with its own rows. In the proof of Theorem 3.5 with Lemma 3.10 in place of Lemma 3.4, three pairwise distinct nonzero challenges suffice at each node, and each sibling avoids the earlier siblings’ challenges and .
The deployed opening in full.
The deployed opening is the masked opening of §3.6 with the deployed fold, a further challenge , and the claimed value moved into the commitment. Let , and write for the coefficient-side vector and for the structured scalars of the deployed fold throughout the rest of this subsection.
-
1.
Mask. The prover samples with and , and sends , as in §3.6.
-
2.
Two challenges. The verifier sends a uniform , and then a uniform .
-
3.
The masked commitment. Both parties replace by
(28) which, by linearity of the commitment (Crypto Guide, §“Pedersen vector commitments”, the remark that linearity survives), commits with blinder to the coefficient vector
of the polynomial , whose value at is . The claim “” has become the claim “ commits to a vector whose inner product with is ”: the value is folded into the commitment, and the opening claims the value .
-
4.
Rounds. The parties run the rounds on with the fold of Lemma 3.10, weights on the coefficients and on generators and evaluation vector, and with the -coordinates of the cross terms scaled by :
the verifier accumulates , and the prover’s blinder accumulates .
-
5.
Final message and check. The prover sends the final scalars and . The verifier accepts if and only if
(29) where and for the structured scalars of (26).
Completeness is the invariant (16) again, with in place of , the value in place of , and every -coordinate scaled by ; the final -coordinate is . Subtracting moves the claimed value into the commitment, so that the argument opens to and the check carries no term in on ; the mask leaves the opened value unchanged in either form because . The halo2 book gives the reason in its comparison with the scheme of Bünz, Chiesa, Mishra and Spooner, which adds the value on the inner-product generator instead (chapter Comparison to other work): is a fixed base, so is the cheaper multiplication inside a recursive verifier. The factor has a reason of its own. The deployed is a fixed public generator rather than a verifier’s sample drawn after (“Generators from a hash” above): a prover who knew in advance could plant a -component in or , and drawing after both re-randomises the generator that carries the inner product, so that a planted component would have to have anticipated ; Corollary 3.13 makes this precise.
Hiding in the deployed opening.
The final scalar is the linear form of (22) for this fold, taken of the masked vector:
| (30) |
the coefficient side folding with the inverse weights of the generator side as always. Unmasked, the deployed fold leaks this form as the symmetric one does (Remark 3.7): four deployed openings of without the mask, with challenge pairs , , and , end in the scalars , , and , and solving the system recovers the vector. Masked, with , and the challenges , , the masked vector is , its inner product with is , and the final scalar is with ; a second mask under the same challenges ends in , and both runs are accepted. The transcript of one opening is
Corollary 3.12 (Honest-verifier zero knowledge of the deployed opening).
Let have prime order , and let the verifier draw uniformly from and each uniformly from . There is a simulator which, given but not , outputs challenges and a transcript of the deployed opening whose distribution lies within statistical distance of the honest one.
Proof.
The proof of Proposition 3.8, with the deployed and with (29) in place of (24). Call a challenge tuple good if and is not a multiple of ; now forces and then for every , at most one challenge tuple among . For good challenges is uniform and independent of by (30) and the argument of that proof. The simulator draws the challenges, , every and every but , and and uniformly, and sets to the one point that satisfies (29), namely ; the counting of that proof shows that the two distributions agree for good challenges, and the tuples that are not good have probability at most . □
The deployed opening of the toy polynomial.
The toy’s of §3.7 is opened at with the deployed opening, using the round challenges and of Table 6; Table 7 lists both sides with every intermediate value. The verifier’s equation (29) closes at on both sides, with and in the deployed shape, and the false value moves the left-hand side to against on the right: rejected once more. The deployed run and the masked symmetric run of §3.7 open the same commitment to the same value with entirely different numbers; Remark 3.9 relates the two folds. The unmasked deployed run of Table 6 and this masked opening both close at , and that run’s equals the mask commitment : further collisions of the kind noted in §3.7, accidents of a -element group, not consequences of the mask.
| step | prover | verifier |
|---|---|---|
| mask | samples , for which , and ; sends | receives ; sends , then |
| masked vector | ; ; blinder | |
| round | halves , ; , ; cross terms , , , ; sends , | sends (); keeps ; |
| folds , , ; | ||
| round | halves , ; , ; cross terms , , , ; sends , | sends (); keeps ; |
| folds , , ; | ||
| final | sends , | ; , ; left: ; right: : accept; with : left : reject |
Corollary 3.13 (Knowledge soundness of the deployed opening).
Let , and be as in Theorem 3.5, and let be a fixed generator, uniform in like them. The deployed opening, with the check (29), is knowledge sound for : there is an extractor which, given rewindable access to any prover that makes the verifier accept with non-negligible probability, runs in expected polynomial time and outputs either a witness for or a nontrivial discrete-logarithm relation among , and . Its knowledge error is .
Proof.
The extractor branches over two values after , under each over two nonzero values , and under each of those over the rounds as in the proof of Theorem 3.5, with three pairwise distinct nonzero challenges per node; the tree has leaves, and the rewinding and running time are as in that proof.
Rounds. Fix and , and write . With in place of the rounds are those of Lemma 3.10, so the induction in the proof of Theorem 3.5 returns a representation of over with , that is, the representation over .
The challenge . Under one , the values and give representations and of the same over . If they differ, their difference is a nontrivial relation among , and . Otherwise , so and , whence : with .
The challenge . The values and follow the same and give with for . Subtracting, with , and . Substituting back, with and , and , the first entry of being . This is the witness.
The error. Beyond the of the rounds, the two branchings at the root and the exclusion of each cost . A relation among , and yields a discrete logarithm by the every-generator embedding, as at the root of Theorem 3.5. □
The bytes.
An Orchard proof is a byte string. The proofs of the Action descriptions that one transaction carries in one pool, here called a bundle, are aggregated into a single proof (protocol specification, § 4.6, “Action Descriptions”); a transaction with Actions in both the Orchard and the Ironwood pool carries one such proof for each. Its length is bytes (ZIP 225, the sizeProofsOrchard field; ZIP 229, the fields sizeProofsOrchard and sizeProofsIronwood; the consensus rule is the protocol specification’s, § 7.5, “Action Description Encoding and Consensus”), bytes for a single Action. Every Vesta point and every field element in it occupies bytes. Table 8 lists by kind, from the per-object counts of the Action circuit whose verifying key the consensus rules fix (protocol specification, § 4.6, “Action Descriptions”), every one of those bytes: a per-Action block of points and scalars, repeated for each Action, and a shared block of points and scalars. The inner-product argument’s share is the last three rows of the shared block: the blinding commitment , the pairs , which are points, and the two scalars and : points, bytes, or bytes with the scalars, once per bundle, because the complete protocol collapses every opening of every polynomial into one opening (“The multipoint opening argument” in §4). This is the only part of the proof that grows with , and it grows as points. Everything else grows with the circuit’s structure and not with : one commitment per advice column, two permuted-column commitments and one running product per lookup, the permutation running products and quotient chunks, the multipoint commitment, and one field element per claimed evaluation.
| kind | count | bytes | what it is |
| Per-Action block, once per Action | |||
| point | 10 | 320 | advice column commitments, one per advice column |
| point | 3 | 96 | permuted lookup input commitments , one per lookup (Construction 2.14) |
| point | 3 | 96 | permuted lookup table commitments , one per lookup (Construction 2.14; unrelated to the mask commitment ) |
| point | 3 | 96 | permutation running-product commitments: the equality-enabled columns in chunks of (§2.6) |
| point | 3 | 96 | lookup running-product commitments, one per lookup |
| scalar | 1 | 32 | instance column evaluation at |
| scalar | 25 | 800 | advice evaluations, one per queried rotation of each advice column (§4.4) |
| scalar | 8 | 256 | permutation product evaluations: products at and , the first also at , the rotation to the boundary row of Remark 2.17, with blinding rows (§4.6) |
| scalar | 15 | 480 | lookup evaluations: product at and ; at and ; at |
| total | 2272 | points and scalars | |
| Shared block, once per bundle | |||
| point | 1 | 32 | random polynomial commitment: a random polynomial added to blind the quotient (the complete protocol, §4) |
| point | 8 | 256 | quotient chunk commitments: constraint degree , so chunks of degree below (Theorem 4.7) |
| scalar | 29 | 928 | fixed column evaluations at , one per fixed column |
| scalar | 15 | 480 | permuted-label polynomial evaluations at , one per equality-enabled column (Construction 2.10) |
| scalar | 1 | 32 | random polynomial evaluation at |
| point | 1 | 32 | multipoint polynomial commitment: the one polynomial into which every query collapses (Construction 4.4) |
| scalar | 5 | 160 | multipoint evaluations: the value of each query group’s combined polynomial at the reduction’s fresh challenge point, one per distinct set of query points; five sets (§4.4) |
| point | 1 | 32 | IPA: the blinding commitment |
| point | 22 | 704 | IPA: the pairs |
| scalar | 2 | 64 | IPA: the final scalars and |
| total | 2720 | points and scalars | |
3.8.1 The “Halo” in Halo 2: deferring the expensive check
The verifier of this section is logarithmic everywhere but in one place. He reads points and two scalars, evaluates in field multiplications, and forms the left-hand side of (29) with scalar multiplications (, and the round terms); then he needs , one combination of all generators, group arithmetic proportional to the size of the whole circuit (§3.4). Two ways of amortising that cost follow, batch verification and accumulation, the second not deployed by Orchard; between them, the paragraph “Transparency: no trusted setup” records why the linear cost is accepted.
Batch verification.
The consensus rules require each Action proof to be valid for the verifying key of the Orchard circuit (protocol specification, § 4.6, “Action Descriptions”); validity includes the check (29) with its multi-scalar multiplication of length , and the specification composes no proofs, so the verifier pays that multiplication itself rather than passing it on. Several proofs can share it (Crypto Guide, §“Polynomial commitment schemes”, Remark “KZG versus IPA, and the Halo lineage”). Written as one multi-scalar multiplication that must evaluate to , equation (29) has terms: the generators , , , , and the points , . The equations of proofs are checked together by testing for fresh uniform drawn by the verifier.
Lemma 3.14 (Randomised batch check).
Let have prime order, let , and let be independent and uniform. If some , then .
Proof.
Fix with and condition on every with . Since has prime order, generates it, so is a bijection , and the sum equals for exactly one value of . □
Because , and are shared, their terms merge, and equations combine into one multi-scalar multiplication of terms, against when checked separately. In the complete protocol is itself a combination of commitments (§4); those of the verifying key are shared as well, and each further proof adds its own points, the of Table 8, and the instance commitments computed from its public inputs, one per Action (§4.2). The generator terms are paid once per batch. A batch check is not accumulation: it emits nothing that a later proof could consume, and it verifies the batch and stops. Both take linear combinations of deferred equations; their interfaces and guarantees differ, and the accumulation scheme of Bünz, Chiesa, Mishra and Spooner, sketched below under “Accumulation (not deployed by Orchard)”, is not part of the specified protocol.
Transparency: no trusted setup.
The generators are outputs of a public hash-to-curve map on fixed inputs (this subsection, “Generators from a hash”); the scheme has no trapdoor and requires no trusted setup, unlike KZG, whose trapdoor permits forgeries (Crypto Guide, §“Polynomial commitment schemes”, under “KZG: evaluation in the exponent”). The price is the points of Table 8, against the constant-size opening proof of KZG, and the linear verifier. ZIP 224’s motivation names the generation of the structured reference string of Zcash’s earlier proving system a point of risk within the protocol and asks for a proving system that does not require one (ZIP 224, Motivation).
Accumulation (not deployed by Orchard).
In a recursive verifier, a circuit that verifies a proof, the multi-scalar multiplication of §3.4 would cost scalar multiplications inside the circuit. Instead the claim is combined with a running claim of the same shape, , by a random linear combination with a challenge drawn after both (a verifier challenge, not a round blinder of this section; §7 keeps the letter): holds for all when both inputs hold and for at most one otherwise. The combined claim, returned to a single tuple by a prover-assisted opening, is the accumulator carried along the chain of proofs, and a single multi-scalar multiplication outside any circuit at the end discharges all combined claims. The soundness of an accumulation scheme for a closely related inner-product commitment is cited in §7 from Bünz, Chiesa, Mishra and Spooner, under the extractability of its openings, which they conjecture from the binding of the Pedersen commitment; the cycle of curves that keeps the recursive arithmetic in the right fields is the other half of Pasta. Both are developed in §7, under “Accumulation and the Halo trick” and “A cycle of curves for efficient native recursion”, where recursion and accumulation over the cycle are classified designed-but-unspecified in the sense of §1.2: the protocol specification uses Halo 2 only to prove and verify Action statements and composes no proofs.