6 The verifier’s decision and its implication chain
This section adds no theorem: it lists the verifier’s checks in the order he performs them, assembles the implication chain from an accepted proof back to the claim, each link labelled by the statement that proves it and by its error term, repeats the chain for the Orchard Action circuit, and maps the five reductions of §1.2 to the formal statements that own them. Nothing here depends on the recursion of §7, which Orchard does not deploy.
6.1 The verifier’s checks, read in order
What he holds.
The verifier of the toy holds the fixed data of the circuit, the five selector polynomials and the permuted-label polynomials of Construction 2.10; the public input, the column interpolated to (§4.2); and the proof. The proof is a byte string (§4.3): commitments, claimed evaluations, and one opening, in the order of the phases of §4.5 (Table 10), counted by kind in Table 8. He never sees a column polynomial, a blinder or the advice; he sees curve points and field elements, and he performs the checks below in this order.
-
1.
The challenges. He first commits to the instance column himself, from the public input and with the fixed blinder (§4.2), so that the public input never comes from the prover. He then replays the transcript (§4.3): he absorbs the key digest, that instance commitment and each prover message in turn, and squeezes every challenge at its prescribed point. In the toy the point was drawn by decree; in the deployed protocol the evaluation point is a hash of everything before it.
-
2.
The identity at the point. From the claimed evaluations and the fixed polynomials he evaluates himself, he forms both sides of the gate identity. In the toy this is the one field equation (5): against , accepted; the cheat of Example 2.3 gives against , rejected. In the deployed protocol the identity is , with the -combination of every constraint polynomial and the chunked quotient, and it is enforced by opening the collapsed quotient commitment at to the value that the verifier computes himself from the evaluations of phase 5, inside the multipoint opening (phases 6 and 7 of §4.5).
-
3.
The wiring. He evaluates the boundary and update identities of the permutation argument (7) at the point and, in the deployed form, the chunk-boundary identities of §2.6 and the boundary identity of Remark 2.17. In the toy the ratio of the two products (6) at is for the honest trace and for the tampered (Example 2.8).
-
4.
The tables. He evaluates the four lookup identities (9) and, in the deployed form, the boundary identity of Remark 2.17 at the point, five for each lookup argument. The toy’s grid has none; the two-bit check of Example 2.13 showed the shape, with both products equal to and the forged stranded in every arrangement. In the deployed protocol items 3 and 4 are not separate checks: their identities are summands of and are enforced by the one check of item 2; only the toy checks them separately.
-
5.
The openings. Every evaluation he received for the three checks above was claimed. He now binds each claim to its commitment: the multipoint reduction of Construction 4.4 folds every claim into one statement, and the inner-product equation (29) discharges it with one multi-scalar multiplication of length . In the toy, the opening of at to the value closes at on both sides (Table 5) and the false value moves the left-hand side to ; the deployed opening of the same commitment closes at and rejects likewise (Table 7). Among the claims is , which the opening binds to his own instance commitment (§4.2).
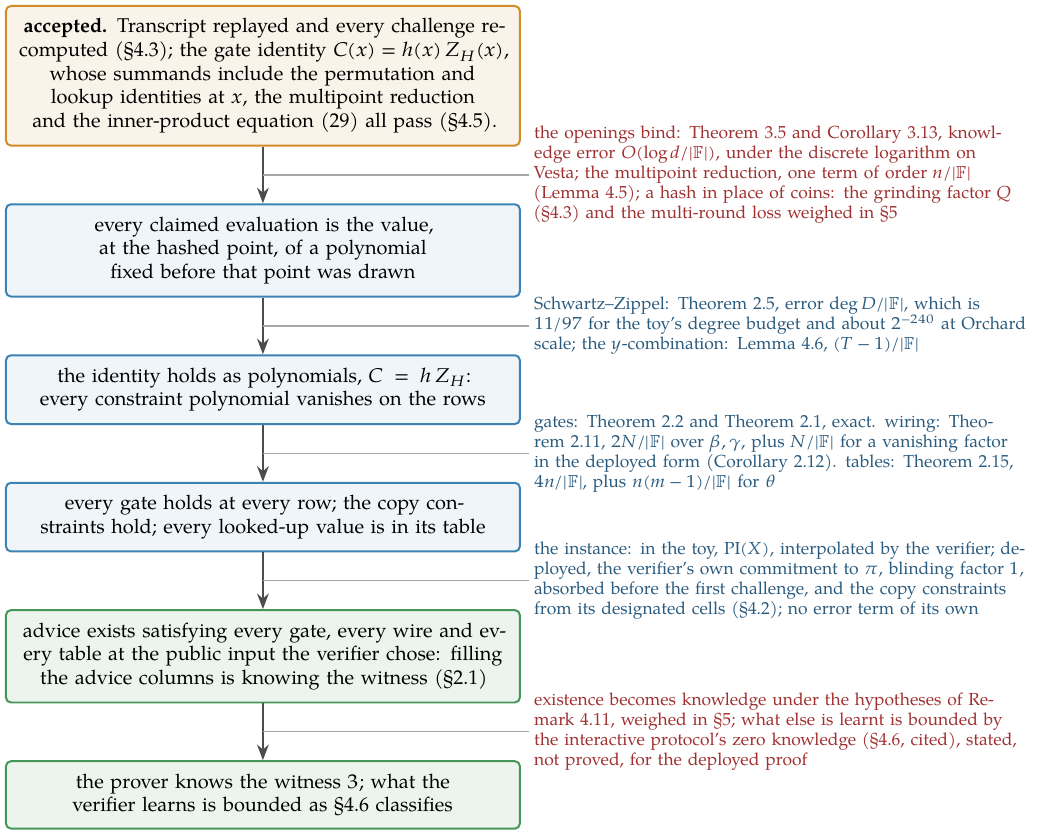
If every check passes he accepts. The accepted checks imply the following chain, read backwards from the last check to the first; Figure 17 draws it.
The chain, read backwards.
-
1.
The identity check passed at his random point. Because the commitment binds, the polynomials behind the openings were fixed before the point was chosen: the Pedersen vector commitment is binding under the discrete logarithm on Vesta (the Crypto Guide, §“Pedersen vector commitments”, recalled in §2.9), and the opening argument is knowledge sound (Theorem 3.5 and Corollary 3.13), so from any prover who passes the opening an extractor recovers the committed vector and the value it opens to, or else a discrete-logarithm relation among the hashed generators; its knowledge error is , and the multipoint reduction that fed it adds one Schwartz–Zippel allowance of order (Lemma 4.5). With a hash in place of coins the ordering holds by construction, every commitment being an input of the hash that produced the challenge testing it (§4.3). Because the point was random and a false identity disagrees with the true one at all but points, passing supports as polynomials except with the error of Theorem 2.5 for this fixed check: for the toy’s degree budget, for the particular cheat of Example 2.6, about at Orchard scale, one term in the sense §1.2 fixed. In the deployed form the identity is , and the challenge that combined every constraint into costs one more term, for constraint polynomials (Lemma 4.6).
-
2.
The identity holds as polynomials. Then , so vanishes on every row (Theorem 2.2, equivalence (3)), so every gate equation holds at every row (Theorem 2.1). Both steps are exact equivalences with no error term: in the toy, the four rows of Table 1 each satisfy (1). In the deployed form every constraint polynomial combined into vanishes on the active rows: every custom gate, and the permutation and lookup identities that the next two links consume.
-
3.
The permutation identities passed. Except with the error of Theorem 2.11 over , with the number of participating cells, twelve in the toy, and, in the deployed form, more for the challenges at which a product factor vanishes (Corollary 2.12), the copy constraints hold: the per-row gates are wired into one coherent computation, the witness of row is the witness of rows and , and each row’s output is the next row’s input. The lookup identities passed likewise: except with the error of Theorem 2.15, and more for the -compression of (10) (Proposition 2.16) when a lookup has columns, every looked-up value is in its table.
-
4.
The public input fixed the target at . In the toy, enters the gate polynomial through , which the verifier interpolates himself (§4.2), so it enters the identity of link 1. In the deployed circuit the instance polynomial of Definition 4.2 is the verifier’s own: he committed to it from the values he intends to verify against, and its designated cells are copy-constrained to the advice cells that carry the same values, so the permutation of link 3 forces agreement. There is no error term of its own. The relation certified is the one at the public input the verifier supplied (§4.2).
Together with the observation that closed §2.1, that filling the advice columns is knowing the witness, because those cells are the wires carrying it and its powers, the four links say: there exists an assignment of the advice columns, a value of the witness, making the entire arithmetisation of hold, at the public .
From existence to knowledge.
The chain so far establishes that satisfying advice exists. That the prover knows it is the extraction question. The extractor of Theorem 3.5 and Corollary 3.13 recovers, from any prover who passes the opening, the committed vector and its blinder: it establishes knowledge of committed polynomial data, and nothing more. It does not by itself prove that those polynomials encode a satisfying circuit witness; that is the upper layer’s task in the layered extraction of Remark 4.11, where the commitment scheme’s extractor turns commitments into polynomials and the polynomial IOP’s extractor turns polynomials into a witness. Under the composed hypotheses named there, a round-by-round or state-restoration knowledge-soundness theorem for the IOP, extractability and evaluation binding for the commitment scheme, and a multi-round Fiat–Shamir theorem for the transcript, an extractor for the full protocol obtains such a witness; §5 weighs those hypotheses against the deployed transcript, and in particular states in which model the tight bound is proved.
What he has not learnt.
For the interactive protocol and an honest verifier the transcript reveals nothing beyond the truth of the statement (Proposition 4.9, cited, and Corollary 4.10); for the non-interactive deployed proof this is stated, not proved (§4.6). Every commitment the prover sent is a uniform group element (perfect hiding, recalled in §4.6); the verifying key’s and the instance commitments carry the fixed blinding factor and commit only public data; the evaluations of each blinded column are uniform by Lemma 4.8; the final scalar of the opening, which folding alone would have leaked as a linear form of the coefficients (Remark 3.7), is masked by the random polynomial vanishing at the opening point (§3.6, in the deployed form of §3.8); and the joint transcript is simulated by the witness-free simulator of Proposition 4.9, within the distance of Corollary 4.10 for the deployed challenges. The toy has no blinding rows and is not zero knowledge: its claimed value alone singles out the witness among the three roots of in , and indeed among all candidates; the blinding rows of Lemma 4.8 are what make the deployed evaluations uniform. The deployed mask makes the opening’s own scalar a fresh uniform value: under one mask (Table 7) and under another (§3.8), both accepted.
The error budget.
The verifier has checked a small transcript, bytes for Actions (Table 8), and a logarithmic opening of points. Each link of the chain carries its own error term, which bounds the failure of that link alone: the identity’s (Theorem 2.5); the -combination’s (Lemma 4.6); the permutation’s (Theorem 2.11) and for the challenges at which a product factor vanishes (Corollary 2.12); the lookup’s (Theorem 2.15) and the -compression’s (Proposition 2.16); the multipoint reduction’s allowance of order (Lemma 4.5); and the opening’s (Theorem 3.5 and Corollary 3.13). Combining them into one knowledge error for the protocol is the compilation principle of Remark 4.11, whose hypotheses §5 names and does not discharge; no sum of the terms is asserted. Beyond these terms lie the loss of replacing coins by a hash, of which the grinding route alone multiplies a term by the query budget , so that becomes after attempts (§4.3, Proposition 4.3), while the multi-round transform’s full loss is weighed in §5, which asserts no factor- bound for the compiled protocol; and the assumptions beneath the chain, the discrete logarithm on Vesta that makes the commitments bind and the extractor’s alternative output infeasible (Theorem 3.5 and Corollary 3.13), the random-oracle model for the transcript hash, and the extraction model in which the non-interactive bound is proved (§5). The isolated is not the verdict’s error: it is one Schwartz–Zippel term for one fixed lie, read as §1.2 fixed.
6.2 The Action circuit at deployed scale
Nothing in the chain used that the statement was small. Replace the four gates by the constraints of the Orchard Action statement, the nine conditions the protocol specification imposes on the public input and the witness (protocol specification, § 4.18.4, “Action Statement (Orchard)”): the integrity of the old and new note commitments, the Merkle path from the spent commitment to the anchor unless the spent value is (the Crypto Guide, §“Merkle trees and commitments to sets”), the opening of the net value commitment, a Pedersen commitment to the value difference (the Crypto Guide, §“The Pedersen commitment”), the nullifier’s derivation, the spend authority, that the randomised verification key is the re-randomisation of the spend validating key by a witnessed randomiser (the Crypto Guide, §“Key re-randomisation and unlinkability”), the integrity of the diversified address, that the spent note’s address satisfies for the incoming viewing key derived in the witness from and further key material (the Crypto Guide, §“Shielded-note delivery as deployed hybrid encryption”) unless that derivation fails, and the two enable flags, which force the spent value to unless and the created value to unless . From NU6.3 the circuit checks a tenth condition on the further public bit (§ 4.6; ZIP 258): when it is set, the receivers of the spent and created notes coincide (§4.2). Each condition unfolds into the gates of the deployed circuit (§4.1), and the grid grows accordingly (Table 11): the four rows become ; the one universal gate of degree becomes custom gates reading rotations, under the degree bound , the incomplete addition of Theorem 4.1 among them; the quotient of degree becomes of degree up to , cut into chunks (Theorem 4.7); the four-class permutation on twelve cells becomes fifteen equality-enabled columns in three running products; a Sinsemilla generator table of rows, reached by three lookup arguments, joins the permutation (§4.1.3; the hash is the Crypto Guide’s, §“Sinsemilla: an algebraic hash-based commitment”); the four openings at become claimed evaluations per Action and shared (Table 10), collapsed into one opening of points; and the point drawn by decree becomes an squeezed from the BLAKE2b transcript. The spine is identical: arithmetise into a grid, interpolate the columns, compress “all rows correct” into one identity, in the toy and in the deployed protocol, commit, and test at a random point.
| the toy | the Orchard Action | |
|---|---|---|
| field | , a prime of bits | |
| commitment group | over , points (§3.7) | Vesta, of order (§3.8) |
| rows | , | |
| columns | advice, selectors, instance | advice, fixed, instance (§4.1) |
| gates | one universal gate (1), degree , rotation | custom gates at rotations, (Definition 2.7; the deployed value, §4.1.4) |
| identity | ; , | with the -combination; , chunks (Theorem 4.7) |
| wiring | a permutation of twelve cells, four copy classes (, fixed), one running product (§2.6) | fifteen equality-enabled columns, three running products |
| table facts | none on the grid; Example 2.13 | three lookup arguments into a -row Sinsemilla table (§4.1.3) |
| the point | , by decree | squeezed from the BLAKE2b transcript (§4.3) |
| one-term error | ; for the cheat | about ; after grinding attempts |
| openings | at ; four cross-term points and per opening (§3.7) | claimed evaluations per Action and shared, one opening of points (Tables 10 and 8; the collapse, Construction 4.4) |
| proof | — | bytes, for one Action (Table 8) |
The algebraic core of Action verification.
For the verification of an Action proof that the consensus rules require (protocol specification, § 4.6, “Action Descriptions”), the randomised polynomial-identity test of link 1 is the algebraic core: a Schwartz–Zippel argument on one identity at one hashed point. The full verifier of §4.5 evaluates that identity’s permutation and lookup summands from the claimed evaluations, binds every claimed evaluation through the multipoint reduction, recomputes every transcript challenge, and closes the single inner-product equation with its one multi-scalar multiplication of length , before concluding that the circuit’s constraints hold at the public input it verified against, the anchor, the net value commitment, the nullifier, the randomised verification key, the extracted note commitment and the flags of §4.2. Under the knowledge soundness whose status §5 classifies (designed-but-unspecified for the deployed transcript), an accepted Action proof certifies, for a known witness, that the constraints of the circuit whose verifying key the consensus rules fix (protocol specification, § 4.6) hold. That these imply the conditions of the Action statement (protocol specification, § 4.18.4) is a property of that circuit, which this volume does not verify and which the specification records as having failed for the Orchard circuit deployed before NU6.2 (the same section); value balance additionally requires the binding signature (protocol specification, § 4.14, “Balance and Binding Signature (Orchard)”), and privacy rests also on components outside the proof, such as note encryption.
What the formal treatment supplies.
Each of the five reductions of §1.2, “The chain of reductions”, is owned by a formal statement. Table 12 lists, reduction by reduction, what the toy exhibited and which statement carries it; the last two rows point beyond the spine, to the extractor that turns existence into knowledge and to the recursion, which Orchard does not deploy and on which nothing above depends.
| reduction | the toy exhibits | the statement that owns it |
|---|---|---|
| computation grid | Table 1, Figure 2; knowing the witness is filling the advice | Definition 2.7 (§2.1, §2.5) |
| grid polynomials | the nine interpolants; of degree vanishing on | Theorem 2.1 (§2.2) |
| vanishing identity | of degree ; the gap | Theorem 2.2 (§2.3) |
| identity one random check | accepted; and ; Figure 3 | Theorem 2.5 (§2.4); Lemma 4.6 and Theorem 4.7 (§4.5) |
| random check committed openings | ||
| binding | sealed in | the Crypto Guide, §“Pedersen vector commitments”, recalled in §2.9 |
| the opening | Tables 4 and 5; rejected | Construction 3.2, Theorem 3.3, Lemma 3.4, Theorem 3.5, Corollary 3.13 (§3) |
| the wiring | product honest, with | Theorem 2.11 (§2.6) |
| the tables | ; the forged stranded | Theorem 2.15 (§2.8) |
| the public | Definition 4.2 (§4.2) | |
| the removed verifier | by decree against by hash; | the Crypto Guide, §“The Fiat–Shamir transform: from interactive to non-interactive”, applied in §4.3 |
| many openings, one | — | Construction 4.4 and Lemma 4.5 (§4.4) |
| hiding | the leaked linear form; against | Remark 3.7 and the mask (§3.6, §3.8); Lemma 4.8 (§4.6) |
| the pattern | — | Remark 4.11 and “The map onto the phases” (§4.7) |
| “the prover knows the witness” | — | the extractor in the algebraic group model and the Fiat–Shamir loss (§5, “The algebraic group model”) |
| beyond the spine | — | the accumulation fold, Proposition 7.5, the accumulation scheme cited as Theorem 7.4, and recursion over the cycle of curves, none deployed by Orchard, which uses one direction of the cycle only (§7.3, “Accumulation and the Halo trick”; §7.4, “The half Orchard uses”) |