7 Key agreement
This section constructs Diffie–Hellman key agreement between two parties that share no prior secret and develops it into the hybrid public-key encryption by which shielded notes are delivered. It proves that the passive security of Diffie–Hellman equals the DDH advantage exactly (Theorem 7.11), that no hardness assumption on the group prevents a man-in-the-middle attack on the unauthenticated protocol (Proposition 7.14), that hybrid encryption is passively secure under CDH, with the key-derivation function modelled as a random oracle and the AEAD secure (Theorem 7.24), and that ElGamal encryption is key-private under DDH (Theorem 7.28), a property that carries over to note encryption (Remark 7.29) and hides the recipient of a ciphertext published permanently on the ledger.
7.1 The Diffie–Hellman protocol
The protocol rests on the asymmetry of Section 2.
In a cyclic group
is a group isomorphism evaluated in group operations by repeated squaring but believed infeasible to invert in the groups this volume uses; inverting it is the discrete logarithm problem (Definition 2.2). The section depends only on the group structure and the hardness of problems in it, not on the presentation of the group; the reference instances are a large prime-order subgroup of and the elliptic-curve point groups of §7.6. Diffie and Hellman observed that this asymmetry suffices for two parties with no prior shared secret to establish one over a public channel.
Construction 7.1 (Diffie–Hellman key exchange).
Fix public parameters with
-
1.
Alice samples
uniformly, computes , and sends to Bob. -
2.
Bob samples
uniformly, computes , and sends to Alice. -
3.
Alice computes
; Bob computes .
The value
Proposition 7.2 (Correctness of Diffie–Hellman).
In Construction 7.1 both parties compute the
same group element,
Proof.
Unwinding the definitions,
where
The shared secret is a function of the transcript , computable by anyone who knows one of the two private keys and, conjecturally, by no one who knows only the public shares; §7.4 makes the conjecture precise.
Remark 7.3 (Small subgroups and the prime-order rule).
If has small subgroups, an adversary who substitutes an element
of small order for a public share confines the victim’s computed
secret to a small subgroup and learns the victim’s exponent modulo a
small factor of —the
Pohlig–Hellman leakage of
Corollary 2.21 in protocol form. The
remedy is the standing rule of Section 2: prefer
of prime order . Then the only subgroups are
and itself, every non-identity element is a
generator, and no nontrivial confinement is possible. When the
ambient group does not have prime order—
has composite order
7.2 Static and ephemeral keys
Construction 7.1 leaves the lifetime of a key pair unspecified, and the properties of the protocol depend on it.
Definition 7.4 (Static and ephemeral keys).
A Diffie–Hellman key pair is static (long-term) if it is generated once and reused across many sessions, typically published and bound to an identity; it is ephemeral if it is generated freshly for a single session and discarded immediately afterwards.
Three protocol shapes result; all three are used below.
-
•
Ephemeral–ephemeral (DHE). Both parties use fresh keys. Once and are erased, no one—the parties included—can recover : this is forward secrecy, the guarantee that a later compromise of all stored long-term state cannot decrypt recorded past sessions, because the only secrets that ever existed were the deleted ephemerals.
-
•
Static–ephemeral. The recipient Bob holds a static pair
, with known in advance; Alice contributes a fresh ephemeral . The shared secret then requires no interaction from Bob at agreement time: Alice computes from the published , attaches , and sends everything in a single flow; Bob recovers whenever he next comes online. This is the shape of hybrid encryption (§7.7) and of shielded-note delivery (§7.9): sender online once, recipient possibly offline, no round trip. -
•
Static–static. Both keys are long-term, so is a fixed function of the two identities—the same in every session. There is no forward secrecy, and the fixed secret must be combined with fresh per-session randomness (a nonce) before it may key any symmetric scheme; using it directly would reuse one key across all time.
In the static–ephemeral shape a static public key
7.3 The key-agreement scheme abstraction
We package the non-interactive (static–ephemeral) pattern as a scheme with named algorithms, so that later constructions, including deployed note encryption, invoke key agreement independently of the underlying group.
Definition 7.5 (Key-agreement scheme).
A (non-interactive) key-agreement scheme over a public parameter set consists of a private-key space , a public-key space , a shared-secret space , and three algorithms:
-
•
, randomised, outputting a private key ; -
•
, deterministic, mapping a private key to its public key ; -
•
, deterministic, mapping one’s own private key and a counterparty’s public key to a shared secret .
Correctness demands that for all and all
| (1) |
Construction 7.6 (Diffie–Hellman as a key-agreement scheme).
Fix
Correctness is exactly
Proposition 7.2:
Remark 7.7 (The deployed interface generalises the base point).
Zcash note encryption is specified against this abstraction with one generalisation: the deployed takes the base point as an explicit argument rather than fixing a protocol-wide generator, so that Sapling and Orchard derive keys over per-address diversified bases (protocol specification §“Key Agreement”). Those bases are used in §7.9; the address construction that produces them belongs to a later volume. Because the interface never inspects the underlying group, the same construction has carried over across three groups: Sprout’s Curve25519, Sapling’s Jubjub, and Orchard’s Pallas.
Remark 7.8 (The abstraction boundary, and what falls outside it).
Any concrete scheme satisfying equation (1) can be swapped in without changing the surrounding logic: a prime-field group, an elliptic curve, or a post-quantum non-interactive key agreement such as the CSIDH group action. A key-encapsulation mechanism (KEM), by contrast, cannot satisfy the correctness equation: encapsulation requires the recipient’s public key before it can produce its ciphertext, so no counterparty-independent exists. The static–ephemeral one-flow pattern generalises to any KEM, with the encapsulation ciphertext in the role of the ephemeral public key, but only through a different interface.
7.4 Passive security and the Diffie–Hellman assumptions
A passive adversary, or eavesdropper, reads the channel without altering it; its view of an honest session is the transcript , and §2.2 formalises its task in two ways. The computational problem is to produce the shared secret: writing for the success probability of in the CDH game of Definition 2.4,
The decisional problem is to distinguish
from with
advantage
(Definition 2.5). The hierarchy
Remark 7.9 (A concrete DDH break: the Legendre symbol).
Take
Definition 7.10 (Passive security of a key-agreement scheme).
For a key-agreement scheme over and an adversary , the game runs as follows.
-
1.
The challenger samples
independently and computes the transcript -
2.
It sets
, samples uniformly, draws a hidden bit , and sends the transcript together with . -
3.
The adversary outputs a bit .
The advantage is
Theorem 7.11 (Passive security of Diffie–Hellman).
For the scheme of Construction 7.6 with uniform on , every adversary satisfies
identically and with running time preserved exactly. Under the DDH assumption the shared secret of an honest ephemeral–ephemeral session is therefore pseudorandom given the transcript: a passive adversary learns nothing about it that it could not have guessed about a random group element.
Proof.
The two games are the same game. In
for , the transcript
is with
Remark 7.12 (Why pseudorandomness, not mere unpredictability).
Every use of a Diffie–Hellman secret in this volume feeds it into a key-derivation function to produce a symmetric key. Hardness of CDH guarantees that the secret is hard to produce in full, not that it lacks efficiently predictable structure such as the Legendre leak of Remark 7.9. Hardness of DDH guarantees that the secret is indistinguishable from a random group element (Theorem 7.11): no predicate of it is efficiently computable from the transcript. In practice one often assumes only CDH and models the hash-based KDF as a random oracle: the derived key is then uniform unless the adversary queries the oracle at the hidden shared secret (Theorem 7.24). Either way the goal is a derived symmetric key indistinguishable from uniform, the hypothesis every theorem of Section 6 consumes.
7.5 Active attacks and the role of authentication
Passive security is the strongest guarantee the bare protocol offers; the following attack by an adversary who controls the channel shows that it does not suffice for a secure channel.
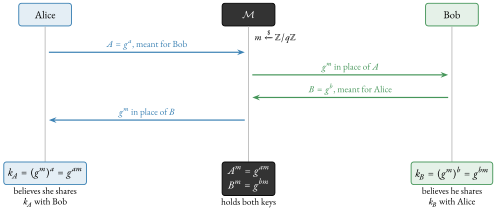
Definition 7.13 (Man-in-the-middle attack on unauthenticated Diffie–Hellman).
An active adversary controlling the channel between
Alice and Bob runs two independent Diffie–Hellman sessions, one with
each victim. It samples
Figure 10 draws the two sessions.
Proposition 7.14 (The attack defeats unauthenticated Diffie–Hellman).
After the attack of Definition 7.13, Alice and Bob each hold a secret they believe is shared with the other but is shared instead with ; and , knowing both and , can decrypt, read, modify, and re-encrypt every subsequent message in each direction, transparently to both parties. No assumption on —not even ideal hardness of the discrete logarithm problem—prevents this.
Proof.
Correctness of Diffie–Hellman (Proposition 7.2), applied once per session, gives agreement between Alice and on and between Bob and on . The adversary knows its own exponent and received both and , so it computes both secrets directly—no problem instance is ever inverted, which is why no hardness assumption is relevant. Neither victim verifies the origin of the group element they received; each transcript is a syntactically valid run of Construction 7.1, so nothing in either party’s view distinguishes the attacked execution from an honest one. With and in hand, decrypts traffic from Alice under , re-encrypts it under for Bob, and symmetrically in reverse, modifying it arbitrarily in between. □
Passive security concerns the secrecy of the shared secret; active security additionally requires the authenticity of the public shares, since confidentiality gives no protection on a channel established with the wrong party. The bare protocol (Construction 7.1) provides no authentication—nothing in or identifies its sender—so the remedy must bind each public share to its sender’s identity, letting the recipient reject a substituted share.
Remark 7.15 (Three mechanisms supply authentication).
Deployed remedies fall into three families, each external to the bare exchange.
-
1.
Signed Diffie–Hellman. Each party signs its ephemeral share with a long-term signing key whose verification key is certified—by a certificate authority (a third party whose signature on the key the parties already trust) or by trust-on-first-use (accepting the first key seen and rejecting later changes). The adversary of Proposition 7.14 cannot forge Alice’s signature on , so the substitution is rejected. Digital signatures are the subject of Section 8; this composition is the structure of authenticated TLS.
-
2.
Static keys that are themselves authenticated. If Bob’s static public key
reaches Alice authentically—a trusted directory, a pinned key—then a static–ephemeral exchange towards already authenticates Bob to Alice: only the holder of can complete it. This authenticates the recipient, not the sender. It is the model relevant to public-key encryption, and to shielded-note delivery, where the recipient’s address is an authenticated public key (§7.9). -
3.
Out-of-band verification. The parties compare a short fingerprint of the exchanged public keys over a channel that is authentic even if low-bandwidth—digits read aloud on a call, a QR code scanned in person.
In every case the key-agreement goal remains the passive guarantee of Theorem 7.11; authentication is a separate layer composed around the exchange, not a property of the group operation.
7.6 Elliptic-curve Diffie–Hellman
This subsection instantiates the preceding constructions on the
elliptic-curve groups of the deployed protocol. Recall from the
Math Guide (§“Elliptic curves”) that an
elliptic curve over a field of characteristic neither
nor is given in short Weierstrass form
Construction 7.16 (ECDH).
Fix an elliptic curve , a base point
The shared secret of parties with private keys and is
Proof.
Scalar multiplication is cyclic-group exponentiation in additive
notation: the group is abelian, and acts on
through because
Remark 7.18 (Why elliptic curves).
Well-chosen elliptic-curve groups admit only the generic attacks of §2.4, whereas index calculus solves the discrete logarithm in in subexponential time (Remark 2.18); a -bit curve therefore delivers the security level that a multi-thousand-bit prime field requires (Example 2.17). That efficiency, together with the availability of curves engineered for cheap in-circuit arithmetic, is why the Pallas curve of §2.6 underlies Orchard.
Remark 7.19 (Subgroup and curve validation).
A recipient computing on an attacker-supplied point must guard against two attacks, the elliptic-curve forms of the validation duty in Remark 7.3.
-
1.
Invalid-curve attack. The received coordinates may satisfy not ’s equation but that of a different, weaker curve which shares the same addition formulas (the chord and tangent slopes of the Math Guide, §“Explicit affine formulas”, involve but never ); scalar multiplication then proceeds without error in the wrong group, whose order may be smooth. The implementation must check the curve equation on every incoming point.
-
2.
Small-subgroup attack. When the cofactor
, an adversary submits a point of small order dividing , confining to a tiny subgroup and learning modulo a small factor. The defences are cofactor clearing—multiply incoming points by —or choosing a curve with .
Prime-order curves such as Pallas have
7.7 Hybrid public-key encryption
Hybrid public-key encryption (HPKE) composes three parts: key agreement in the static–ephemeral flow of §7.2, so that the recipient need not be online; a key-derivation function, which turns the shared secret, a structured group element rather than a uniform string of key bits, into a symmetric key; and an authenticated cipher, which transports the message. The two symmetric ingredients are those of Section 6, recalled below in the shape the composition needs.
Definition 7.20 (KDF, recalled and specialised).
In this section a key-derivation function is a deterministic function
mapping input keying material
Definition 7.21 (AEAD, recalled).
An authenticated encryption scheme with associated data with
key space —matching the KDF output—is a pair
with
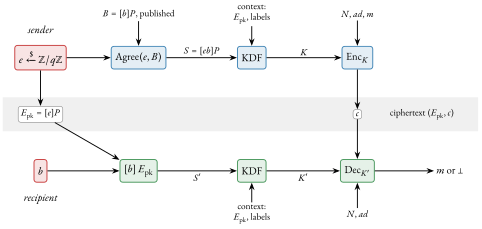
Construction 7.22 (DH-based hybrid public-key encryption).
Fix ECDH over
-
1.
sample an ephemeral
and set ; -
2.
compute the shared secret
; -
3.
derive the symmetric key
, where includes and the protocol’s labels; -
4.
output with
for a fixed or derived nonce —fixed is safe because each is used once.
To decrypt with : compute
Figure 11 draws both directions of the construction.
Theorem 7.23 (Correctness of hybrid encryption).
For every message and every honestly generated ciphertext of Construction 7.22, decryption returns .
Proof.
Theorem 7.24 (Passive security of hybrid encryption).
Model the KDF as a random oracle
(Definition 3.13) and let the AEAD be secure in the
sense of Definition 6.15. Consider a passive
adversary who sees the public key and a single
challenge ciphertext: it names two equal-length messages
for explicit reductions against CDH and against the AEAD’s authenticated-encryption security (of which the proof consumes only the confidentiality half, so is the CPA advantage of Definition 6.4 read against the AEAD), each running in essentially the same time as .
Proof.
The proof is a game hop.
Game 0 is the real CPA game: the challenge ciphertext is
with
Game 1 replaces by an independent uniform -bit string, leaving everything else unchanged.
The hop. In the random oracle model the two games proceed
identically unless the adversary queries the oracle at exactly the
point
The factor is a guessing-type security loss in the tightness taxonomy of Definition 1.22. Assuming gap-CDH—CDH hardness even given a DDH-decision oracle, which would let test each query—restores tightness; the loose bound is stated because it is the bound plain CDH yields.
Game 1 analysed. In Game 1 the AEAD key is uniform and
independent
of everything else in the adversary’s view, which is exactly the
hypothesis of the AEAD’s confidentiality game. The reduction
forwards to its AEAD challenger,
embeds the returned ciphertext as alongside a self-generated
, and relays ’s guess; the AEAD
challenger’s hidden bit plays , so
Accounting. The difference-form advantage of
Definition 6.4 is twice the bit-guessing
advantage
the stated bound.
Alternative hypothesis. The random oracle can be replaced, but not by Definition 6.24 alone: that guarantee is stated for a uniform independent salt, which the specialised KDF of Definition 7.20 omits, and the definition denies any generic unsalted guarantee. The replacement needs an explicit hypothesis on the deployed function—the narrower premise Definition 6.24 allows for unsalted use: for a uniform group element , the output is computationally indistinguishable from a uniform -bit string given the context. Under that hypothesis and DDH in place of CDH, Theorem 7.11 first replaces the shared secret by a uniform group element at cost , and the stated indistinguishability then replaces by a uniform string—no oracle and no factor, at the price of the stronger decisional assumption on the group and an explicit pseudorandomness assumption on the KDF. □
Remark 7.25 (Necessity of each component).
Omitting any component of Construction 7.22 breaks the composition.
-
•
Without the KDF, one would key the cipher with the raw group element . Its bit-representation is non-uniform—curve points do not fill the encoding space—and in non-DDH groups it is partially predictable, the Legendre-symbol leakage of Remark 7.9 being the classical instance. The KDF standardises the format, extracts uniform bits, and, by folding into its context, ties the derived key to this particular ephemeral share.
-
•
Without AEAD integrity, a passively confidential but malleable cipher would let an active adversary tamper with undetectably—the stream ciphers of Section 6 are fully XOR-malleable. Ciphertext integrity (Definition 6.14) makes any modification decrypt to except with negligible probability, giving the symmetric payload its chosen-ciphertext robustness.
-
•
Without the ephemeral key—a static–static variant—every message to would begin from the same shared secret. The fresh per-message ephemeral, with bound into the KDF context, gives each ciphertext separate key material, so nothing relies on nonce uniqueness under a reused key. What it does not supply is forward secrecy against later compromise of the recipient’s static key : from a recorded , an attacker who learns recomputes and with it the ciphertext’s key. Erasing provides only the sender-side guarantee that the key derives from no stored secret of the sender.
7.8 Key privacy
Theorem 7.24 bounds what an eavesdropper learns about the message, not about the recipient: a scheme may hide the message perfectly and still reveal the recipient’s key in every ciphertext, which an observer of the ledger can test against every public key it can enumerate. Key privacy, due to Bellare, Boldyreva, Desai, and Pointcheval, rules this out. We define it for a generic public-key scheme and prove it for ElGamal encryption, the bare static–ephemeral flow with the message folded in, on whose key privacy later volumes rely.
Definition 7.26 (Key privacy under chosen-plaintext attack, IK-CPA).
A public-key encryption scheme over
consists of a randomised
-
1.
The challenger samples
independently and sends . -
2.
The adversary outputs a message .
-
3.
The challenger draws a hidden bit
and sends . -
4.
The adversary outputs a bit .
The advantage is
Construction 7.27 (ElGamal encryption).
Fix
-
•
: choose as above and
; output and with . -
•
: sample
; output . -
•
: output
.
Correctness is the scalar identity in the proof of
Proposition 7.17, valid for any base
in :
Theorem 7.28 (ElGamal is key-private under DDH).
For ElGamal over (Construction 7.27,
either base variant), every adversary yields two
distinguishers
Under the DDH assumption ElGamal is therefore IK-CPA: a ciphertext is computationally independent of the public key it was made for.
Proof.
The proof is a hybrid through a game that uses no key at all. Write
and for the IK-CPA game with
fixed to and to , and
The hop
generates honestly, and hands
the pair . For
invertible the base is uniform on
and outputs ’s bit. If
The hop
Remark 7.29 (Key privacy of note encryption and diversified addresses).
The hybrid argument carries over unchanged to
Construction 7.22: planting the challenge in
the recipient’s key and the ephemeral share exactly as above makes
the shared secret uniform, and once it is, the pair
with
7.9 Shielded-note delivery as deployed hybrid encryption
Shielded-note delivery in the deployed protocol is the composition assembled in this section, run in band on the public ledger.
Remark 7.30 (Note delivery is HPKE on the ledger).
A shielded address embeds a static public key
by the personalised BLAKE2b call of §6.6, and AEAD-encrypts the note plaintext—a version byte, the recipient’s diversifier, the value, the note’s random seed, and the memo—under with ChaCha20-Poly1305 (Construction 6.18), attaching the ciphertext to the transaction (protocol specification §“Encryption (Sapling and Orchard)”). The nonce is fixed to zero and the associated data is empty (§“Symmetric Encryption” there), safe because each keys exactly one encryption.
Chain scanners see in every shielded output,
but lacking they learn nothing
(Theorem 7.24). The recipient
trial-decrypts: for each incoming transaction it derives
The signatures that authorise the transaction carrying the note ciphertext are the subject of the next section.