3 Keys and addresses
This section constructs the key components of the protocol specification, §“Orchard Key Components”, from the instances of §2: the spending key and the spend-side secrets, the viewing keys, and the diversified addresses. It states each assumption that their security needs at its first use and proves, in Proposition 3.18, four one-way separations between key tiers.
3.1 The spending key and the spend-side secrets
Remark 3.1 (Scope of the key derivations).
Every derivation of this section is that of a key generated with , where is the Boolean key-generation flag of ZIP 2005. ZIP 2005, §“Changes to the Protocol Specification”, item §4.2.3, specifies, as a change to the specification’s §“Orchard Key Components” and not in that section itself, an alternative source of and , with derived as here; it yields components of the same types, and again of even -coordinate. The volume does not construct the alternative and names none of its intermediate keys. Assumption 3.13, Propositions 3.18, 3.17, 6.10 and 10.6, Proposition “Confidentiality of the outgoing ciphertext” (§10.3), and the hypotheses on honest key generation of Theorems 12.9 and 12.12 are stated for only. For such keys every key component is a deterministic function of the spending key .
Definition 3.2 (Spending key and key generation).
The spending key is a uniformly random -bit string, identified with a -byte string (protocol specification, §“Constants”). Key generation draws , derives from it the components of this section, and discards and draws a new one when (below), when (§3.2), or on the one further condition of the protocol specification, §“Orchard Key Components”, which concerns the internal key of ZIP 32, a key this volume does not construct, and is stated in §3.2. A spending key that key generation does not discard is accepted; it determines every other component of a key generated with .
Construction 3.3 (Spend-side secrets).
For a spending key , the spend authorising key , the nullifier deriving key and the trapdoor of are
(protocol specification, §“Orchard Key Components”). The three lead bytes are rows of Table 3. Key generation discards if .
The scalars and lie in , the scalar field of the Pallas group, because each multiplies a Pallas point: the generator below, the blinding base of (§3.2). The key is an element of the base field .
The three inputs of have distinct lead bytes. By Lemma 2.15, under Assumption 2.12, the triple computed from a uniform , before rejection and before the normalisation below, is therefore computationally indistinguishable from independent uniform elements of , and , up to an additional statistical distance of three reduction distances, each below (§2.3).
Construction 3.4 (Spend validating key and sign normalisation).
Let (Table 2), the generator of the spend-authorisation signature scheme (protocol specification, §“Spend Authorization Signature (Sapling and Orchard)”). For :
-
1.
compute the point ;
-
2.
if its -coordinate is odd, that is, if bit of the star encoding is , replace by ;
-
3.
let for the updated , and .
The spend validating key is the point together with its -coordinate , a field element (protocol specification, §“Orchard Key Components”).
After step 2 the point has even -coordinate. The point is not , since and generates a group of prime order, so with (§2.1, on the star encoding). Replacing by replaces by , and the representatives and have opposite parities because is odd.
3.2 Viewing keys
Definition 3.5 (Full viewing key).
The full viewing key of an accepted key is the triple
with the field element of §3.1; the point is recomputed from by the even- lift.
Construction 3.6 (Incoming viewing key scalar).
With the key commitment of §2.4 and ,
Explicitly, let be the Sinsemilla hash point of the -bit message under the domain z.cash:Orchard-CommitIvk-M, and let
be the blinding base; then if , and otherwise. Key generation discards when , so an accepted key has . Because , this integer is a non-zero element of , the scalar that multiplies the diversified base in §3.3.
Let . The set has elements (§2.4, Definition “The key commitment”), and an accepted lies in it. The blinding base is not : the protocol specification, §“Sinsemilla commitments”, states that the commitment is distributed as a uniform point for a uniform trapdoor, which holds only for a blinding base other than .
Lemma 3.7 (Distribution of ).
Let be uniform on and independent of , and let . Then is with probability and otherwise uniform on , independently of .
Proof.
In particular is not uniform on (protocol specification, §“Orchard Key Components”, note).
The further rejection condition of key generation concerns the internal key of ZIP 32, §“Orchard internal key derivation”. That key has the same and and a trapdoor that is an efficiently computable function of , and key generation discards when its incoming viewing key is or (protocol specification, §“Orchard Key Components”).
Proof.
A single draw is rejected only if , of probability ; or ; or , of probability by Lemma “Distribution of ”; or . The value commits to the message of , so it is exactly when . The event has negligible probability under Assumptions 2.22 and 2.8: an algorithm that samples and outputs the message finds a input with that probability, which Proposition 2.24(iii) bounds. For , exactly when (Lemma 2.3). By (1), with (Table 4), this is a relation among , the and whose coefficient on the first is , non-zero modulo . An algorithm that samples , computes and outputs this relation succeeds with the probability of the event, which the lemma on relations among fixed generators (§2.4) bounds under the same assumptions. The rejection event is efficiently decidable from the three outputs of , so by Lemma 2.15 a first draw from a uniform is also rejected with negligible probability. Key generation outputs its first draw whenever that draw is accepted; its output is therefore within that negligible probability, in statistical distance, of a single draw without rejection. □
The proofs of this section analyse a single draw and add the statistical distance bounded by this lemma, under Assumptions 2.12, 2.22 and 2.8.
Construction 3.9 (Diversifier key and outgoing viewing key).
Let and
a -byte string, where encodes the field elements and as -byte little-endian integers. The diversifier key is the first bytes of and the outgoing viewing key the last bytes (protocol specification, §“Orchard Key Components”; row of Table 3). One output of , keyed by the encoding of , yields both.
Proof.
Equal extracted values come from commitment points , with (Lemma 2.4). If the messages differ, both cases are excluded by Proposition 2.24(ii), since is injective on integer representatives. If the messages agree, then , the case gives , impossible for in a group of prime order, and the case is excluded by the same proposition. □
Hence is bound to the pair , and so is every address of the key (§3.3): its transmission key with determines , an integer below . The binding is used in Lemma 12.5 (“Double-spend resistance”, §12.2) and Theorem 12.9 (“Authorisation of spends”, §12.3). Binding alone would follow from any collision-resistant hash of ; the trapdoor adds hiding.
Remark 3.12 (Hiding of and the double use of ).
For uniform and independent of every other quantity, is independent of by Lemma “Distribution of ”. The derivation of is keyed by the same , so once or is known that argument no longer applies, and modelling only as a PRF does not restore it: the key of row is also the trapdoor of , outside the hypothesis of Lemma 2.15 (§2.3; protocol specification, §“Orchard Key Components”, note on the use of as both trapdoor and key). The volume states the joint assumption on Pallas scalar multiplication and that the specification proposes as Assumption 3.13.
Assumption 3.13 (Joint hiding of the viewing keys).
For keys with : for every , given to the distinguisher, and uniform on , the triple computed from by the constructions of this subsection is computationally indistinguishable from
where is uniform on and , are uniform -byte strings, all independent. It is a precise form of the joint assumption that the protocol specification proposes (§“Orchard Key Components”, note); it is not perfect hiding. Results apply it after Lemma 2.15 (Assumption 2.12) has made uniform and independent of , averaging over the key-generation distribution of . It is used by Propositions 3.18, 3.17, 6.10 and 10.6, by Proposition “Confidentiality of the outgoing ciphertext” (§10.3) and by Theorem 12.12.
3.3 Diversified addresses
Construction 3.14 (Diversified address).
For an index chosen by the key holder:
-
1.
the diversifier is , the FF1 mode of NIST SP 800-38G over AES-256 with key , radix , length and the empty tweak (Crypto Guide, §“Format-preserving encryption and FF1”, Construction “The FF1 mode of NIST SP 800-38G”; protocol specification, §“Pseudo Random Permutations”);
- 2.
-
3.
the diversified transmission key is , with read as a scalar (§2.1).
The address is (protocol specification, §“Orchard Key Components”).
The map packs into bytes, eight bits at a time, least significant bit first (§2.1). Every index yields an address. The map returns a point for every input, and replaces the identity by the fixed fallback point, which is not the identity: the protocol specification types into the non-identity points. The fallback case has negligible probability under Assumption 2.8. Hence for every , and because is a non-zero scalar and the group has prime order. For each key the map is a permutation of the -bit strings (Crypto Guide, §“Format-preserving encryption and FF1”, Proposition “FF1 is a keyed bijection on ”), so distinct indices give distinct diversifiers: one incoming viewing key yields distinct addresses, all with transmission keys under the same . No index is excluded.
Assumption 3.15 (FF1-AES256 as a pseudorandom permutation).
For a uniform -bit key, with the empty tweak on is a pseudorandom permutation: no efficient adversary with oracle access distinguishes it from a uniformly random permutation of (Crypto Guide, §“Pseudorandom functions and permutations”, Definition “Pseudorandom permutation”, and §“Format-preserving encryption and FF1”, Definition “Format-preserving encryption”). It is the security requirement of the protocol specification, §“Pseudo Random Permutations”, whose note records that the distinguishing attack of Dunkelman, Kumar, Lambooij and Sanadhya at this domain size and round count is no better than exhaustive search for the -bit key. It is used so that a diversifier reveals neither its index nor the key that produced it, in Proposition 3.17 (“Unlinkability of diversified addresses”).
Assumption 3.16 (DDH on Pallas).
Let be a generator of , let and be uniform on and uniform on (§3.2), all independent. The triples and are computationally indistinguishable. With uniform on instead, this is the DDH assumption of the Crypto Guide (§“Diffie–Hellman: computational and decisional”, Definition “Decisional Diffie–Hellman, DDH”). The volume assumes the form with uniform on because is so distributed, and claims no reduction between the two forms; the protocol specification expects the non-uniformity of to cause no security issue (§“Orchard Key Components”, note). It is used by Propositions 3.17 and 10.6 (“Confidentiality and key privacy of note encryption”).
Proposition 3.17 (Unlinkability of diversified addresses).
Let two keys be generated independently with . An adversary holds , and of both keys, and none of , and of either. It chooses indices , and with , and receives the address of key at index , the address of key at index , and the address of key at index , for a uniform hidden bit ; it outputs a bit . Conditioned on the event that the three diversifiers are pairwise distinct, its advantage is negligible under Assumptions 2.12 (through Lemma 2.15), 3.13, 3.15, 2.8 and 3.16, together with Assumption 2.22 for Lemma “Rejection in key generation”. This is the unlinkability requirement of the protocol specification, §“ and Hash Functions”, which stipulates distinct diversifiers.
Proof.
For each the game is modified by a sequence of hops, each changing the adversary’s output distribution by a negligible amount (Crypto Guide, §“The hybrid argument”, Lemma “Hybrid lemma”). Each hop is justified by a reduction that runs the game; the event is efficiently decidable from the diversifiers and has probability at least in every game below, so conditioning on at most doubles each cost.
-
1.
Each key is replaced by a single draw without rejection (Lemma “Rejection in key generation”, §3.2).
-
2.
For each key in turn, is replaced by independent uniform elements of the three fields (Lemma 2.15); the reduction derives the remaining components and the addresses.
-
3.
For each key in turn, is replaced by (Assumption 3.13); the reduction is given , generates the other key itself, and computes the game from the triple. Now and are uniform and independent of all else, and, except on the negligible events , the scalar is uniform on and independent of (Lemmas “Distribution of ” and “Rejection in key generation”, §3.2).
-
4.
For in turn, is replaced by a uniformly random permutation of (Assumption 3.15); the reduction queries its oracle at the indices it needs. Then because , and on the triple is uniform on pairwise distinct triples, for either value of . The event fails only if equals or , of probability .
-
5.
On the inputs of are distinct, since is injective, so under Assumption 2.8 the bases , , are independent uniform points, each , which invokes the fallback, with probability only.
In the last game the adversary’s view consists of , , of both keys and , independent of the rest and identically distributed for , together with
where , are independent and uniform on . The first two pairs are public keys of the per-key-base ElGamal scheme with private keys and . For the uniform point equals for a uniform scalar , so the third pair is , an encryption of under key (Crypto Guide, §“Key privacy”, Construction “ElGamal encryption”). Distinguishing is therefore the game of Definition “Key privacy under chosen-plaintext attack, IK-CPA” of the same subsection, for the message . The proof of its Theorem “ElGamal is key-private under DDH” bounds the advantage by two DDH advantages. That proof plants the first exponent of the DDH triple as a private key; with private keys uniform on , the same proof, with the other key’s private key drawn uniformly from (the -coordinate of a uniform non-identity point), reduces to Assumption 3.16. Its reduction samples itself and programs at their three inputs with the planted bases before running the adversary. The Crypto Guide’s Remark “What key privacy buys upstairs” records this correspondence for diversified addresses. Summing the costs of the hops, the advantage is negligible. □
3.4 Key capabilities and scope
Figure 1 gives the derivation graph, each edge labelled by its operation, and each one-way edge also by the assumption that makes it one-way. Proposition 3.18 proves four separations: the full viewing key yields no , the incoming viewing key neither nor , the outgoing viewing key no , and an address no .
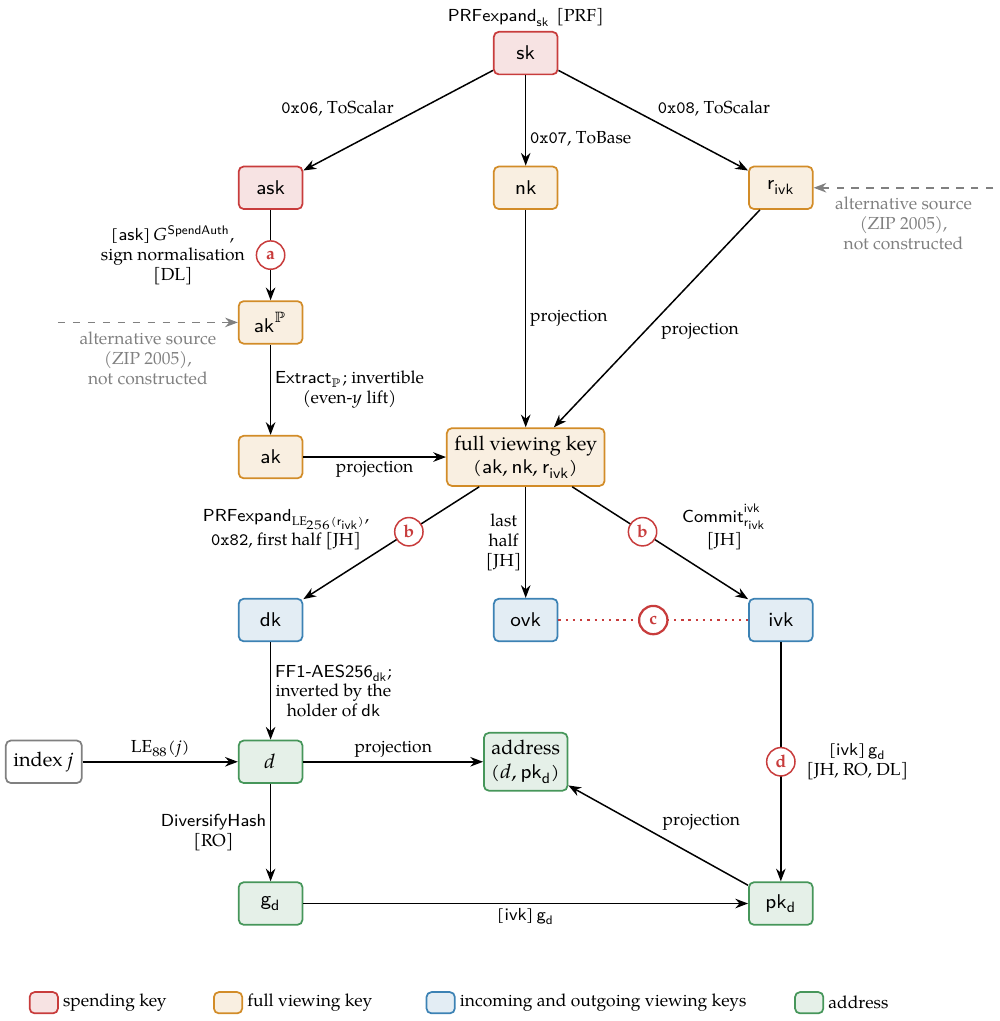
Proposition 3.18 (Capability separation).
Let a key be generated honestly with . No efficient algorithm, given the public parameters and only the listed key material of the key, outputs the listed secret, except with negligible probability:
-
(a)
given the full viewing key , the scalar ;
-
(b)
given the incoming viewing key , the key or the scalar ;
-
(c)
given , the scalar ;
-
(d)
given an address of the key, the scalar .
The hypotheses are: for (a), Assumptions 2.12 (through Lemma 2.15) and 2.22; for (b), those of (a) and, for , Assumption 3.13; for (c), Assumptions 2.12 and 3.13; for (d), Assumptions 2.12, 3.13, 2.8 and 2.22 (“Discrete logarithms on Pallas”). Every part also uses Lemma “Rejection in key generation” (§3.2), under Assumptions 2.12, 2.22 and 2.8. These are the only separations claimed.
Proof.
By Lemma “Rejection in key generation” (§3.2), a single draw from a uniform replaces the key at a negligible cost. By Lemma 2.15, its triple is then replaced by independent uniform elements of , and , at a further negligible cost: in each part the success of an algorithm is efficiently decidable from the three values, by deriving the remaining components, running the algorithm and comparing its output with the secret. The result is called the idealised key.
(a) Let an algorithm output from with probability for the idealised key. An algorithm receives for uniform on , draws and uniformly, and runs on . The input is distributed as for the idealised key, because the sign normalisation replaces by and does not change (Lemma 2.4). A correct output satisfies , the even- lift of , which is or ; outputs whichever of and maps to . Hence computes discrete logarithms to the generator with probability , and is negligible by Assumption 2.22.
(b) An algorithm that computes from computes it from by first deriving , so (a) applies. Let output from with probability . A distinguisher for Assumption 3.13, given of the idealised key and a triple , runs on and outputs exactly when outputs . On the real triple it outputs with probability . On the ideal triple receives and , which is independent of unless , a negligible event (Lemma “Rejection in key generation”); since is uniform on , then succeeds with probability at most plus a negligible term. So exceeds the distinguisher’s advantage by a negligible amount at most.
(c) Let output from with probability . The distinguisher given and runs on and outputs exactly when outputs . On the ideal triple, is independent of , which, for , takes each value with probability at most by Lemma “Distribution of ”. Hence is at most the advantage under Assumption 3.13 plus and a negligible term.
(d) Let output from the address at an index , possibly of its choice, with probability . The distinguisher given and computes , and , runs on , and outputs exactly when outputs . On the ideal triple, succeeds with probability , for the advantage under Assumption 3.13; there, outside the negligible event , the value is with probability and otherwise uniform on , independently of and of , hence of . An algorithm receives a generator and for uniform on . It draws uniform on and uniform, computes from and , programs at with the uniform non-identity point (Assumption 2.8), answers other queries with fresh uniform points, and runs on . With probability the exponent lies in ; it is then uniform on , and the view of is that of the ideal triple conditioned on , up to statistical distance for the programmed point. Algorithm outputs the output of and so computes with probability at least
a loss factor of , about , against Assumption 2.22. Hence , and with it , is negligible. □
Of the objects of this section only an address , with the base computed from , is public; , , , , , , the full viewing key, , , and the index are secret key material. One incoming viewing key yields addresses (§3.3), unlinkable in the sense of Proposition 3.17 (“Unlinkability of diversified addresses”).
What a holder of each key can compute from the objects of later sections is stated where those objects are constructed, each with a back-reference to Proposition 3.18: from nullifiers in “Nullifier uniqueness and unlinkability” (§6.4), and from note ciphertexts in “The outgoing ciphertext” (§10.3) and “Trial decryption and note acceptance” (§10.4). This section states no such power.