3 Addresses and viewing keys (ZIP 316)
This section passes from the keys of an account to the addresses and viewing keys that a wallet hands out. It defines the diversifier index and the recovery of an index from an address, the raw encodings of receivers and keys, the unified container with its jumbled string encoding and its viewing-key form, the unified address at an index of a viewing key, the extensions of Revision of ZIP 316, and the recipient addresses a sender handles.
3.1 Diversifier indices
The address layer meets two requirements.
-
(R1)
Each payee receives an address unlinkable to every other address of the same holder, while all of them are spendable by one key and recoverable from one seed (protocol specification, §“ and Hash Functions”, security requirements; ZIP 32; ZIP 316, “Rationale for address derivation”). Each shielded protocol meets (R1) with diversified addresses.
-
(R2)
Transparent, Sapling and Orchard receivers coexist, each with its own format. A recipient publishes one string, from which the sender selects the most preferred receiver type it supports, and whose characters a sender can check (ZIP 316, “Motivation” and “Requirements”). ZIP 316 meets (R2) above the protocols, with unified containers (§3.3) and their jumbled string encoding (§3.4).
The Ironwood Guide constructs the Orchard key tiers, the diversifier map and the diversified base (§“Viewing keys” and §“Diversified addresses”). This subsection adds the diversifier index, shared by Sapling and Orchard and used by transparent derivation.
The Orchard address at index of an incoming viewing key is that of the Ironwood Guide, §“Diversified addresses”, Construction “Diversified address”, cited and not re-derived: , , which is unless that is the identity and the fallback point otherwise, and ; the address is . For each scope of an account (Construction 2.14) the pair is the first and the second bytes of (Ironwood Guide, §“Viewing keys”), and is the incoming viewing key of the scope. The address at index is the default address of the scope (protocol specification, §“Orchard Key Components”; ZIP 32, “Orchard diversifier and OVK derivation”).
Definition 3.1 (Diversifier index).
For a -byte diversifier key and an index , the diversifier at index is
the FF1 mode of NIST SP 800-38G over AES-256 with key , radix , length and the empty tweak (Crypto Guide, §“Format-preserving encryption and FF1”, Construction “The FF1 mode of NIST SP 800-38G”; protocol specification, §“Pseudo Random Permutations”). The map is the same in both shielded protocols; only the key differs.
-
1.
For Orchard, of the scope , as above.
-
2.
For Sapling, is the diversifier-key component of the account’s Sapling extended spending key: at the master key and for a hardened child, with the left half of the child’s derivation output (ZIP 32, “Sapling master key generation” and “Sapling child key derivation”); Sapling key derivation is cited and not constructed.
The diversifier , and the index , are valid for a protocol if and only if that protocol’s does not return at .
-
3.
Orchard: is total, so every index is valid, a scope has exactly addresses, and the default diversifier is (ZIP 32, “Orchard diversifier and OVK derivation”).
-
4.
Sapling: , a hash into the points of order of the Jubjub curve that returns on some inputs (protocol specification, §“ and Hash Functions”, §“Jubjub” and §“Group Hash into Jubjub”, cited and not constructed). Approximately half of all indices are valid (ZIP 32, “Sapling diversifier derivation”); the probability under the specification’s random-oracle model is derived in §3.6. The default Sapling diversifier is for the least valid (same section).
Totality of removes the search for a valid index. The Sapling failure rate matters when one index must serve several protocols at once (§3.6).
Index-choice rules, specified (protocol specification, §“Orchard Key Components” and §“Sapling Key Components”, notes). Orchard diversifier indices SHOULD NOT be chosen at random; ZIP 32 specifies their use in hierarchical deterministic wallets. Address generators MAY encode information in the diversifier index, recoverable by a holder of (Lemma 3.3). For Sapling, generators MAY encode information in the diversifier itself, and it is RECOMMENDED to encode it in the ZIP 32 diversifier index instead, so that only a holder of reads it.
Proposition 3.2 (Distinct diversifiers).
-
(a)
For every diversifier key the map is a bijection from onto . In particular distinct indices give distinct diversifiers, and a wallet issues the indices over the whole index space without a repeated diversifier.
-
(b)
If instead diversifiers are drawn independently and uniformly from , the probability that two coincide satisfies
so a collision becomes likely once is of order ; at the bounds are and .
Proof.
(a) The map is a bijection from onto , and under a fixed key and tweak is a bijection of (Crypto Guide, §“Format-preserving encryption and FF1”, Proposition “FF1 is a keyed bijection on ”); the composition is a bijection. (b) The Math Guide, §“The union bound and a birthday calculation”, Proposition “Birthday bound”, with . □
The specification notes that an -bit diversifier is not unguessable at the -bit security level and that randomly chosen diversifiers collide near choices; the keyed permutation removes the collisions, provided indices do not repeat (protocol specification, §“ and Hash Functions”, notes). One further reason for a keyed permutation is ZIP 32’s: it makes the diversifier sequence of each account pseudorandom and uncorrelated with that of any other account, so issued diversifiers do not reveal how many addresses have been generated (ZIP 32, “Sapling diversifier derivation” and “Orchard diversifier and OVK derivation”). The Ironwood Guide supplies Assumption “FF1-AES256 as a pseudorandom permutation” (§“Diversified addresses”) and the unlinkability proposition only.
In Orchard, is derived from the full viewing key of scope , so a holder of the account’s Orchard full viewing key computes for both scopes, hence the index of any diversifier of the account (Lemma 3.3; ZIP 32, “Orchard diversifier and OVK derivation”). In Sapling the same capability belongs to the extended full viewing key, of which is a component. A holder of the incoming viewing key of one scope has this capability for that scope only.
Lemma 3.3 (Index recovery and ownership).
Let be an Orchard address and the incoming viewing key of some scope.
-
(i)
The value is defined for every and every , and . Decryption alone therefore proves nothing about ownership.
-
(ii)
The address is the address of at some index if and only if ; the index is then unique and equals .
- (iii)
The Sapling case of (i) and (ii) is the same with , the test of (ii) failing when it returns . For (iii), both tests succeed only if the two Sapling incoming viewing keys are equal; this volume does not bound that probability for Sapling.
Proof.
(i) FF1 decryption is the two-sided inverse of encryption under every key and tweak (Crypto Guide, §“Format-preserving encryption and FF1”, Proposition “FF1 is a keyed bijection on ”), and is a bijection. (ii) If is the address at index , then , so by (i) and Proposition 3.2 (a), and by the Ironwood Guide’s Construction “Diversified address” (§“Diversified addresses”). Conversely, if , the address at index is . (iii) If both tests succeed, then with in a group of prime order , and both scalars lie in with , so . Its probability is bounded as in the proof of Proposition 2.17: after the replacement of Assumption 2.16, at most by the Ironwood Guide’s Lemma “Distribution of ” (§“Viewing keys”), plus the distinguishing advantage, equality being efficiently decidable. □
Unlinkability of the addresses of one key is cited with its assumptions. For Orchard it is the Ironwood Guide, §“Diversified addresses”, Proposition “Unlinkability of diversified addresses”: for two keys generated independently with , an adversary that holds , and of both keys and chooses indices , and distinguishes which key produced the third address with negligible advantage, conditioned on the three diversifiers being pairwise distinct. Its assumptions are the Ironwood Guide’s “Pseudorandomness of PRF expansion”, “Joint hiding of the viewing keys”, “FF1-AES256 as a pseudorandom permutation”, “GroupHash as a random oracle”, “DDH on Pallas” and “Discrete logarithms on Pallas”. Account keys are admitted as such keys by Lemma 2.9, the win event being decidable by the challenger; the addresses of one key at distinct indices have distinct diversifiers by Proposition 3.2 (a). For Sapling the protocol specification argues the same property under DDH on the prime-order subgroup of Jubjub, with modelled as a random oracle, through IK-CPA key privacy of ElGamal (§“ and Hash Functions”, notes; Crypto Guide, §“Key privacy”). This volume does not prove the Sapling case.
Remark 3.4 (Chosen-diversifier oracle).
Suppose that the holder of an incoming viewing key gives an adversary the address of that key at any diversifier the adversary chooses. The adversary then breaks unlinkability outright: given an address , it requests the address at and compares the returned transmission key with . The two are equal if and only if the key is the same, the base being a point other than the identity in a group of prime order. No other privacy property is affected. Implementations SHOULD avoid providing such a chosen-diversifier oracle (protocol specification, §“ and Hash Functions”, notes). An interface returning the address at a requested index gives no chosen diversifier (Lemma 3.5), but it returns the issued addresses themselves: it links every address whose index the requester queries, and under sequential issuance (Proposition 3.2) small indices reach every issued address.
Lemma 3.5 (Index queries give no chosen diversifier).
Let be either diversifier key of an Orchard key with . Under Assumption 2.16, the hypotheses of Lemma 2.9, and the Ironwood Guide’s Assumption “FF1-AES256 as a pseudorandom permutation” (§“Diversified addresses”), an adversary without that obtains the diversifiers at indices of its choice obtains a given , fixed independently of , with probability at most plus its distinguishing advantages against the two assumptions and, for an account key, the loss of Lemma 2.9. This volume does not prove the Sapling case.
Proof.
Replace by a uniform -byte string independent of the other keys; by Assumption 2.16, applied after Lemma 2.9, the probability changes by at most that distinguishing advantage and the loss of that Lemma, the win event being decidable. Then replace FF1-AES256 keyed by with a uniform permutation of ; the probability changes by at most the distinguishing advantage. Repeated indices add nothing, so let the adversary query distinct indices. Each image is uniform on the values not yet returned, so the -th image is the first to equal with probability
summing over , is returned with probability . □
3.2 Raw encodings
The items of unified containers carry the byte encodings below. Each is stated with the validity condition that a decoder applies.
Definition 3.6 (Raw receiver and key encodings).
-
(a)
An Orchard raw payment address has bytes, , where is the -byte compressed encoding of the Pallas point (Ironwood Guide, §“Fields, groups, and encodings”). A decoder MUST treat the address as invalid if returns or the identity (protocol specification, §“Orchard Raw Payment Addresses”).
-
(b)
A Sapling raw payment address has bytes, , with the compressed Jubjub encoding. It MUST be considered invalid if returns , if the encoding of is non-canonical, or if is not a point of order , the identity included (protocol specification, §“Sapling Payment Addresses”).
-
(c)
An Orchard raw full viewing key has bytes,
It MUST be considered invalid if , or is not the canonical encoding of an element of its field (, , ), if is not the -coordinate of a point of other than the identity, or if the external or the internal incoming viewing key derived from it is or (protocol specification, §“Orchard Raw Full Viewing Keys”).
-
(d)
An Orchard raw incoming viewing key has bytes, . It MUST be considered invalid unless (protocol specification, §“Orchard Raw Incoming Viewing Keys”).
-
(e)
String forms. No Bech32 or Bech32m encoding exists for an individual Orchard payment address, incoming viewing key or full viewing key; the unified encodings of §3.4 are their only strings. A Sapling payment address keeps a standalone Bech32 string, with human-readable part zs on Mainnet and ztestsapling on Testnet (same sections).
-
(f)
Transparent receivers. A P2PKH (pay-to-public-key-hash) address pays to the -byte of a -byte compressed ECDSA validating key; a P2SH (pay-to-script-hash) address pays to the -byte of a redeem script that the spender reveals and satisfies (Crypto Guide, §“The transparent layer’s hashes”). Their raw encoding prefixes two version bytes to the hash and is written in Base58Check (protocol specification, §“Transparent Addresses”). Inside a unified container a transparent receiver is the bare -byte hash, without the two version bytes (ZIP 316, “Requirements for both Unified Addresses and Unified Viewing Keys”).
One Orchard raw address serves both pools of the Orchard protocol (§3.3).
3.3 Unified addresses
ZIP 316 defines Revision , the format of this subsection and of §3.4, and Revision , which adds metadata items, splits the address prefix into a shielded-only and a transparent-enabled form, and renames the viewing-key prefixes (§3.7); Revision is withdrawn (ZIP 316, “Revisions”). The revision of a container is read from its human-readable part. The status of ZIP 316 is that of Table 1; everything Revision adds is specified in the sense of Definition 1.1.
Definition 3.7 (Unified container).
For , is the variable-length integer of Bitcoin that ZIP 316 cites:
the range of fixing the form. An item is a pair of a typecode and a byte string . The raw encoding of a container with items , where , is
Both and MUST be at most ; since , each takes at most bytes and an item header at most .
Typecodes and are transparent, and shielded, and to designate metadata items, items that are neither receivers nor viewing keys (§3.7). A unified address (UA) is a container whose non-metadata items are receivers, in the raw encodings of Definition 3.6 under the typecodes of Table 3. A unified full viewing key (UFVK) and a unified incoming viewing key (UIVK) are containers whose non-metadata items are full, respectively incoming, viewing keys (§3.5); UVK denotes either. No typecode exists for Sprout.
Validity. Every container holds at least one non-metadata item. A Revision UA, and a Revision UVK, holds at least one shielded item. A Revision shielded-only UA holds no transparent item; a Revision transparent-enabled UA may consist of a single P2PKH receiver, and a Revision UVK need hold no shielded item. A Consumer MUST reject a container
-
(i)
that violates the containment rule of its revision;
-
(ii)
in which a typecode repeats, or which holds both and ;
-
(iii)
which holds only metadata items;
-
(iv)
whose items are not in ascending typecode order;
-
(v)
which has bytes after the last item;
- (vi)
A Consumer MUST ignore items with typecodes it does not recognise, with the exception stated in §3.7; a Consumer therefore parses a container that holds unrecognised items.
Same-account rule. Within one UA or UVK, all receivers, full viewing keys and incoming viewing keys derived hierarchically SHOULD belong to the same account at the ZIP 32 or BIP 44 account level, or, for ZIP 48 and FROST UVKs, to one set of signers able to generate independent addresses for that spending authority. FROST key material MUST be derived according to ZIP 312 and ZIP 2005, in particular ZIP 2005, “Usage with FROST”.
Sources: ZIP 316, “Encoding of Unified Addresses”, “Requirements for both Unified Addresses and Unified Viewing Keys” and “Receivers”.
The ascending order makes the raw encoding a function of the set of items, so a representation that discards the order reproduces the same encoding, provided it retains unrecognised items (ZIP 316, “Rationale for Item ordering”). This order is not the priority order below.
| Typecode | Item | Receiver | UFVK item | UIVK item |
|---|---|---|---|---|
| transparent P2PKH | ||||
| transparent P2SH | — | — | ||
| Sapling | ||||
| Orchard |
Receiver selection. The Sender of a payment to a UA MUST use the receiver of the most preferred type that it supports, by the Priority List Orchard (), Sapling (), then P2SH () or P2PKH (); an unrecognised item is treated as absent, with the exception of §3.7. A wallet MAY let its users configure which receiver types it can send to, and MUST NOT let them change the order of the Priority List except by opting into an experiment, whose specification MAY add to the list and SHOULD keep the preference for more recent shielded protocols (ZIP 316, “Encoding of Unified Addresses”, “Transfers” and “Experimental Usage”). The Orchard receiver belongs to the Orchard protocol, not to a pool: one trial-decrypts both Orchard-pool and Ironwood-pool note ciphertexts (ZIP 326, “Scanning for Ironwood-pool and Orchard-pool notes”), and the Ironwood pool changes no address structure or encoding (ZIP 229, “Abstract”). The pool in which a payment to an Orchard receiver is made is fixed by the routing rule of §11.2, which carries the prohibition of ZIP 326, “Wallet key-generation restrictions”, on paying external receivers in the Orchard pool; the Priority List is unchanged.
3.4 String encoding: F4Jumble and Bech32m
The Bech32m checksum does not cascade: a user who checks only the beginning and the end of a long string can miss an adversarial substitution of an inner receiver. ZIP 316 therefore passes the whole payload through F4Jumble, an unkeyed four-round Feistel construction that approximates a random permutation of the entire byte string, so that every output character depends on every input byte. It states two goals (ZIP 316, “Jumbling”).
-
(i)
Near second-preimage resistance. Given honestly generated UAs or UVKs, an adversary does not produce a valid one that it controls, knowing at least one constituent private key, whose string matches one of the targets on a chosen set of characters, for concreteness the first and the last .
-
(ii)
Nonmalleability. Without any private key, an adversary does not produce a valid UA or UVK usefully different from a target, for example with its shielded receiver removed, that matches the target on the checked characters.
Generic attacks bound what is achievable: about for (i) and for (ii), where is the work to produce and verify one UA or UVK, the size of the character set and the probability that a random decoding is valid and useful (ZIP 316, “Discussion”). Jumbling is not authentication. F4Jumble is unkeyed, so anyone can jumble and checksum a wholly substituted address, and an address is still obtained or verified through a trusted channel; jumbling raises only the cost of partial-match and malleation attacks against a genuine string.
Construction 3.8 (F4Jumble).
Let and . For and byte strings , with the first argument of BLAKE2b the personalisation,
an -byte hash and an extendable-output function in the sense of the Crypto Guide, §“Hash functions and the random oracle model”, Definition “Extendable-output function”, for the lengths and below. For a byte string of length with , let
split with , and let
Each personalisation has bytes: for and for . They are pairwise distinct, differing at byte between the and the family and at bytes to within a family, and distinct from the three personalisations of key derivation in Table 2 and from that of , Zcash_ExpandSeed. Being of one length and distinct, they are prefix-free tags, so BLAKE2b under these personalisations is modelled as independent random oracles (Crypto Guide, §“Domain separation and personalisation”, Proposition “Domain separation yields independent oracles”).
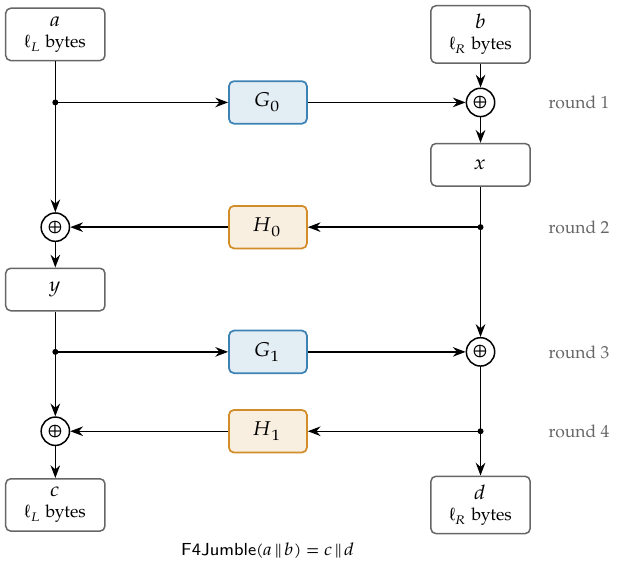
Proposition 3.9 (F4Jumble is a permutation).
For every with , is well defined and is a bijection of the -byte strings. Its inverse maps , with , to computed by
Proof.
Well defined. From , ; from , the output length of is admissible for BLAKE2b. If then and one block of suffices. Otherwise and , so and every counter fits ; this is the reason for .
Bijection. Each of the four steps replaces one half by its XOR with a function of the other half, which it leaves unchanged, and implies . Each step is therefore inverted by recomputing the same function of the unchanged half, and the composition of the four inverses in reverse order is the stated map, a two-sided inverse. This is the argument of the Crypto Guide, §“Format-preserving encryption and FF1”, Proposition “Feistel is a bijection regardless of the round functions”. Unequal halves change nothing, since maps into bytes and into bytes, the lengths of the halves they are XORed into. □
ZIP 316, “Heuristic analysis”, motivates the number of rounds.
Construction 3.10 (Unified string encoding).
Human-readable parts of Revision : u for a UA, uview for a UFVK and uivk for a UIVK on Mainnet; on Testnet test is appended (utest, uviewtest, uivktest). Let be the raw encoding of Definition 3.7, the human-readable part and the human-readable part in US-ASCII right-padded with zero bytes to bytes.
-
1.
Producer. It MUST ensure , and outputs , the Bech32m encoding of BIP 350 with its length restriction ignored.
-
2.
Consumer. It MUST decode as follows, rejecting the string at the first failure:
-
(1)
decode with Bech32m, rejecting an incorrect checksum;
-
(2)
reject a decoded byte string shorter than or longer than bytes;
-
(3)
apply (Proposition 3.9);
-
(4)
reject a result that does not end in the -byte padding of the string’s human-readable part, and remove that padding;
-
(5)
parse the rest as a raw encoding, rejecting the whole string if any rule of Definition 3.7 fails.
-
(1)
UFVKs and UIVKs use the same procedure under their own human-readable parts (ZIP 316, “Encoding of Unified Addresses”, “Encoding of Unified Full/Incoming Viewing Keys” and “Usage for Unified Addresses, UFVKs, and UIVKs”; BIP 350).
The padding supplies the redundancy that defeats the generic nonmalleability attack, since a random decoding must end in the exact bytes, and gives the human-readable part the same protection against malleation as the payload, which may help against cross-network substitution and against confusion of an address with a viewing key (ZIP 316, “Usage for Unified Addresses, UFVKs, and UIVKs” and “Heuristic analysis”).
Length rules (ZIP 316, “Rationale for length restrictions” and “Efficiency”). The -byte minimum is Revision ’s: one P2PKH item of bytes and the padding. Revision specified bytes. No set of items valid in Revision has an encoding of to bytes (the smallest Revision input is bytes), so the difference is unobservable except in the error reported, and a Consumer supporting Revision MAY apply either minimum to Revision strings. A Consumer that cannot support strings up to MUST support those with of at least bytes; a full implementation supports .
Display rule, specified (ZIP 316, “Requirements for both Unified Addresses and Unified Viewing Keys”). If the string of a UA or UVK is shown in an abridged form, at least its first characters MUST be shown. The rationale is the ZIP’s (“Rationale for showing at least the first 20 characters”). After the longest Mainnet human-readable part of Revision , uview, and the separator 1, characters remain, bits of jumbled data at bits per character, below the target of against classical attacks, and multi-target attacks are possible; is an absolute minimum and a wallet may show more. Only a prefix counts, because displays that show different substrings let a user compare only the characters common to all of them, and because checksum characters complicate the analysis of partial matching.
Item sizes. A Sapling or Orchard receiver item has bytes (typecode, length, -byte diversifier and -byte transmission key), a P2PKH receiver item bytes, and the padding bytes. Hence a UA with Sapling and Orchard receivers has , and one with P2PKH, Sapling and Orchard receivers (ZIP 316, “Efficiency”).
Example 3.11 (A unified address, end to end).
Let the seed be the bytes , on Mainnet, with the Orchard account at (Definition 2.7), the external scope and the index . Every value below is computed by script from the seed.
Receiver. The diversifier key is the first half of the expansion of the account’s full viewing key, and FF1 encryption of gives (Definition 3.1):
| 82cc9d79742fe5ae9a142b9336a98677b154fe20401eb18998dbed915b0453ce | |
|---|---|
| 0100000000000000000000 | |
| 3fadf8edb20a3301e8260a | |
| a311f4cbd54d7d6a76baac88c244b0b121c6dc22a8bcce15898e267829fc1e01 |
Decryption returns , so , and the ownership test of Lemma 3.3 holds for the external . It fails for the internal , although also decrypts , to the index : recovery alone proves nothing, and the test on decides. The neighbouring diversifiers are and ; that consecutive indices give unrelated strings illustrates the Ironwood Guide’s Assumption “FF1-AES256 as a pseudorandom permutation” (§“Diversified addresses”) and is not evidence for it.
Container. The UA has one item, so its raw encoding (Definition 3.7) is the header followed by the -byte receiver , bytes in all. The padding is (u) followed by fifteen zero bytes, so has , and . The cells of Construction 3.8:
| 032b3fadf8edb20a3301e8260aa311f4cbd54d7d6a76baac88c244b0b121 | |
| c6dc22a8bcce15898e267829fc1e0175000000000000000000000000000000 | |
| e6f1529b03a0ad0a4209da8e4365ca14a5988bf1d03084a1c326f929c574ca | |
| 37b358eb784bb2b315fd35c595628cfa9aa8045ef271728dd0cbf84dc81a | |
| ad26d7fb043e09cbf18e8f4d80d2b423ecb01719170463d644be4c76daab6b | |
| 98979f9a7d2dfce7b1616a8d2b9975f87878171b6fcf33b303f770b4aa64 |
The header, the diversifier and the padding are legible in and , and in neither nor .
String. The bytes of regroup into five-bit symbols, the last padded with two zero bits. With the human-readable part u, the separator 1 and the -symbol checksum, the string has characters:
u1nztelxna9h7w0vtpd2xjhxt4lpu8s9cmdl8n8vcr7actf2ny45nd07cy8cyuhuvw3axcp545y0ktq9cezuzx84jyhex8dk4tdvwhu4dl
Decoding reverses each stage of Construction 3.10, and . The string equals the unified-address test vector for account and index of the zcash-test-vectors suite, which ZIP 32, “Test Vectors”, names.
3.5 Unified viewing keys
Definition 3.12 (Unified full and incoming viewing keys).
A UFVK and a UIVK are containers of Definition 3.7 under the string encoding of Construction 3.10 with their own human-readable parts; a Consumer MUST use the decoding procedure of Construction 3.10. Their items, at the receiver typecodes, are the following.
-
1.
Orchard, : the -byte raw full viewing key, respectively the -byte raw incoming viewing key, of Definition 3.6.
-
2.
Sapling, : in a UFVK the bytes
of ZIP 32, “Sapling helper functions”, which SHOULD be derived from the account-level extended full viewing key; in a UIVK the bytes , valid only if (protocol specification, §“Sapling Incoming Viewing Keys”; ZIP 316 notes the exclusion of ). The Sapling UIVK item carries beyond the specification’s Sapling incoming viewing key, which is alone (protocol specification, §“Sapling Incoming Viewing Keys”); maps an index to a diversifier and back, so a UIVK yields addresses at indices (Construction 3.16) and recovers the index of a diversifier (Lemma 3.3).
-
3.
Transparent P2PKH, : the bytes of a -byte BIP 32 chain code and a -byte compressed public key, the last bytes of the BIP 32 extended public key serialisation (BIP 32, “Serialization format”). The UFVK item is the key at , the account level of BIP 44, and the UIVK item its external (non-change) child at .
The current viewing-key types reuse the receiver typecodes; future types MAY use others. The Priority List does not govern viewing keys: a Consumer normally takes the union of the information of all items (ZIP 316, “Encoding of Unified Full/Incoming Viewing Keys”).
The transparent item omits the BIP 32 depth, parent fingerprint and child number; the format is ZIP 316’s. That the child number of the account-level key would reveal the account index is this volume’s inference, not a statement of the ZIP. The Sapling UFVK item carries no chain code, so a UFVK supports no non-hardened Sapling child derivation below the account.
Construction 3.13 (Attenuation of a UFVK to a UIVK).
Item by item, with the typecode preserved:
-
1.
a Sapling full viewing key to its incoming viewing key (protocol specification, §“Sapling Key Components”), with carried over;
-
2.
an Orchard full viewing key to the external-scope incoming viewing key (Ironwood Guide, §“Viewing keys”);
-
3.
a transparent P2PKH account key to its child at non-hardened index by BIP 32 public-to-public derivation (BIP 32, “Public parent key public child key”).
Items with unrecognised typecodes, and items of experiments the user has not opted into, MUST be dropped (ZIP 316, “Deriving a UIVK from a UFVK”). The treatment of metadata items is stated with them, in §3.7.
Assumption 3.14 (Independence of the per-protocol key trees).
For a wallet seed (Definition 2.1) and an account index , the Orchard account key of Definition 2.7, the Sapling extended spending key at of ZIP 32 and the BIP 32 extended private key at are jointly computationally indistinguishable from three independently generated keys of the respective protocols: a uniform Orchard spending key with a uniform chain code, a uniform Sapling master-derived key and a uniform BIP 32 key.
The assumption has a heuristic basis and no proof. It follows if BLAKE2b-512 under ZcashIP32Sapling (the Sapling master key) and HMAC-SHA512 under the key Bitcoin seed (the BIP 32 master key) are modelled as random oracles independent of BLAKE2b-512 under ZcashIP32Orchard, and the Sapling and BIP 32 hardened child derivations as PRFs keyed by the parent chain code (HMAC as a PRF: Crypto Guide, §“PRFs from hash functions: length extension and keyed BLAKE2”; ZIP 32, “Sapling master key generation” and “Sapling child key derivation”; BIP 32, “Master key generation” and “Private parent key private child key”). Lemma 2.5 proves the Orchard component and nothing more.
Proposition 3.15 (Capabilities of a unified viewing key).
Let the keys of one account be generated from a seed, with for the Orchard component, and let Assumption 3.14 hold.
-
(a)
From a UFVK the following are computed: for Orchard, the incoming and outgoing viewing keys of both scopes and , hence receipt, spend and outgoing detection (Proposition 2.15); for Sapling, the same through ZIP 32’s internal key derivation; for transparent keys, every external and internal address and the transparent outgoing viewing keys (Construction 2.18). No secret that is infeasible to compute from its own component becomes feasible from the whole UFVK: in particular the Orchard (Ironwood Guide, §“Key capabilities and scope”, Proposition “Capability separation”, part (a)), the Sapling spend authorising key and a transparent private key.
-
(b)
A UIVK gives receipt detection for the external scope in each shielded protocol it carries, and no spend detection for its shielded items: is infeasible to compute from an Orchard (Ironwood Guide, §“Key capabilities and scope”, Proposition “Capability separation”, part (b)), and internal-scope receipt is neither detected (Proposition 2.17) nor derivable (Proposition 2.20). A transparent UIVK item yields the external addresses and not the internal ones. Spends of transparent funds are public on the transparent chain, so their visibility is a property of the chain, not of the key.
Metadata items confer no viewing authority (§3.7), so the statements hold for containers of either revision.
Proof.
Componentwise. The computations of (a) and (b) are those of the cited constructions applied to each item. For the separations: by Assumption 3.14 the components are indistinguishable from independently generated keys, so a reduction given one component generates the others itself. An algorithm that outputs a secret of one protocol from the whole container thus yields an algorithm that outputs it from that protocol’s component alone, with the advantage of Assumption 3.14 added; the success of either is efficiently decidable, by recomputing the public key or viewing key from the output. The per-component statements are Propositions 2.15, 2.17 and 2.20 with the Ironwood Guide, §“Key capabilities and scope”, Proposition “Capability separation”, under the assumptions named there, for Orchard; ZIP 32 and the protocol specification, §“Sapling Key Components”, cited, for Sapling; and Assumption 2.19 with BIP 32, “Security”, for the transparent keys. The transparent spend clause is a property of transparent inputs, which name the outpoints they spend in the clear. □
3.6 Deriving unified addresses
Construction 3.16 (Unified address at an index).
Let be a UIVK. Choose one index , which MUST be valid for every item of :
-
1.
for an Orchard item, always;
-
2.
for a Sapling item, if and only if , with the diversifier of the item’s at (Definition 3.1);
-
3.
for a transparent P2PKH item, if and only if and BIP 32 derivation of the child at index succeeds; it fails with probability below (BIP 32, “Public parent key public child key”).
Each receiver is derived from its item at the same : a Sapling or Orchard receiver as the address at index of (protocol specification, §“Sapling Key Components” and §“Orchard Key Components”; Ironwood Guide, §“Diversified addresses”, Construction “Diversified address”), and a transparent P2PKH receiver as the of the non-hardened BIP 32 public child of the external key, so that its path is (BIP 44). Items with unrecognised typecodes, and items of experiments the user has not opted into, MUST be dropped; metadata items are treated in §3.7 (ZIP 316, “Deriving a Unified Address from a UIVK”).
Proposition 3.17 (Indices valid for a unified key).
Let be the set of indices valid for every item of a UIVK .
-
(a)
If has only an Orchard item, .
-
(b)
If has a transparent item, , a fraction of the index space, so has at most unified addresses.
-
(c)
Let have a Sapling item, and let in be modelled as a random oracle, the model of the protocol specification, §“Group Hash into Jubjub”, notes. The events that the indices are valid for the Sapling item are independent over distinct indices, each of probability
with the cofactor and the prime subgroup order of Jubjub (protocol specification, §“Jubjub”); an index is invalid with probability . ZIP 32’s “approximately half” and ZIP 316’s probability are this value rounded.
-
(d)
With a Sapling and a transparent item, is the set of indices below that are Sapling-valid and at which BIP 32 derivation succeeds; its expected size lies within of .
For the Sapling key of account of the seed of Example 3.11, of the indices are valid, a fraction , and index is valid.
Proof.
The set is the intersection of the per-item valid sets of Construction 3.16, which gives (a) and (b), distinct indices giving distinct receivers.
(c) Distinct indices give distinct diversifiers (Proposition 3.2 (a)), hence distinct inputs to , whose outputs are then independent and uniform on . The group hash returns a point if and only if and (protocol specification, §“Group Hash into Jubjub”). The map reads as a -bit integer and a sign bit , rejecting and with no curve point (protocol specification, §“Jubjub”). Each point with is the image of exactly one , since and have different parities, and each of the two points is the image of two. The curve has points and its -torsion subgroup, the kernel of , has points: , and six with . The strings for which the hash succeeds are thus in bijection with the points with outside that subgroup, of which there are , so .
(d) Parts (b) and (c) and Construction 3.16 (3) combined by linearity of expectation over the indices below , each of which fails BIP 32 derivation with probability below . □
Remark 3.18 (Default addresses).
ZIP 316 fixes neither an order in which a wallet searches for a valid index nor a default unified address. The only normative defaults are ZIP 32’s per-protocol default diversifiers: for Sapling with the least valid index, for Orchard (ZIP 32, “Sapling diversifier derivation” and “Orchard diversifier and OVK derivation”). Issuing the unified address at the least index valid for every item is designed but unspecified (Definition 1.1).
Index and recovery across wallets, specified (ZIP 316, “Deriving a Unified Address from a UIVK”). Index is invalid for a Sapling item with probability (Proposition 3.17), so a wallet that requires a Sapling receiver often issues its first unified address at a later index, while some wallets, earlier than ZIP 316 or without a Sapling component in their unified addresses, always generate a transparent P2PKH address at index . Therefore every Zcash wallet, whether or not it supports unified addresses, MUST assume that transparent funds may exist at diversifier index of each ZIP 32 account, even where it would never generate a unified address at that index; reliable recovery of funds when key material moves between wallets depends on this. Its use in restoration is stated in §6.2.
3.7 Revision 2 containers
Definition 3.19 (Metadata items).
The following is Revision of ZIP 316, specified (Definition 1.1).
-
1.
Human-readable parts. A UA is either shielded-only, with human-readable part zu, which MUST NOT hold a transparent item (typecode or ), a Consumer rejecting any that does, or transparent-enabled, with tu. A UFVK uses uvf and a UIVK uvi; on Testnet test is appended. The human-readable part distinguishes a Revision container (u, uview, uivk) from a Revision one.
-
2.
Metadata items, typecodes to (Definition 3.7), MAY affect the interpretation of the container, MUST NOT be selected as receivers and MUST NOT confer viewing authority.
-
3.
MUST-understand items. Typecodes to are MUST-understand: a Consumer that does not recognise such an item MUST regard the whole container as unsupported and not process it further. This is the exception to the ignore rule of Definition 3.7.
-
4.
Registry. Typecodes to are unassigned; to are metadata that need not be understood, none assigned; is the Address Expiry Height and the Address Expiry Time, permitted in zu and tu addresses and not in Revision ; to are unassigned MUST-understand metadata; to are unassigned; and to are experimental. Producers MUST NOT include items whose typecodes are unassigned or not permitted for the type of the container.
-
5.
Address expiry items. An item of typecode holds the Address Expiry Height, an unsigned -bit little-endian integer; a UA carrying it MUST be considered expired when the height of the chain exceeds that value. An item of typecode holds the Address Expiry Time, an unsigned -bit little-endian Unix time; a UA carrying it MUST be considered expired when the current time is after that value. A Producer MAY include either, both or neither.
-
6.
Retroactive rule. A Revision container MUST NOT hold a MUST-understand metadata item, and a Consumer MUST reject one that does.
-
7.
Derivation. To derive a UIVK from a UFVK, or a UA from a UFVK or UIVK, a Consumer MUST understand every MUST-understand item of the source. The derived container MUST be Revision if the source holds any metadata item, and SHOULD be Revision if the source is. A UIVK derived from a UFVK MUST retain its and items unmodified. A UA derived from a UFVK or UIVK that carries (respectively ) MUST carry (respectively ) with a value at most that of the viewing key. Metadata items that need not be understood and are unrecognised are dropped under Constructions 3.13 and 3.16.
- 8.
Sources: ZIP 316, “Revisions”, “Metadata Items”, “Address Expiration Metadata”, “Typecode Registry”, “Requirements for both Unified Addresses and Unified Viewing Keys”, “Deriving a UIVK from a UFVK” and “Deriving a Unified Address from a UIVK”.
A Consumer that predates Revision does not recognise the Revision human-readable parts. Requiring MUST-understand items to appear only under those parts therefore enforces the MUST-understand rule even against such a Consumer (ZIP 316, “Rationale for making Revision 0 UA/UVKs with MUST-understand Typecodes invalid”).
Sender rules for expiring addresses, specified (ZIP 316, “Address Expiration Metadata” and its “Rationale”). The expiry height of a transaction is its field (Ironwood Guide, §“The transaction format”). A Sender supporting Revision MUST set a nonzero in a transaction to a UA with an Address Expiry Height, and MUST NOT send the transaction if the it would otherwise construct exceeds that height; lowering to the address’s value instead would reveal the destination’s expiry on chain. With only an Address Expiry Time, it SHOULD choose so that the transaction expires no more than hours after the current time. With both items both restrictions apply, and with several recipient UAs in one transaction all their constraints apply. A wallet MUST NOT send to an address it knows to have expired, and its error SHOULD suggest obtaining a current address. The choice of is stated in §9.3.
Linkability through metadata (ZIP 316, “Address Expiration Metadata”). Diversified UAs derived from one UIVK that hold only Sapling or Orchard receivers and no metadata are unlinkable (§3.1); with metadata items present this no longer holds, and it is RECOMMENDED that the expiry height and time of distinct derived addresses vary. Re-issuing the same receivers with different expiry metadata yields a visually distinct address that is directly linkable to the original, since the receivers are shared.
3.8 Recipient addresses
Definition 3.20 (Recipient address).
A recipient address is one of the following:
-
1.
a transparent address, P2PKH or P2SH, in its Base58Check encoding (Definition 3.6 (f));
-
2.
a Sapling payment address in its Bech32 encoding (Definition 3.6 (e));
- 3.
-
4.
a TEX address (transparent-source-only address): the Bech32m encoding, with human-readable part tex on Mainnet and textest on Testnet, of the -byte validating-key hash of a P2PKH address. It is obtained from a Base58Check P2PKH address whose decoding has bytes beginning with the lead bytes (Testnet ) by removing them, and it is parsed by requiring the human-readable part and exactly decoded bytes (ZIP 320, “Specification”).
Sprout addresses are not recipient addresses: no transaction adds value to the Sprout pool, and no typecode exists for them (§14.2; ZIP 316, “Requirements for both Unified Addresses and Unified Viewing Keys”). A Sender paying a TEX address, as any output of a transaction, MUST spend only transparent (P2SH or P2PKH) outputs in that transaction, and SHOULD send only to transparent outputs (ZIP 320, “Specification”; §11.3).
Two predicates on recipient addresses, defined here, are used by payment construction and by ZIP 321 (ZIP 321, “memo”; §14.2).
-
(i)
An address is memo-capable if and only if it is a Sapling payment address or a unified address that contains a Sapling or Orchard receiver, since a memo travels only in a note plaintext (Ironwood Guide, §“The note plaintext”). A memo reaches the recipient of a unified address only when the Sender selects a shielded receiver.
-
(ii)
An address is transparent-only if and only if it is a transparent or TEX address, or a unified address whose non-metadata items are all transparent receivers, which is possible only as a Revision tu address.