4 OrchardZSA Actions and Action Groups
This section shows that the membership exemption of Orchard dummy notes is unsound once the value base of an Action is a witness, and defines the Split Inputs that replace dummy consumed notes for Custom Assets (§4.1); constructs the split nullifier and proves its independence from the nullifier of the copied note (§4.2); states the OrchardZSA Action statement as a delta on the Orchard one, with named conditions (§4.3); states the assumptions on its proof and proves that a Split Input requires the spend authority of the copied note (§4.4); and defines the Action Group (§4.5). The objects of the section are taken from ZIP 226 and ZIP 228, both Draft, with the rules of ZIP 227 that bound the number of Action Groups. The Orchard objects they modify are those of the Ironwood Guide and are cited, not restated.
4.1 Dummy notes and Split Inputs
By the Ironwood Guide’s Definition “Dummy notes” (§“Actions, bundles, and dummy notes”), an Action whose consumed side is unused consumes a dummy note of value : under a fresh key or, when and the created note is real, at the expanded receiver of the created note and under the key from which that receiver derives. Condition A3 of that volume’s Definition “Orchard Action statement”, namely or some evaluation of in the fold returns , exempts every consumed note of value from membership (protocol specification, §“Dummy Notes (Orchard)” and §“Action Statement (Orchard)”). In the Orchard protocol the exemption is sound for value: condition A4 multiplies the value by the fixed generator (Ironwood Guide, Definition “Net value commitment”), so a consumed note of value contributes , whatever path it fails to prove. The per-Asset value commitment of Definition 3.8 multiplies by a witnessed Asset Base instead. The next proposition shows that the exemption, kept unchanged, then admits a balance violation.
Proposition 4.1 (Unsoundness of the dummy exemption under a witnessed base).
Let be the relation obtained from the Ironwood Guide’s Definition “Orchard Action statement” by adding an auxiliary input and making three replacements: in A1 and A2, the commitment is replaced by of Definition 3.2 with Asset Base for both notes; in A4, the net value commitment becomes
as in Definition 3.8; condition A3 and conditions A5 to A10 are unchanged, so a consumed note of value is exempt from membership whatever is. Then for every there is a bundle of two Actions whose witnesses satisfy , with balancing value and no burn, whose binding signature verifies, and which creates a ZEC note, of Asset Base , of value while every consumed note has value :
-
Action 1 witnesses , and ;
-
Action 2 witnesses , a dummy consumed note and .
More generally, a witnessed base with known coefficients over Asset Bases contributes for a committed value , so a value committed on cancels values committed on the . This is the attack of ZIP 226, “Rationale for Split Notes”: without the enforcement “the prover could input a multiple (or linear combination) of an existing Asset Base, and thereby attack the network by overflowing the ZEC value balance and hence counterfeiting ZEC funds”. Status (Definition 1.3): proved here; ZIP 226 states the attack in words only.
Proof.
The point is not , since has prime order , so Action 1 is well typed. Both consumed notes have value , so A3 holds for both Actions without a path, and A8 holds for either value of ; A9 holds with . The remaining conditions hold when the commitments, the nullifiers and are computed from the witness by their definitions, under a key of the prover; each consumed note is placed at the expanded receiver of the note its Action creates, so that A10 holds for either value of , as in the Ironwood Guide’s Remark “Meaning of A10”. The net value commitments are
With balancing value and no burn, the Ironwood Guide’s Definition “Binding validating key” gives
whose discrete logarithm to the base the prover knows, so that volume’s Construction “Binding signature” produces a valid signature. Action 2 creates a ZEC note of value , and no consumed note carries value. For the general case, for every integer , by bilinearity of scalar multiplication, and the same computation applies. □
Definition 4.2 (Split Input and Split Action).
Let with . A Split Input of Asset Base is an OrchardZSA note (Definition 3.1), whose extracted commitment
(Definition 3.2) is a leaf of the note commitment tree under the anchor of the consuming Action, consumed by an Action that sets the witness bit of the statement defined in “The OrchardZSA Action statement” (§4.3). A Split Input differs from a spend of in two respects only: its value is replaced by in the net value commitment, while the commitment still opens with the true value ; and the Action publishes the split nullifier of “Nullifiers of OrchardZSA notes” (§4.2) in place of the nullifier of . A Split Action is an Action whose consumed note is a Split Input. ZIP 226 calls “a previously issued input note (that is, a note that has previously been included in the Merkle tree)”; any leaf of Asset Base qualifies, whether its note was created by an Action or by issuance (ZIP 226, “Terminology” and “Split Notes”). Class: specified.
Padding rule. In a bundle (Ironwood Guide, Definition “Bundle”) of OrchardZSA Actions, for each Custom Asset whose Asset Base has fewer consumed notes than created notes, the sender gives each input-less Action of a Split Input of (ZIP 226, “Split Notes”). Actions of ZEC keep the dummy consumed notes of the Ironwood Guide’s Definition “Dummy notes”; Actions of Custom Assets take no dummy consumed note (ZIP 226, “Backward Compatibility”). Both regimes occur within one bundle of OrchardZSA Actions. That bundle is not the Orchard-pool bundle of a version- transaction: version is the format of ZIP 229, which carries no ZSA fields (ZIP 229, “Non-requirements”). ZIP 226 enforces in the statement that every consumed note of a Custom Asset, split or not and of any value, is a leaf: “for Custom Assets we enforce that every input note to an OrchardZSA Action must be proven to exist in the set of note commitments” (“Rationale for Split Notes”). The condition is constructed in “The OrchardZSA Action statement” (§4.3), and Corollary 9.4, in “Security”, states what it yields for the Asset Base of the created note.
Remark 4.3 (Choice of the copied note).
ZIP 226, “Split Notes”, lets the sender copy one of three notes of Asset Base :
-
(1)
another note of consumed by a real spend in the same bundle, but not by this Split Input;
-
(2)
a different unspent note of , which is not thereby spent;
-
(3)
an already spent note of , the zeroed value preventing a second spend.
It states that “we do not care about whether the previously issued note copied to create a Split Input is owned by the sender, or whether it was nullified before”. Proposition 4.12, in “The OrchardZSA Action proof” (§4.4), states which of these choices are available to a sender who does not hold the spend authority of the copied note. Under Remark 1.7, if OrchardZSA notes are in the Orchard pool, which ZIP 258, “Consensus rules from NU6.3 activation”, restricts to Actions with , then a Split Action whose created note is at an expanded receiver other than that of the copied note violates the cross-address rule. ZIP 226 does not address this case.
4.2 Nullifiers of OrchardZSA notes
An OrchardZSA note consumed by a real spend, with , has the Orchard nullifier of the Ironwood Guide’s Definition “Nullifier”:
with of Definition 3.2 (ZIP 226, “Note Structure and Commitment”: “generated in the same manner as in the Orchard protocol”; protocol specification, §“Computing values and Nullifiers”). It depends on the Asset Base only through ; for a note with it is the Orchard nullifier bit for bit. The extension of the Ironwood Guide’s Lemma “One nullifier per note” to OrchardZSA notes is Lemma 9.6, in “Security”.
A Split Action publishes one nullifier, which enters the nullifier set of its pool, and a nullifier must not repeat, either within a transaction or across the block chain (Ironwood Guide, §“Nullifier sets”; protocol specification, §“Nullifier Sets”). The copied note may be unspent, choice (2) of Remark 4.3, or spent in the same bundle, choice (1). Publishing its nullifier would, in the first case, make it unspendable and, in the second, repeat a nullifier within the transaction, which invalidates the transaction. The nullifier of a Split Input must therefore differ from that of the copied note. ZIP 226 states the purpose of the change as privacy: it is made “to prevent the identification of notes” (“Circuit Statement”).
Construction 4.4 (Split nullifier).
Let , the input of the second row of Table 3. For a Split Input with nullifier deriving key , element and commitment , the sender draws uniformly from and sets
The split nullifier is
Against the Ironwood Guide’s Definition “Nullifier” there are two changes: is replaced by the fresh , and the fixed point is added before extraction. The derivation adds one row to that volume’s Construction “Domain bytes of PRF expansion”:
| Key | Remainder | Output | Section | ||
|---|---|---|---|---|---|
| §4.2 |
The key is secret, uniform and used once. The byte is reserved for this use by ZIP 2005’s amendment of §“Sending Notes (Orchard)” (ZIP 2005, “Changes to the Protocol Specification”; ZIP 226, “Split Notes”); the specification’s own list of expansion uses (§“Pseudo Random Functions”) does not record it, and ZIP 2005’s amendment of that list adds and . It differs from the bytes of , and of and of of the Orchard sending derivations (protocol specification, §“Sending Notes (Orchard)”; Definition 3.5). Class: specified, as a sender rule; Remark 4.8 states what the statement enforces.
Proposition 4.5 (Independence of split nullifiers).
Let be an OrchardZSA note with commitment , elements , and nullifier under . For let be the split nullifier of a copy of with .
-
(i)
Under the Ironwood Guide’s Assumptions “GroupHash as a random oracle” and “Discrete logarithms on Pallas”, no efficient algorithm outputs , a note with the opening of its commitment, and with , except with negligible probability. This holds for every choice of , honest or not.
-
(ii)
Let be uniform and used only for this derivation, and let . To an adversary that knows , and the full viewing key, the split nullifier is indistinguishable from for uniform on , with advantage at most
where bounds the Ironwood Guide’s Assumption “Pseudorandomness of PRF expansion” for one query, is the statistical distance of on a uniform -byte input from the uniform distribution on , and as in that volume’s Proposition “Nullifier unlinkability”.
Status (Definition 1.3): proved here for the specified construction. Part (ii) concerns honest senders, since the statement does not enforce the derivation (Remark 4.8).
Proof.
(i) Write
and , . By the Ironwood Guide’s Lemma “Coordinate extraction identifies opposite points”, means . With the sign ,
with the sign ,
Given its opening, is a known integer combination of the Sinsemilla generators of its domain and of its blinding base, by the unfolding of the Ironwood Guide’s Construction “Sinsemilla hash on Pallas” used in the proof of its Proposition “Collision resistance of the Sinsemilla instances”; in either branch of Definition 3.2 these generators are values of at inputs other than and . In both cases has coefficient , and its input differs from every other input involved (Lemma 2.8), so the algorithm has output a non-trivial relation among values of at distinct inputs, which the Ironwood Guide’s Lemma “Relations among fixed generators” excludes except with negligible probability. This is the role of the offset , which ZIP 226 does not state: without it, reproduces .
(ii) The hybrids follow the proof of the Ironwood Guide’s Proposition “Nullifier unlinkability”. First, , evaluated at the single input , is replaced by a uniform -byte string, at cost : the key is used nowhere else, and the rest of the game is an efficient function of the answer and of . Second, of that uniform string is replaced by a uniform , at cost (Math Guide, §“Uniform sampling and the bias of modular reduction”; Ironwood Guide, §“Pseudorandom functions and field reductions”). Translation by is a bijection of , so is then uniform on and independent of , and all else. Third, , read in , is replaced by a uniform scalar , at cost , the statistical distance computed in the cited proposition. Since generates the group of prime order , the point is then uniform on whatever and are, and the split nullifier is of a uniform point. □
In the model of the Ironwood Guide’s Assumption “GroupHash as a random oracle”, the event excluded in part (ii) has probability .
4.3 The OrchardZSA Action statement
The statement is defined as a delta on the relation of the Ironwood Guide’s Definition “Orchard Action statement”, itself a relation in the sense of the Crypto Guide’s Definition “Language, relation, witness” (§“Languages, relations, and witnesses”). Notation, types and conditions not named below are those of that definition; conditions A6 to A9 are cited by name and not restated.
Definition 4.6 (OrchardZSA Action statement).
Base. The seven components of the primary input of the Ironwood Guide’s Definition “Orchard Action statement” other than , and its conditions A1 to A9. The input and condition A10 are omitted (Remark 4.7).
Primary input.
with the first seven components typed as in the cited definition and .
Auxiliary input. The auxiliary input of the cited definition, together with
Notation. Let if and otherwise. With and the -bit messages of the cited definition, built from the witnessed diversified bases, write for the commitment of Definition 3.2 with replaced by the message built from these arguments: in the native branch, and , or , in the custom branch. Let be as in Construction 4.4.
Relation. The relation is the set of pairs of the types above that satisfy the following conditions.
-
A1′.
Old note commitment integrity:
-
A2′.
New note commitment integrity:
with and the same as in A1′.
-
C1.
Native indicator: if and only if .
-
C2.
Pause: if , then .
-
A3′.
Merkle path validity: and , or , or some evaluation of in the fold returns ; the value , the fold and the encoding bits are those of A3.
- A4′.
-
C3.
Split only for Custom Assets: if , then .
- A5′.
-
A6, A7.
Spend authority and diversified address integrity: unchanged and unconditional; no factor of relaxes them.
-
A8, A9.
Enable spend flag and enable output flag: unchanged; A8 reads , not , and A9 reads .
(ZIP 226, “Circuit Statement”, paragraphs “Asset Base Equality”, “The enableZSA Flag”, “Value Commitment Correctness” and “Asset Identifier Consistency for Split Actions”; ZIP 226, “Split Notes” and “Note Structure and Commitment”; protocol specification, §“Action Statement (Orchard)”.) Class: specified at statement level; its status is stated in Remark 4.7.
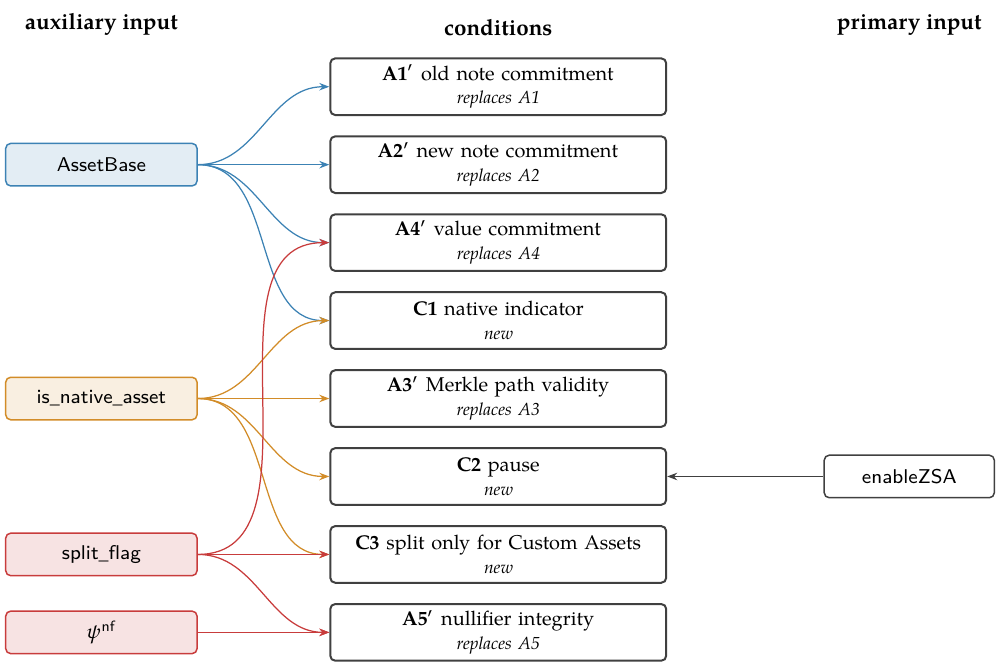
One witness. Conditions A1′, A2′ and A4′ use the single witnessed , so the consumed and the created note of an Action have one Asset Base, and its net value commitment is on that base.
Native branch. By C1 and the case split of Definition 3.2, an Action with and satisfies A1′, A2′, A4′ and A5′ exactly when and it satisfies the Orchard A1, A2, A4 and A5.
Pause. With , C2 and C1 force , and C3 then forces , so the relation admits only Orchard Actions.
Membership. Since , the first disjunct of A3′ holds only for a consumed ZEC note of value . Every consumed note of a Custom Asset, split or not and of any value, satisfies or the clause. The clause gives no escape: for witnesses extracted under Assumption 4.9, the argument of the Ironwood Guide’s Remark “-weakened conditions”, by that volume’s Proposition “Collision resistance of the Sinsemilla instances” (iii) under its Assumptions “Discrete logarithms on Pallas” and “GroupHash as a random oracle”, excludes it except with negligible probability; the same holds for the cases of A1′ and A2′ in both branches of , by Proposition 3.3(c) for the custom branch.
Split Actions. By A4′ the copied value never enters . By A8, which reads , a Split Action that copies a note of non-zero value requires , while one that copies a note of value does not.
These consequences are direct from the cited definitions and from the Ironwood Guide’s Remark “-weakened conditions”, with Assumption 4.9 in place of that volume’s knowledge-soundness assumption (ZIP 226, “Circuit Statement” and “Overview”). Table 5 pairs each condition with the Orchard condition it replaces and its ZIP 226 paragraph; Figure 1 draws the new witnesses and the conditions that read them.
| Condition | Replaces | ZIP 226, “Circuit Statement”, paragraph |
|---|---|---|
| A1′ | A1 | “Asset Base Equality” |
| A2′ | A2 | “Asset Base Equality” |
| C1 | none | “Asset Base Equality” (the witness ) |
| C2 | none | “The enableZSA Flag” |
| A3′ | A3 | “Asset Identifier Consistency for Split Actions” (Merkle Path Validity) |
| A4′ | A4 | “Value Commitment Correctness”; “Asset Identifier Consistency for Split Actions” () |
| C3 | none | “Asset Identifier Consistency for Split Actions” |
| A5′ | A5 | “Asset Identifier Consistency for Split Actions” (Nullifier Integrity), with “Split Notes” for the formula and “Note Structure and Commitment” for |
| A6 to A9 | themselves | none (unchanged) |
| A10 | omitted | none (Remark 4.7) |
Remark 4.7 (Status of the OrchardZSA Action statement).
The delta is specified at statement level (ZIP 226, Draft, “Circuit Statement”). ZIP 226 states it against the specification’s statement with seven primary inputs and conditions A1 to A9. The current Orchard statement has the eighth primary input and condition A10 (Ironwood Guide, Definition “Orchard Action statement” and Remark “Status”; protocol specification, §“Action Descriptions”; ZIP 258, “Consensus rules from NU6.3 activation”), which ZIP 226 never mentions. The composition of the delta with A10 is therefore an open problem (Definition 1.2). The statement uses , which ZIP 226 never lists as a primary input. The encoded instance of the current Orchard statement has ten elements, the nine that encode its first seven primary inputs and (Ironwood Guide, §“The Action statement”); no live text places in it, so its position is an open problem. ZIP 226 defers “All modifications in the Circuit” to an unversioned document outside the ZIPs, “Modifications to the Orchard circuit for the OrchardZSA Protocol”; no ZIP fixes a complete OrchardZSA circuit, which is designed but unspecified. The reading of A8 on is specified by the delta, which leaves A8 unchanged; only its confirmation in that circuit document is designed but unspecified, and Table 7 records it.
Remark 4.8 (What the OrchardZSA statement does not check).
Items (i) to (iii) of the Ironwood Guide’s Remark “What the statement does not check” carry over. In addition:
-
(iv)
The witness is constrained only through A5′ to the published nullifier. For only the equality is switched off, and no condition derives from a seed. The derivation of Construction 4.4 is therefore a sender rule whose formula is specified and which nothing enforces: is transmitted nowhere, and no text proposes an enforcement. Proposition 4.5(i) holds for every ; part (ii) holds for senders that follow the rule.
-
(v)
The derivations of and from are unchecked, as for Orchard.
-
(vi)
The witnessed is checked only against the consumed leaf, through A1′ and A3′, and never against a record of issued Assets. Lemma 9.3, in “Security”, concerns the leaves.
-
(vii)
The statement does not check that the prover owns the copied note of a Split Input beyond A6 and A7; this is the subject of Proposition 4.12.
(ZIP 226, “Split Notes” and “Circuit Statement”.)
4.4 The OrchardZSA Action proof
The Ironwood Guide’s Assumptions “Knowledge soundness of the Action proof” and “Zero knowledge of the Action proof” name the relation and its verifying key. The corresponding assumptions for are stated here in the same form; the OrchardZSA verifying key denotes the verifying key of a circuit for , which no ZIP names.
Assumption 4.9 (Knowledge soundness of the OrchardZSA Action proof).
Let the hash of the Fiat–Shamir transform be modelled as a random oracle. For every efficient adversary that outputs primary inputs and an aggregate proof , there is an efficient extractor, with access to the adversary and to its random-oracle queries, that outputs auxiliary inputs such that the probability of the event
| is accepted for under the OrchardZSA verifying key | ||
is negligible. This is the knowledge-soundness clause of the Crypto Guide’s Definition “SNARK” (§“SNARKs: succinct non-interactive arguments of knowledge”) for the relation of Definition 4.6, for a Halo 2 proof (Halo 2 Guide, §“The Halo 2 proof system” and §“A rigorous treatment of knowledge soundness”), the primary input bound to the proof as in the Halo 2 Guide, §“Instance columns and binding the public statement”. It includes that every satisfying assignment of the circuit yields a witness of ; in particular, the multiplication of A4′ is by the witnessed and nothing else. No ZIP names the circuit or the verifying key: the assumption concerns a designed but unspecified object.
Assumption 4.10 (Zero knowledge of the OrchardZSA Action proof).
Let the hash of the Fiat–Shamir transform be modelled as a programmable random oracle. There is an efficient simulator that, given only and programming the random oracle, outputs an aggregate proof statistically indistinguishable from an honest proof under the OrchardZSA verifying key, for any with for every , against every distinguisher that makes polynomially many random-oracle queries. This is zero knowledge of statistical grade in the non-interactive, random-oracle form of the Crypto Guide’s Definition “Zero knowledge” (§“The simulation paradigm and zero knowledge”), for a Halo 2 proof (Halo 2 Guide, §“Zero knowledge: hiding the witness in Halo 2”). It concerns the same designed but unspecified circuit and key.
Remark 4.11 (Circuit, verifying key and proof length).
The statement is specified at delta level (ZIP 226). Its arithmetisation exists only in the document outside the ZIPs named in Remark 4.7, so the circuit and its verifying key are designed but unspecified, and Assumptions 4.9 and 4.10 are the only hypotheses through which later results depend on them. Condition A4′ is sound only if the circuit multiplies by the witnessed and nothing else. The Orchard variable-base scalar multiplication was corrected at NU6.2 because it left the base under-constrained (ZIP 257, “NU6.2 deployment”). ZIP 226, which turns the value base into a witness (“Value Commitment Correctness”), does not mention the correction, which any OrchardZSA circuit must carry. ZIP 257 made the Orchard proof length bytes, for Actions, a consensus rule (“Canonical Orchard Action proof length”). No ZIP fixes an OrchardZSA proof length, which the circuit determines and which no live text contradicts: it is designed but unspecified, as the circuit and the verifying key are.
Proposition 4.12 (Ownership of Split Inputs).
Consider the Ironwood Guide’s Definition “Spend-authority experiment” with in place of : a key generated with , the adversary holding its full viewing key but not . Under Assumption 4.9 and the Ironwood Guide’s Assumptions “Discrete logarithms on Pallas”, “GroupHash as a random oracle”, “The RedPallas hash as a random oracle” and “Pseudorandomness of PRF expansion”, no efficient adversary outputs, except with negligible probability, a block chain with an accepted Split Action whose witness copies a leaf that is a note of the key, and whose spend-authorisation signature is valid under its on a signature digest for which it made no signing query with that . Consequently the sentence of ZIP 226, “Split Notes”, “we do not care about whether the previously issued note copied to create a Split Input is owned by the sender, or whether it was nullified before” holds for spentness and not for ownership: a sender can use choices (2) and (3) of Remark 4.3 only with the spend authority of the copied note, except for a note whose key is public, such as a reference note (Proposition 6.11). Status (Definition 1.3): proved here from specified conditions; conditional on Assumption 4.9, which concerns the designed but unspecified circuit.
Proof.
The proof is a reduction to the proof of the Ironwood Guide’s Theorem “Spend authority”. By Assumption 4.9 the extractor yields, for the accepted Split Action, a witness of with . By C3, , so A3′ gives outside its case, which is excluded as in the consequences of Definition 4.6; with the anchor rule, the Ironwood Guide’s Proposition “Membership soundness” makes a leaf. Condition A1′ with Proposition 3.3(b) makes the witnessed consumed note the note of that leaf, so its witnessed expanded receiver is the receiver of the leaf’s note, a note of the key; the witness therefore consumes a note of the key in the sense of the experiment. Conditions A6 and A7, unchanged and unconditional, then bind to a randomisation of of that key, by the Ironwood Guide’s Proposition “Binding of to ” and Lemma “Coordinate extraction identifies opposite points”, and a valid signature under without a matching signing query contradicts that volume’s Proposition “Unforgeability under re-randomisation”, exactly as in steps (1) to (5) of the proof of Theorem “Spend authority”. Neither nor enters A6 or A7, the only conditions that proof uses; A1′ and membership serve here only to identify the witnessed receiver with that of the copied leaf’s note, so the steps apply unchanged.
4.5 Action Groups
Definition 4.13 (Action Group).
An Action Group is a non-empty finite sequence of OrchardZSA Actions together with one anchor , the flags , and in , and one aggregate proof for the relation of Definition 4.6 at the primary inputs
of its Actions . Each Action carries the public fields of an Orchard Action description (Ironwood Guide, Definition “Action description”) and its own spend-authorisation signature under . The term is that of ZIP 228, “Terminology”: Actions that share the tuple . ZIP 227, “Specification: Consensus Rule Changes”, requires and at most one Action Group per transaction, so the fifth component is constant and is omitted. The nullifier of the first Action of the Action Group is the value that issuance uses (ZIP 227, “Computation of ”). The Action Group has no burn set; the remaining components of a transaction’s bundle are defined in “Burn sets and OrchardZSA bundles” (§5.1). Class: specified.
The structure is specified by ZIPs 226 to 228, all Draft. Its encoding exists only in ZIP 230, which is Withdrawn; the layout that ZIP 230 calls version is not the version of ZIP 229, which has no Action Groups (ZIP 229, “Transaction Format”). The byte lengths of the note ciphertext and of an Action depend on a plaintext encoding that no current ZIP defines (Definition 3.7). The flag has no flag bit in any current format. ZIP 230 assigns it bit of the Orchard flags byte, which ZIP 229, “Consensus Rules”, reserves as in version and which is in the Ironwood flags byte (Ironwood Guide, §“Bundle flags”; ZIP 258, “Consensus rules from NU6.3 activation”). The design conflicts with live text, so the flag bit is an open problem (Definition 1.2).