12 Partially created transactions (PCZT)
This section states the protocol by which the construction, proving and authorisation of one transaction are divided among several parties (ZIP 374). It defines the partially created transaction, its versions and the kinds of its fields; the roles that act on it and the modification state they maintain; its fields, its canonical empty bundles and its encoding; the version- 2 rules for deferred anchors and the Ironwood bundle; construction and IO finalisation; signing, with the theorem that a Signer’s signatures authorise exactly what it checked; proving; combining and redaction, with the order independence of proving and signing and the data a PCZT discloses; and spend finalisation and extraction.
12.1 The PCZT and its requirements
Definition 12.1 (Partially created transaction).
A partially created transaction (PCZT) of one transaction is a value of the typed record of §12.3 for one PCZT version, exchanged among the parties to the creation of that transaction. It carries the data each role needs for its step (adding inputs and outputs, proving, signing, extracting) and accumulates proofs and signatures until the transaction is complete; since it carries all data a signer needs, a signer can be offline. A PCZT consists of a Global record and one bundle per protocol: transparent, Sapling, Orchard and, from version 2 , Ironwood. Every bundle is present in every PCZT, empty bundles included, because metadata of a protocol may have to be held before it is known whether that protocol has inputs or outputs (ZIP 374, “Abstract”, “Specification” and “Structure”).
The PCZT protocol is specified (Definition 1.1) in ZIP 374, Revision 0 , whose status is that of Table 1; no consensus rule depends on it. It covers transactions of versions 5 and 6 only: it supports neither Sprout nor version 4 or earlier, since version 4 predates the ZIP 244 digest and several of the role separations of this section, the independence of proving from signing in particular, fail for it (ZIP 374, “Specification”). The protocol serves signing devices that hold spending keys but can neither compute proofs nor hold a whole transaction; proof delegation, the prover needing note data and the full viewing key but no spending key; transactions with several signers (threshold signing, the transparent multisignature wallets of ZIP 48) or several contributors of inputs, whose parallel contributions are merged; and, for version 6 , pre-authorisation, in which the signatures precede the choice of anchors, the witnesses and the proofs (ZIP 374, “Motivation”).
ZIP 374, “Requirements”, states six requirements, recorded here as the ZIP’s and not proved as such:
-
(R1)
every intermediate state of the creation of a version- 5 or version- 6 transaction is representable, and adding inputs and outputs, finalising the input and output set, attaching lookup data, proving, signing, merging parallel contributions and extracting are each performable by distinct entities, in an order constrained only by data dependencies;
-
(R2)
no spending key material is required, the keys of dummy spends excepted, which authorise nothing of value and are removable before any Signer sees the PCZT;
-
(R3)
a Signer determines from the PCZT alone what it authorises (amounts, recipients, and the correspondence between the fields it signs and the values shown to its user), and data a Signer does not need is removable;
-
(R4)
merging two PCZTs of the same transaction is deterministic and fails on any conflict;
-
(R5)
for version 6 , signatures can be produced while anchors, witnesses and proofs are absent, and supplying them later leaves the signatures valid;
-
(R6)
the encoding is compact and strictly versioned, so that no data is read under another version’s rules.
Requirement (R3) is made a theorem in §12.7, (R5) a proposition in §12.5 and (R4) a construction in §12.9.
Definition 12.2 (PCZT versions).
Version 1 represents transactions of version 5 (ZIP 225); version 2 represents transactions of versions 5 and 6 (ZIP 229). The PCZT version does not fix the transaction version: a version- 2 PCZT carries a transaction of version 5 or 6 , subject to the per-field rules, and a version- 1 PCZT only one of version 5 . Relative to version 1 , version 2 adds the Ironwood bundle; a note version in { V2, V3 } per Orchard-protocol bundle; anchors that may be absent; and an encoding that writes a bundle equal to its slot’s canonical empty bundle as absent (ZIP 374, “Versioning”). The fields are made exact in §12.3 and the encoding in §12.4.
No field can be added within a version: the encoding is positional, and a parser cannot skip a field it does not know. A PCZT has no non-proprietary key–value maps, so every field of a version is known in advance and a Signer’s view of a PCZT is complete; the proprietary maps are the only extension point within a version, and MUST be used for internal processes only. The format evolves by new versions, which the four-byte version of the header distinguishes. Implementations SHOULD parse every specified version and SHOULD emit the oldest version able to represent a PCZT’s state when interoperating with entities that may lack the newest; conversion between versions is lossless exactly when the target version represents the state (ZIP 374, “Extensibility” and “Proprietary Use fields”). The states that version 1 cannot represent are listed in §12.4.
Definition 12.3 (Field kinds of a PCZT).
Every field of a PCZT is of one of three kinds (ZIP 374, “Structure”):
-
(i)
effecting data, required fields that are part of the final transaction and are always present, committed to by the signature digest (Ironwood Guide, §“Transaction digests and signatures”);
-
(ii)
authorising data, initially absent and filled as roles act: proofs, signatures, binding signing keys and, in a transaction of version 6 , the anchors;
-
(iii)
context data, which enables roles to act and never enters the final transaction: note openings, keys, witnesses, derivation records and address strings.
In a transaction of version 5 the anchors are effecting data (ZIP 374, “Anchors and pre-authorization”).
The signature digest commits to every non-transparent effecting field as soon as any input is signed, so no shielded analogue of the transparent hash types that leave inputs or outputs open exists. The transparent and the shielded modifiable flags of §12.2 are therefore kept apart, so that a purely transparent PCZT behaves as a partially signed Bitcoin transaction of BIP 174 and BIP 370 does (ZIP 374, “Separate Shielded Modifiable Flag from Transparent Modifiable Flags”).
12.2 Roles and the modification state
Definition 12.4 (Roles).
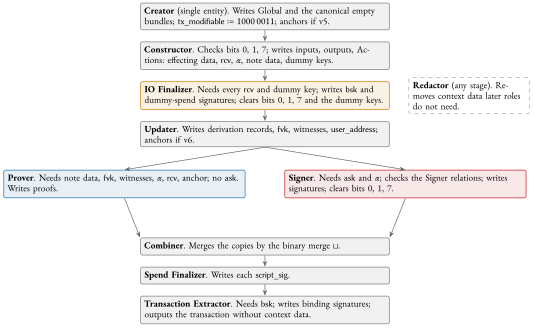
A role is a partial map from PCZTs to PCZTs, undefined where the role fails; a role that draws randomness is a family of such maps indexed by its random coins, and the Combiner maps a finite set of PCZTs to one. The roles, with the parties that may execute them (ZIP 374, “Specification” and “Roles”), are:
-
(1)
Creator (a single entity): chooses the transaction version and consensus branch identifier, and sets the Global fields and the empty bundles;
-
(2)
Constructor: adds transparent inputs and outputs, Sapling spends and outputs, and Orchard-protocol Actions;
-
(3)
IO Finalizer (anyone): declares the input and output set final, computes the binding signing keys and signs dummy spends;
-
(4)
Updater (anyone): adds data later roles need, such as derivation records, full viewing keys, witnesses and, for version 6 , anchors;
-
(5)
Redactor (anyone): removes data later roles do not need;
-
(6)
Prover (a holder of the note data): adds proofs;
-
(7)
Signer (a holder of a spending key): adds signatures;
-
(8)
Combiner (anyone): merges PCZTs;
-
(9)
Spend Finalizer (anyone): assembles transparent unlocking scripts;
-
(10)
Transaction Extractor (anyone): checks completeness and produces the transaction.
The lifecycle runs the Creator, the Constructors, the IO Finalizer and the Updaters, then the Provers and the Signers, the Combiners and the Redactors, and last the Spend Finalizer and the Transaction Extractor. A Verifier is not a role: it is an inspection of a PCZT’s internal consistency, for example the relations of §12.7, performed on behalf of an entity, such as a hardware signer, that trusts it and cannot perform the checks itself (ZIP 374, “Verifier”).
Definition 12.5 (Modification state).
The Global field
-
(i)
bit 0 , transparent inputs modifiable, and bit 1 , transparent outputs modifiable: each set by the Creator, checked, and possibly cleared, by a Constructor before it adds an input or output of its kind, cleared by the IO Finalizer when shielded spends or outputs exist, and merged by AND;
-
(ii)
bit 2 , a signature with hash type SIGHASH _ SINGLE is present: cleared by the Creator, set by a Signer that adds such a signature, read by a Constructor, which then preserves the pairing of each such input with its output, and merged by OR;
-
(iii)
bits 3 to 6 : zero, which ZIP 374 requires in version 1 and the Combiner requires of every PCZT it merges;
-
(iv)
bit 7 , shielded modifiable: set by the Creator, checked, and possibly cleared, by a Constructor before it adds a shielded spend or output, cleared by the IO Finalizer when shielded spends or outputs exist and by every Signer, and merged by AND.
The Creator’s value is therefore 1000 0011 in binary.
Signing freezes the effects. After adding a shielded signature a Signer clears bits 0 , 1 and 7 : every shielded signature, spend-authorisation and binding alike, is on the one signature digest, which commits to all effecting data (Ironwood Guide, §“Transaction digests and signatures”, Proposition “Bundle binding”), and no shielded hash type leaves an input or output open. After adding a transparent signature it clears bit 0 unless the hash type has ANYONECANPAY , clears bit 1 unless its base type is NONE , sets bit 2 if its base type is SINGLE , with or without ANYONECANPAY , and clears bit 7 (ZIP 374, “Global” and “Signer”).
A wallet executing a plan (Definition 11.2) acts as Creator, Constructor, IO Finalizer and Updater. It builds the bundles by Construction 11.18 and then, as Updater, attaches to each non-dummy Orchard-pool, Ironwood-pool and Sapling spend the derivation record of §12.3, with the seed fingerprint of Construction 2.2 and the path (32 ′, coin _ type ′, account ′) of Definition 2.7; to each transparent input the BIP 44 path (44 ′, coin _ type ′, account ′, scope, index) , the last two components non-hardened; and to each output that pays a payment of the plan (Definition 11.1) that payment’s address string as user _ address , which a Signer checks (§12.7) (ZIP 374, “Updater” and “Zip32Derivation”; ZIP 32; BIP 44).
12.3 Fields
Definition 12.6 (PCZT fields).
Types. The types u8 , u32 and u64
are the unsigned integers of that width, i128 the signed
integers of 128 bits and
- Global.
-
tx _ version ∈ u32 , which is 5 in version 1 and 5 or 6 in version 2 ; version _ group _ id ∈ u32 , consistent with it (ZIP 225, ZIP 229); consensus _ branch _ id ∈ u32 , which for tx _ version = 6 names an upgrade at which version 6 is supported, NU6.3 or later, that of NU7 being 0x77190AD9 (ZIP 259, “NU7 network constants”); fallback _ lock _ time ∈ Opt (u32) , absence meaning 0 ; expiry _ height ∈ u32 (ZIP 203); coin _ type ∈ u32 , the SLIP 44 coin type, which is not part of the transaction and against which roles check network-specific data; tx _ modifiable ∈ u8 (Definition 12.5); proprietary ∈ P . - Transparent bundle.
-
inputs ∈ List (TI) and outputs ∈ List (TO) . An input TI : prevout _ txid ∈ B 32 ; prevout _ index ∈ u32 ; sequence ∈ Opt (u32) , absence meaning 2 32 − 1 ; required _ time _ lock _ time ∈ Opt (u32) , at least 500, 000, 000 ; required _ height _ lock _ time ∈ Opt (u32) , in { 1, ..., 499, 999, 999 } ; script _ sig ∈ Opt (List (u8)) ; value ∈ u64 ; script _ pubkey ∈ List (u8) ; redeem _ script ∈ Opt (List (u8)) ; partial _ signatures ∈ Map (B 33, List (u8)) ; sighash _ type ∈ u8 ; bip32 _ derivation ∈ Map (B 33, D) ; four preimage maps, for RIPEMD160, SHA256, HASH160 and HASH256, of types Map (B 20, List (u8)) , Map (B 32, List (u8)) , Map (B 20, List (u8)) and Map (B 32, List (u8)) in that order; proprietary ∈ P . An output TO : value ∈ u64 ; script _ pubkey ∈ List (u8) ; redeem _ script ∈ Opt (List (u8)) ; bip32 _ derivation ∈ Map (B 33, D) ; user _ address ∈ Opt (Str) ; proprietary ∈ P . - Sapling bundle.
-
spends ∈ List (SS) ; outputs ∈ List (SO) ; value _ sum ∈ i128 , the net value of the spends minus the outputs; anchor ∈ B 32 (v1) or Opt (B 32) (v2); bsk ∈ Opt (B 32) . A spend SS : effecting cv, nf, rk ∈ B 32 ; zkproof ∈ Opt (B 192) ; spend _ auth _ sig ∈ Opt (B 64) ; recipient ∈ Opt (B 43) ; value ∈ Opt (u64) ; rcm ∈ Opt (B 32) and rseed ∈ Opt (B 32) , at most one set, by whether the note predates ZIP 212; rcv ∈ Opt (B 32) ; the proof generation key (ak, nsk) ∈ Opt (B 32 × B 32) ; witness ∈ Opt (u32 × (B 32) 32) ; α ∈ Opt (B 32) ; a derivation record in Opt (D) ; dummy _ ask ∈ Opt (B 32) ; proprietary ∈ P . An output SO : effecting cv, cmu, epk ∈ B 32 and the ciphertexts C enc, C out ∈ List (u8) , whose lengths depend on the transaction version; zkproof ∈ Opt (B 192) ; recipient ∈ Opt (B 43) ; value ∈ Opt (u64) ; rseed, rcv, ock ∈ Opt (B 32) ; a derivation record in Opt (D) ; user _ address ∈ Opt (Str) ; proprietary ∈ P . The Sapling constructions are those of the protocol specification and are cited, not restated. - Orchard bundle.
-
actions ∈ List (OA) ; flags ∈ u8 , with bit 0 enableSpends , bit 1 enableOutputs , bit 2 enableCrossAddress (v2; zero in version 1 and in the Orchard bundle of every transaction mined under NU6.3 or later, the rule of Construction 11.5), and bits 3 to 7 zero; value _ sum ∈ u64 × bool ; anchor ∈ B 32 (v1) or Opt (B 32) (v2); note _ version ∈ Enum { V2, V3 } (v2), where V2 is the note plaintext of ZIP 212, lead byte 0x02, and V3 that of ZIP 2005, lead byte 0x03, which MUST be V2 in the Orchard bundle and is implicitly V2 in version 1 ; zkproof ∈ Opt (List (u8)) , one proof for the bundle; bsk ∈ Opt (B 32) . An Action OA : cv net ∈ B 32 ; a spend OS ; an output OO ; rcv ∈ Opt (B 32) , one per Action, since an Action has one net value commitment (Ironwood Guide, §“Value commitments”). A spend OS : effecting nf, rk ∈ B 32 ; spend _ auth _ sig ∈ Opt (B 64) ; recipient ∈ Opt (B 43) , a raw Orchard address; value ∈ Opt (u64) ; ρ, rseed ∈ Opt (B 32) ; fvk ∈ Opt (B 96) , the encoding of (ak, nk, r ivk) ; witness ∈ Opt (u32 × (B 32) 32) , a position and a 32 -level authentication path; α ∈ Opt (B 32) ; a derivation record in Opt (D) ; dummy _ sk ∈ Opt (B 32) ; proprietary ∈ P . In a transaction of version 6 the witness may be absent until proving (§12.5). An output OO : effecting cmx, epk ∈ B 32 and C enc, C out ∈ List (u8) ; recipient ∈ Opt (B 43) ; value ∈ Opt (u64) ; rseed, ock ∈ Opt (B 32) ; a derivation record in Opt (D) ; user _ address ∈ Opt (Str) ; proprietary ∈ P . - Ironwood bundle
-
(v2). The fields of the Orchard bundle, with
note _ version = V3 and its anchor a root of the Ironwood note commitment tree (§12.5).
Which role sets, requires or clears each field is as ZIP 374 states per field; this section restates it where it defines a role.
Every transparent input’s value and script _ pubkey are required, not optional, because the signature digest commits to the value and script of every coin a transaction spends (ZIP 244, as amended by ZIP 229; Ironwood Guide, §“Transaction digests and signatures”), and the binding signatures are on that digest (ZIP 374, “TransparentInput”).
Remark 12.7 (The sign of an Orchard-protocol value sum).
The pair
A Signer MUST parse the user _ address of each output that carries one and confirm that it contains the output’s recipient, directly or as a receiver of a unified address (ZIP 374, “TransparentOutput”, “SaplingOutput” and “OrchardOutput”; Definition 3.7 and Construction 3.10). The anchors, witnesses and commitments that these fields carry are those of the Ironwood Guide, §“The note commitment tree”, with its subsections “Anchors” and “Authentication paths”; they are cited, not rebuilt.
Definition 12.8 (Canonical empty bundles).
The canonical empty bundle of each slot is (ZIP 374, “v2 Encoding”):
-
(i)
transparent: empty input and output lists;
-
(ii)
Sapling: empty spend and output lists,
value _ sum = 0 , anchor = ⊥ , bsk = ⊥ ; -
(iii)
Orchard: no Actions,
flags = 0000 0011 in binary (spends and outputs enabled), value _ sum = (0, false) , anchor = ⊥ , note _ version = V2 , zkproof = bsk = ⊥ ; -
(iv)
Ironwood: no Actions,
flags = 0000 0111 in binary (spends, outputs and cross-address transfers enabled), value _ sum = (0, false) , anchor = ⊥ , note _ version = V3 , zkproof = bsk = ⊥ .
A bundle that differs from it in any field, its flags, note version or anchor included, is not canonical empty.
12.4 Encoding
Construction 12.9 (PCZT encoding).
The encoding of a PCZT of version n is
| 50 43 5a 54 ‖ I2LEOSP 32 (n) ‖ body n, |
the first four bytes being the ASCII string PCZT. A string that does not begin with this 8 -byte header is not a PCZT encoding, and a parser that meets an unknown version MUST NOT parse the remainder (ZIP 374, “Encoding”). The body is built from the following encodings of the types of Definition 12.6 (ZIP 374, “Data type encodings”):
-
(i)
u8 : one raw byte;
-
(ii)
u32 and u64 : varint (x) , the digits of x in base 128 , least significant first, one per byte, with bit 7 set on every byte but the last. Encoders MUST emit the shortest form. A k -bit integer takes at most ⌈ k / 7 ⌉ bytes, 5 for u32 and 10 for u64 , and in an encoding of that length the last byte contributes only the high
k mod 7 bits, so the fifth byte of a u32 is at most 0x0f; decoders MUST reject encodings that exceed either bound and MAY accept non-minimal encodings within them; -
(iii)
i128 : varint (zigzag (x)) , with
zigzag (x) = 2 x for x ≥ 0 and 2 | x | − 1 for x < 0 ; -
(iv)
bool : the byte 0x00 for false or 0x01 for true , other bytes rejected;
-
(v)
B n , T n and pairs: the concatenation of the elements, with no length prefix, so that a witness path is 1024 raw bytes;
-
(vi)
Opt (T) : the byte 0x00 for ⊥ , and 0x01 followed by the value otherwise, other tag bytes rejected;
-
(vii)
List (T) and Str : the varint of the number of elements, of bytes for a string, followed by the elements; invalid UTF-8 is rejected;
-
(viii)
Map (K, V) : the varint of the number of entries, followed by each key and its value. Encoders MUST emit the entries in strictly ascending lexicographic byte order of the unencoded keys, without duplicates; decoders MAY accept other orders and duplicates;
-
(ix)
Enum : the varint of the tag’s index;
-
(x)
a record: the concatenation of its fields in the order of Definition 12.6, without tags or padding, a field absent from version n being omitted entirely.
Encoders MUST NOT emit data after the last field; decoders MAY ignore or
reject it. Layout (ZIP 374, “v1 Encoding” and “v2 Encoding”):
body 1 is the Global record followed by the transparent, Sapling
and Orchard bundles, each Action encoded as cv net , spend,
output, rcv . The body body 2 is the Global record followed by
the four bundles, transparent, Sapling, Orchard and Ironwood, each as a
value of Opt ; a bundle equal to its slot’s canonical empty bundle
(Definition 12.8) MUST be encoded as absent and any other as
present, and a parser MUST restore the canonical empty bundle from absence.
Encoding in version 1 MUST fail when
Lemma 12.10 (Canonicity of the encoding).
For every version n and every PCZT P representable in version n , exactly one byte string is an output for P permitted to an encoder that obeys the MUST rules of Construction 12.9, and distinct PCZTs have distinct encodings. Canonicity is a property of encoder output: since decoders may accept non-minimal varints, unordered or repeated map entries and trailing data, several strings may decode to one PCZT.
Proof.
By induction on the type structure. Uniqueness. The permitted encoding of each primitive is a function of its value: the shortest base- 128 representation is unique, its last byte non-zero unless the value is 0 ; the map zigzag is a bijection from the integers onto the naturals; the tags of options, booleans and enumerations are fixed; the counts of lists and strings are determined by the value. A finite map admits exactly one strictly ascending order of its entries without duplicates, since lexicographic order on byte strings is total. A record concatenates uniquely encoded fields in a fixed order. In version 2 the presence of each bundle is determined by equality with Definition 12.8, and no trailing data is permitted. Injectivity. Each encoding is self-delimiting given its type, being of fixed length or a count followed by self-delimiting elements, so a decoder that reads the fields in order recovers every value; an absent version- 2 bundle is restored as the canonical empty bundle, the only bundle encoded as absent. The header fixes n , so encodings of distinct versions differ as well. □
The canonical-empty rule is exact equality so that two copies of one PCZT encode identically whatever software produced them, and re-encoding cannot move a bundle between its present and absent forms (ZIP 374, “Omitting empty bundles in PCZT v2”).
Example 12.11 (A minimal version-2 PCZT).
The Creator’s PCZT (§12.6) for a transaction of
version 6 , with version group identifier 0xD884B698 (ZIP 229),
consensus branch identifier 0x77190AD9 (NU7, ZIP 259), expiry
height
| Offset | Bytes | Field |
|---|---|---|
| 0 | 50 43 5a 54 | header, PCZT |
| 4 | 02 00 00 00 | version 2 |
| 8 | 06 | tx _ version = 6 |
| 9 | 98 ed 92 c4 0d | version _ group _ id |
| 14 | d9 95 e4 b8 07 | consensus _ branch _ id |
| 19 | 00 | fallback _ lock _ time = ⊥ |
| 20 | 80 ad e2 04 | expiry _ height |
| 24 | 85 01 | coin _ type = 133 |
| 26 | 83 | tx _ modifiable , bits 0 , 1 , 7 |
| 27 | 00 | empty proprietary map |
| 28 to 31 | 00 00 00 00 | four absent bundles |
12.5 PCZT v2: deferred anchors and the Ironwood bundle
In version 2 the Ironwood bundle carries the Ironwood-pool component of a
transaction of version 6 , with the structure, field meaning and role
interactions of the Orchard bundle, the Ironwood pool being a second value
pool of the Orchard protocol (ZIP 229; Ironwood Guide, §“The
Orchard protocol and its two pools”). It differs in three respects: its
enableCrossAddress bit is meaningful and normally 1 ; its anchor
is a root of the Ironwood note commitment tree, distinct from the Orchard
tree; and its note version MUST be V3 . Every role MUST reject a
PCZT with
Definition 12.12 (Anchors and witnesses in version 2).
The following rules hold (ZIP 374, “Anchors and pre-authorization”).
-
(i)
For
tx _ version = 5 , every shielded bundle’s anchor is set when the bundle’s first spend is added and never changes, since the version- 5 digest commits to it. -
(ii)
For
tx _ version = 6 , which requires version 2 , an anchor MAY be absent until proving; an Updater MAY set an absent anchor, or replace a set one, at any time before the Prover runs for that bundle; setting or replacing an anchor MUST clear every proof already in that bundle, the Sapling spends’ proofs or the Orchard-protocol bundle’s proof, since a proof takes the anchor as a primary input; and the witness of a Sapling or Orchard-protocol spend MAY be absent until proving, and is set by an Updater once known. -
(iii)
Whenever a bundle has both an anchor and witnesses, the Updater that sets either MUST check that every witness of a spend of non-zero value roots to the anchor, and the Prover MUST check the same before proving.
Deferral is governed by the transaction version, not by the PCZT version: a transaction of version 5 in a version- 2 PCZT fixes its anchors as in version 1 . Absence is an absent option, not an all-zero string, because zero is an element of F p Pallas and so a syntactically valid anchor (ZIP 374, “Optional anchors in PCZT v2”).
Proposition 12.13 (Deferred anchors).
Let P be a PCZT of a transaction of version 6 .
-
(i)
If every spend of P is signed, replacing the anchor rt of a bundle and its proof π by any anchor rt ′ and a proof π ′ valid for it leaves every signature valid and the transaction identifier unchanged: re-anchoring needs only re-proving.
-
(ii)
A spend of an Orchard-protocol note whose creating transaction is not yet mined can be fully signed before that note is in the tree, and its signatures remain valid once an anchor, a witness and a proof are supplied: every field that the signature digest commits to is computable from the note data, and the anchor is not among them.
Neither holds for a transaction of version 5 , and (ii) fails for a Sapling spend in version 6 .
Proof.
(i) The version- 6 digest and transaction identifier omit the anchors, which are authorising data (ZIP 229, “Anchor commitment (version 6)”), and by Ironwood Guide, §“Transaction digests and signatures”, Proposition “Bundle binding”, replacing (rt, π) by (rt ′, π ′) changes neither the transaction identifier nor any signed message, so every signature remains valid.
(ii) The effecting fields of an Orchard-protocol spend are nf , rk and its Action’s cv net . The nullifier is DeriveNullifier nk (ρ, ψ, cm) (Ironwood Guide, §“The nullifier”), a function of the key and of note data, with ρ fixed by the creating Action and ψ and cm derived from rseed , ρ , the address and the value; it does not depend on the note’s position. The key rk and the commitment cv net depend on keys, values and fresh randomness only.
For version 5 the digest commits to the anchors (ZIP 244, “Signature Digest”), so replacing an anchor invalidates every signature, which refutes (i); and an anchor fixed before the note is in the tree is the root of a tree state that does not contain the note, for which no authentication path of the note exists except with negligible probability (Ironwood Guide, §“Anchors”, Proposition “Membership soundness”), so a spend of non-zero value signed then admits no valid proof, so no signature made before the note is in the tree survives completion, which refutes (ii). A Sapling nullifier depends on the note’s position in the tree (protocol specification, §“Computing ρ values and Nullifiers”), which is unknown until the note is mined, and is effecting data; for Sapling only (i) holds. □
12.6 Construction and IO finalisation
The transaction of a PCZT is of version 5 , with version group identifier 0x26A7270A (protocol specification, §“Transaction Consensus Rules”), or of version 6 , with 0xD884B698 (ZIP 229), whose consensus branch identifier names NU6.3 or a later upgrade; version 4 is not representable, and is invalid from NU7 on (ZIP 2003, deployed by ZIP 259). An Ironwood component requires version 6 , the mixed case being rejected by the rule of §12.5. The consensus branch identifier fixes the rules in force, and a role that does not recognise it cannot check the PCZT against them (ZIP 374, “Global”).
Creator. The Creator chooses tx _ version ,
version _ group _ id and consensus _ branch _ id , sets the
other Global fields with
Constructor. Before adding anything the Constructor MUST check the
bit of tx _ modifiable for the kind added
(Definition 12.5), and it updates the bundle’s
value _ sum . Per Orchard-protocol Action, in the notation of the
Ironwood Guide, it sets
Construction 12.14 (IO finalisation).
Once the input and output set is final, the IO Finalizer performs the following steps, failing where stated (ZIP 374, “IO Finalizer”).
-
(1)
If shielded spends or outputs exist, it clears bits 0 , 1 and 7 of tx _ modifiable .
-
(2)
For each Orchard-protocol bundle with Actions
1, ..., n , it requires every rcv i , sets bsk := ∑ i rcv i ∈ F p Vesta , computes bvk := ∑ i cv i net − [v balance] V Orchard, with v balance the integer that the bundle’s value _ sum denotes (§12.3), and fails unless
[bsk] R Orchard = bvk (Ironwood Guide, §“The binding signature”). The Orchard and the Ironwood bundles are finalised separately, each by this computation on its own Actions. -
(3)
For the Sapling bundle, it sets bsk to the sum of the spends’ rcv minus the sum of the outputs’ rcv , checked in the same way against the Sapling binding validating key (protocol specification, §“Balance and Binding Signature (Sapling)”).
-
(4)
It computes the signature digest over the effecting data (Ironwood Guide, §“Transaction digests and signatures”), signs each dummy spend under the spend authorising key derived from its dummy _ sk or given by its dummy _ ask , randomised by the spend’s α , and clears that key.
-
(5)
For each bundle with
enableCrossAddress = 0 , it MUST verify that each Action’s output recipient equals its spend recipient, and fail otherwise.
Equality of the raw recipients in step (5) implies condition A10 of the Action statement, equality of the expanded receivers (g d, pk d) (Ironwood Guide, §“The Action statement”), and is stricter only for two diversifiers with one diversified base. An Action that violates A10, for which no valid proof exists, therefore fails the step, which reports the violation at the role responsible for it. ZIP 374 keys the step on the value of the bit alone, but before NU6.3 activation bit 2 of the Orchard bundle’s flags is reserved as 0 while cross-address transfers are unrestricted (ZIP 229, Rationale, “enableCrossAddress polarity”); read literally, the step then rejects an Orchard bundle that pays another address, a gap in the specification. This volume applies the step only where bit 2 carries the meaning of enableCrossAddress , and compares expanded receivers as A10 does; both readings are designed but unspecified (Definition 1.1).
Lemma 12.15 (Value-sum consistency).
Let an Orchard-protocol bundle have Actions with
Proof.
With
| bvk − [bsk] R Orchard = [∑ i v i net − v balance] V Orchard, |
which is O if and only if the coefficient vanishes modulo p Vesta , since V Orchard is a non-identity point of the group of prime order p Vesta . This is Ironwood Guide, §“The binding signature”, Proposition “Balance and key knowledge”, part (i). No independence of V Orchard and R Orchard is used. The check computes bvk from the commitments and value _ sum alone. □
The binding signing key cannot wait for the Transaction Extractor, since every rcv would then travel to it and open every value commitment to every intermediate party; nor can Constructors maintain it incrementally, since serial Constructors would have to update it and parallel ones, whose results a Combiner merges, must not. One role run once the set is final removes both problems, and the same role signs dummy spends so that no Signer parses spending-key material (ZIP 374, “Adding an IO Finalizer role”).
12.7 Signing
Digests. The Signer derives the effecting data from the PCZT and computes the shielded signature digest SigHash itself (ZIP 244 for version 5 , as amended by ZIP 229 for version 6 ; Ironwood Guide, §“Transaction digests and signatures”), neither proofs nor signatures entering it; for each transparent input it signs, it computes that input’s digest under the input’s sighash _ type (ZIP 244, “S.2: transparent_sig_digest”) and signs it by the scheme of the Crypto Guide, §“The transparent layer’s schemes: ECDSA and BIP-340 over secp256k1”. A Signer that cannot sign under an input’s hash type MUST NOT sign that input (ZIP 374, “TransparentInput”).
Orchard-protocol spends. For an Action it signs, with α
present, the Signer sets
Definition 12.16 (Signer relations).
For an Orchard-protocol Action whose explicit data are present, with v old and v new the values of its spend and its output, the Signer relations are, in the notation of the Ironwood Guide:
-
(a)
cv net = ValueCommit rcv Orchard (v old − v new) (§“Value commitments”); -
(b)
the consumed note rebuilt from ( recipient , v old , ρ , rseed ) has nullifier nf under the nk of fvk (§“The nullifier”), and fvk owns the recipient:
pk d = [ivk] g d for the ivk that fvk determines (§“Diversified addresses”); -
(c)
rk = ak P + [α] G SpendAuth for the ak of fvk (§“Randomised validating keys”); -
(d)
cmx is the commitment of the created note rebuilt from ( recipient , v new , rseed ) with
ρ new = nf (§“Note commitments”); -
(e)
for an output that is not fabricated, esk derived from rseed and ρ new gives epk and a C enc that decrypts to a plaintext with the explicit recipient, value and rseed (§“Encryption to the recipient”), and, when ock is present, C out decrypts under it to (pk d, esk) (§“The outgoing ciphertext”).
A fabricated zero-valued output at a spent note’s receiver carries a random C enc (Construction 11.18) and is exempt from (e): a Signer MUST NOT reject it on that ground alone, and SHOULD classify it as a tolerable dummy, checking (d) if it wishes (ZIP 374, “Signer”, “Verifier” and “Fabricated same-address outputs (NU6.3)”).
Obligations before signing (ZIP 374, “Signer”). A Signer MUST reject a PCZT that carries any dummy _ sk or dummy _ ask : the IO Finalizer signs dummy spends and clears these keys, so their presence asks the Signer to parse spending-key material. It MUST, for each output with a user _ address , parse it and confirm that it contains the output’s recipient (§12.3). It SHOULD verify that the explicit values and note data it shows its user are consistent with the effecting data it signs, through the relations of Definition 12.16; a field absent because it was redacted is not an inconsistency, and only a present field that contradicts the effecting data is. The relations need the value and note commitments, BLAKE2b and the functions built on it, nullifier derivation, key agreement, the key derivation and the AEAD of note encryption, the signature digest and RedPallas signing (RedJubjub for Sapling), and no proof system.
Theorem 12.17 (Signer safety).
Let a Signer hold the ask of an Orchard-protocol key generated with
-
(i)
every accepted Action that consumes a note of the key carries a signature on some m P ;
-
(ii)
every accepted transaction that carries an Action with a randomised validating key rk under which the Signer signed has the effecting data T Q of some PCZT Q that the Signer signed with an Action of key rk ; in it the Actions whose spends the Signer signed consume and create the notes, with the values and recipients, that the Signer displayed for Q , and every other effecting field, balancing values and transparent data included, equals that of Q .
The theorem concerns content, not inclusion.
Proof.
(i) The Signer is the signing oracle of the Ironwood Guide, §“Authorisation of spends”, Definition “Spend-authority experiment”, queried with (α, m P) for α taken from the PCZT and so possibly chosen by an adversary, which that experiment admits; the full viewing key that the PCZT discloses is given to the adversary there. Theorem “Spend authority” bounds by a negligible function the probability of an accepted Action that consumes a note of the key without a queried digest.
(ii) Let T ′ be accepted and carry an Action with key rk and a
signature σ ′ valid under rk on SigHash (T ′) . The
reduction of the proof of Theorem “Spend authority”, which simulates the
key holder from ak P and answers queries with adversarial
randomisers, turns a triple (rk, SigHash (T ′), σ ′) that is
not a triple of an answer of the Signer into a forgery in Ironwood Guide,
§“RedPallas unforgeability”, Proposition “Unforgeability under
re-randomisation”; hence,
except with negligible probability,
Pre-authorisation (ZIP 374, “Signer” and “Anchors and pre-authorization”). For a transaction of version 6 a Signer MAY sign while the shielded anchors, witnesses or proofs are absent, since signatures commit to none of them (Proposition 12.13). A Signer asked to do so SHOULD be aware, and where applicable make its user aware, that a spend without a witness may be of a note that never exists on chain: the signature authorises the spend whether or not the note is created. For a transaction of version 5 the anchors are in the digest and MUST be present before signing.
Lemma 12.18 (Binding key after IO finalisation).
If IO finalisation (Construction 12.14) succeeded for an Orchard-protocol bundle, and its commitments cv i net and its value _ sum are unchanged afterwards, then a binding signature under bsk on the signature digest is valid under the bvk that validation derives from the transaction’s cv i net and balancing value v balance .
Proof.
Validation computes bvk from the same commitments and balancing value (Ironwood Guide, §“The binding signature”, Definition “Binding validating key”), and IO finalisation checked that it equals [bsk] R Orchard (Lemma 12.15). Correctness of RedPallas in the binding-signature instance (Ironwood Guide, §“The binding signature”, Construction “Binding signature”) gives validity. □
12.8 Proving
Per Orchard-protocol Action the Prover requires the spend’s recipient, value, ρ , rseed , fvk , witness and α , the output’s recipient, value and rseed , and the Action’s rcv ; the bundle’s anchor MUST be set, and before proving the Prover MUST verify that the path of the witness of every spend of non-zero value roots to it, and fail otherwise. For Sapling it requires per spend the recipient, the value, rcm or rseed , rcv , the proof generation key and the witness, and per output the recipient, the value, rseed and rcv . The Prover needs no spending key; a delegated Prover learns the note data of the bundle but gains no spending authority (§12.9) (ZIP 374, “Prover”).
Construction 12.19 (Proof creation from a PCZT).
For an Orchard-protocol bundle with no Actions the Prover does nothing.
Otherwise, for each Action i , it rebuilds the consumed note from its
explicit data and the created note from its explicit data with
| (rt, cv i net, nf i, rk i, cmx i, enableSpends, enableOutputs, disableCrossAddress) |
with rt the bundle’s anchor, and the auxiliary input from the witness, the two notes, α i , the components of fvk i and rcv i (Ironwood Guide, §“The Action statement”); and fails if the pair does not satisfy the Action statement, in particular if fvk i does not own the consumed note or cmx i differs from the commitment of the rebuilt created note. It then creates one Halo 2 proof for all Actions of the bundle (Ironwood Guide, §“The Action circuit and the Halo 2 proof”; Halo 2 Guide, §“The Halo 2 proof system”) and sets zkproof . The Ironwood bundle is proved in the same way with its own anchor. The primary input consists of effecting data and the anchor only.
An Action whose rk is the identity point O is invalid (protocol specification, §“Action Descriptions”; ZIP 256, “Orchard identity rk”), and the Transaction Extractor MUST refuse it (ZIP 374, “Transaction Extractor”). A Prover that refuses it as well spares a proof of a transaction that cannot be valid; ZIP 374 does not state that check for the Prover, and it is designed but unspecified (Definition 1.1).
12.9 Combining, redaction, and privacy
Construction 12.20 (Binary merge).
The merge
-
(1)
Global. The fields tx _ version , version _ group _ id , consensus _ branch _ id , fallback _ lock _ time , expiry _ height and coin _ type MUST be equal. The field tx _ modifiable merges bitwise, bits 0 , 1 and 7 by AND and bit 2 by OR, bits 3 to 6 being required zero on both sides.
-
(2)
Lists of inputs, outputs, spends and Actions. If either side’s bundle is IO-finalised, its bsk being present, both sides have equally many entries and equal value _ sum . Otherwise the entries at the positions common to both lists merge pairwise, and the extra entries of the longer list are appended provided the shorter side’s tx _ modifiable permits additions of that kind, the merge failing otherwise. The merged shielded bundle’s value _ sum is that of the side each of whose lists of the bundle is at least as long as the other side’s, the merge failing if neither side is; with lists of equal lengths the two MUST be equal. ZIP 374 leaves this unstated, so it is designed but unspecified (Definition 1.1).
-
(3)
Required fields of merged entries, and the bundle flags , note _ version and, in version 1 , anchor , MUST be equal.
-
(4)
Optional fields merge as
x ⊔ ⊥ = ⊥ ⊔ x = x , and x ⊔ y = x if x = y , failing otherwise; in version 2 this rule covers the anchors. -
(5)
Maps merge by union of their keys, the values of a common key being required equal.
The Combiner of k PCZTs merges them into one that contains every field of each, or fails. It MUST NOT combine PCZTs that do not represent the same transaction, that is, PCZTs not derived by roles from a common ancestor, which rules (1) to (3) check structurally. Once the input and output set is final, the effecting data determine the transaction identifier, which then identifies the PCZT; for version 6 , re-anchored copies keep that identifier.
BIP 174 lets a combiner keep one of two conflicting values and discard the other. The PCZT merge requires equality instead, which is always possible because every field is typed and known in advance, so every conflict fails at the Combiner and none diverges later (ZIP 374, “Combiner rejecting non-identical duplicates”).
Lemma 12.21 (Commutativity of the merge).
For PCZTs P and Q , the merge
Proof.
By cases on the rules of Construction 12.20. The equality tests of rules (1) and (3) are symmetric; AND and OR are commutative; the rule for optional fields and the union of maps with equal values on common keys are symmetric; the condition on IO-finalised bundles is symmetric; in rule (2) the longer list and the side whose permission is consulted are determined by the lengths, not by the order of the arguments, and so is the merged value _ sum , which is required equal at equal lengths; and the pairwise merges of common entries commute by induction on the structure of the entries. □
ZIP 374 requires further that combining SHOULD be functionally
order-independent,
Proposition 12.22 (Order independence of proving and signing).
Let p be an IO-finalised PCZT on which the Prover
(Construction 12.19) and a Signer (§12.7)
are both defined, the anchors being set for proving and, for a transaction
of version 5 , fixed before signing (Definition 12.12). Fix the
random coins of both roles. Then Prove (Sign (p)) and
Sign (Prove (p)) are defined and both equal
Proof.
Signing. The signed digest is computed from effecting data only,
excluding proofs and signatures (Lemma 11.21), and the
relations of Definition 12.16 read effecting and
context data; Prove writes neither, so Sign reads the
same values on p and on Prove (p) and, with its coins fixed,
writes the same signatures and bits. Proving. The primary input of
the Action statement consists of effecting data and the anchor, and the
auxiliary input of context data (Construction 12.19;
Ironwood Guide, §“The Action statement”); Sign writes
none of them, and the Prover reads no spending key, so Prove
writes the same proofs on p and on Sign (p) . Merge. The
role Prove sets only proof fields, absent in p , and
Sign only signatures, absent in p , and bits of
tx _ modifiable , which it only clears, or sets in the case of
bit 2 ; the bundle of p is finalised on both sides with equal counts and
value sums. Neither role writes a required field, so rule (3) holds, and a
transparent signature is a new key of partial _ signatures ,
merged by rule (5). Rules (1) to (5) of Construction 12.20
therefore give
Redactor (ZIP 374, “Redactor” and the field descriptions). Anyone may clear fields that later roles do not need: per Orchard-protocol Action the spend’s spend _ auth _ sig , recipient, value, ρ , rseed , fvk , witness, α , derivation record, dummy key and proprietary entries, the output’s recipient, value, rseed , ock , derivation record, user _ address and proprietary entries, and rcv ; the corresponding Sapling fields; and the transparent and Global lookup data. A PCZT with inputs of several independent Signers is sent to each with only what that Signer needs, for example without the other Signers’ values of α .
Proposition 12.23 (Disclosure by a PCZT).
A PCZT carries strictly more than its transaction: for each shielded spend or output it may carry the counterparty address, the value, the note randomness, rcv , which opens cv net , the full viewing key of the spending account, derivation records, ock , which opens C out , and address strings. Every recipient of a PCZT at a stage learns all data present at that stage; a delegated Prover learns the note data of the spends and outputs but gains no spending authority; the extracted transaction contains none of these data. Participants SHOULD send a PCZT only to entities needed for the remaining roles and SHOULD redact what those do not need, and wallets SHOULD protect stored PCZTs as they protect their note records (ZIP 374, “Privacy Implications”).
Proof.
The listed fields are context data (Definition 12.3), which
extraction omits (§12.10); a recipient reads every field
present. The Prover’s data (Construction 12.19) contain
fvk but no ask , and an accepted spend of a note of the key without a
signature under
12.10 Spend finalisation and extraction
Spend Finalizer (ZIP 374, “Spend Finalizer” and “TransparentInput”; BIP 11; BIP 16). For each transparent input with enough data, the Spend Finalizer builds script _ sig : for P2PKH, the push of the one signature, with its hash-type byte, under the key that hashes to the address, followed by the push of that key; for P2SH multisignature, the opcode OP _ 0 , the pushes of m signatures in the key order of the redeem script and the push of the redeem script, failing with fewer than m signatures. It MUST fail on a signature whose hash type is not the input’s sighash _ type . It SHOULD then clear the input’s redeem script, partial signatures, derivation records and preimages. It keeps value and script _ pubkey , required fields that the digest needs, and sequence and the lock-time requirements, which the digest and Definition 12.24 read at extraction; ZIP 374’s “all other optional data” would include these last fields, a gap in the specification.
Definition 12.24 (Lock-time determination).
If no transparent input has a required time or height lock, the lock time is fallback _ lock _ time , or 0 if it is absent. Otherwise the lock type is one supported by every input that states a requirement, an input that states both types supporting both; an input that states neither supports both. If both types remain possible, the height type is chosen; if none remains, the requirements are unsatisfiable. The lock time is the maximum required value of the chosen type (ZIP 374, “Determining Lock Time”).
Construction 12.25 (Transaction extraction).
The Transaction Extractor checks, failing on any violation (ZIP 374, “Transaction Extractor”), that
-
(i)
tx _ version , version _ group _ id and consensus _ branch _ id name a supported format, and the lock-time requirements are satisfiable (Definition 12.24);
-
(ii)
for
tx _ version = 5 the Ironwood bundle is canonical empty; -
(iii)
every script _ sig is set;
-
(iv)
every Sapling spend has its proof and signature, and every Sapling output its proof;
-
(v)
every Orchard-protocol bundle with
n ≥ 1 Actions has a zkproof of the canonical length of 2720 + 2272 n bytes (Ironwood Guide, §“The transaction format”), and every Action a spend _ auth _ sig ; -
(vi)
every non-empty shielded bundle has its anchor and bsk ;
-
(vii)
no rk is O .
It then sets each bundle’s balancing value to v balance , failing if it lies outside the signed 64 -bit range of the transaction field; sets the lock time by Definition 12.24; computes SigHash ; for each bundle derives bvk from its value commitments and balancing value, fails unless it matches bsk , and signs SigHash under bsk , by RedPallas for the Orchard and Ironwood bundles and by RedJubjub for Sapling (Lemma 12.18); and outputs the transaction, without any context data (ZIP 229). It SHOULD then verify every proof and signature of that transaction, each spend _ auth _ sig under its rk on SigHash included, so that an invalid transaction is found before submission.
A party that holds an Orchard-protocol output’s recipient, value and rseed , with ρ new the nf of its Action’s spend, recovers the full note plaintext, memo included, without ock or any viewing key, by the derivation of esk stated with Theorem 11.22 (§11.8; Ironwood Guide, §“Encryption to the recipient”, Proposition “Decryption correctness”; ZIP 212). The random C enc of a fabricated output decrypts to nothing, as the construction intends.