10 Merkle trees and commitments to sets
This final section constructs, from the collision-resistant hash of §3 alone, the Merkle tree: a short commitment to a list of values with membership proofs of logarithmic size. It proves, by reduction to collision resistance, that the root is binding—no party can publish one root and later open it to two different lists (equivocation)—and that membership proofs are sound—no party can prove membership of a value absent from the committed list, which in a payment system would spend a note the ledger never recorded (Proposition 10.5, Theorems 10.12 and 10.25). It constructs the append-only tree of a shielded pool, updated in logarithmic time (Proposition 10.20), and makes membership private by hiding the path from leaf to root in a zero-knowledge argument of §9: an observer of an honest proof learns nothing about which member it concerns, information that would trace every coin (Theorem 10.29). The commitments of §4 are the leaves, and the algebraic hashes of §3 and §4 compute the internal nodes; the section ends with an Orchard shielded spend assembled end to end.
10.1 Two statements about a set
A prover holds a large collection of values—transactions in a block, public keys in a directory; in this volume, the growing set of note commitments of a shielded payment system. A verifier must be convinced of two statements about it without storing it or seeing most of it.
-
•
Membership. “Value v occurs at position i of the list”—or, forgetting the position, “ v belongs to the set.”
-
•
Integrity. “The collection is exactly the one committed to earlier, unaltered.”
Both are served by a single short commitment that determines the whole collection and short membership proofs, where “short” means of size independent of the number of elements, or at most logarithmic in it: integrity becomes one comparison, and membership a small certificate sent with the value. The Merkle tree, due to Ralph Merkle, achieves this from a collision-resistant hash function alone. It is the membership mechanism of Orchard: every shielded spend proves, against a published root, that some note commitment lies in the tree.
Notation follows §3.1: { 0, 1 } ∗ is the set of finite binary strings, { 0, 1 } n the strings of length exactly n , x ∥ y concatenation, and λ the security parameter. All algorithms are PPT in λ , and negl (λ) denotes a negligible function (Math Guide, §“Polynomial, exponential, and negligible functions”).
10.2 The compression function and collision resistance
The tree uses a single primitive, recalled in the keyed form in which its security is a meaningful asymptotic statement.
Definition 10.1 (Compression function).
Let
| h s : { 0, 1 } 2 l ⟶ { 0, 1 } l, |
taking two digests to one.
The key s models the choice of a concrete function from a family. For a single fixed function a colliding pair exists and some small program outputs it (the hardcoded-collision triviality discussed in §3.1), so only the keyed formulation admits a non-trivial quantification over adversaries. Deployments use a fixed standardised function or, inside arithmetic circuits, an algebraic hash in the sense of §3.8 and §4.8; we suppress s and write h and H .
The tree needs collision resistance (Definition 3.7,
§3.2): given the key s , every PPT adversary
outputs
10.3 Binary Merkle trees
Definition 10.2 (Binary Merkle tree).
Fix a two-to-one compression function
| N 0, j = L j (0 ≤ j < 2 d), N t + 1, j = h (N t, 2 j ∥ N t, 2 j + 1) (0 ≤ t < d, 0 ≤ j < 2 d − t − 1) . | (3) |
Level t has 2 d − t nodes, and N t, j is the j -th
node from the left at level t . The unique level- d node is the
root:
Example 10.3 (A depth-two tree).
With
| N 1, 0 = h (L 0 ∥ L 1), N 1, 1 = h (L 2 ∥ L 3), |
and the root
| root (L) = N 2, 0 = h (h (L 0 ∥ L 1) ∥ h (L 2 ∥ L 3)) . |
The single l -bit root depends on the whole list of four l -bit strings.
A list whose length m is not a power of two is handled by fixing
the depth d with
That the root commits to the list is a security property, stated as a game in the style of Definition 1.15.
Definition 10.4 (Merkle commitment; binding).
The Merkle commitment to a list L of 2 d leaves is
-
1.
The challenger samples
s ← $ K , fixing the compression function h := H s , and sends s to the adversary. -
2.
The adversary outputs two lists
L, L ′ , each of 2 d leaves in { 0, 1 } l . -
3.
The game outputs 1 iff
L ≠ L ′ and root (L) = root (L ′) .
The commitment is binding if every PPT adversary wins with probability negl (λ) .
Proposition 10.5 (Binding of the root).
If h is collision resistant, the Merkle commitment is binding.
Concretely, there is a deterministic procedure that, from any two
distinct equal-length lists
Proof.
Build both trees. The lists differ at some leaf index j 0 , so
| N 0, j 0, N 1, ⌊ j 0 / 2 ⌋, N 2, ⌊ j 0 / 4 ⌋, ..., N d, 0 |
in both trees. The labels differ at level 0 and agree at level
d —the common root—so there is a smallest level t at
which they first agree: with
| N t, j = N t, j ′, yet N t − 1, 2 j ≠ N t − 1, 2 j ′ or N t − 1, 2 j + 1 ≠ N t − 1, 2 j + 1 ′, |
since one of the two children at level
| h (N t − 1, 2 j ∥ N t − 1, 2 j + 1) = N t, j = N t, j ′ = h (N t − 1, 2 j ′ ∥ N t − 1, 2 j + 1 ′), |
while the two 2 l -bit inputs differ in at least one half: a collision for h , located after at most d comparisons along one path. The reduction built on this extractor runs the BIND adversary once and extracts whenever it wins, so collision resistance forces the winning probability to be negligible. □
10.4 Authentication paths and membership proofs
Membership needs a certificate relating one leaf to the root: the siblings along the leaf’s path, which are exactly the data needed to recompute the root from the leaf.
Definition 10.6 (Authentication path).
Let a depth- d tree over L be given, and let i be a leaf
index,
| π i = ((s 0, b 0), (s 1, b 1), ..., (s d − 1, b d − 1)), |
where s t is the label of the sibling of the level- t
node on the path. Explicitly, with
| s t = { N t, j t + 1 if b t = 0 (sibling on the right), N t, j t − 1 if b t = 1 (sibling on the left) . |
The path has exactly d entries.
Definition 10.7 (Path verification).
The verifier Verify (rt, i, v, π i) , on a root
rt , an index i , a claimed leaf value
| a t + 1 := { h (a t ∥ s t) if b t = 0, h (s t ∥ a t) if b t = 1 . | (4) |
Accept iff
Proposition 10.8 (Completeness).
For every list L , every index i , and π i the genuine authentication path for i in the tree over L ,
| Verify (root (L), i, L i, π i) = accept . |
Proof.
The index-consistency check passes by construction, the genuine path
carrying exactly the bits of i . We show by induction on t
that
Proposition 10.9 (Logarithmic proof size).
An authentication path in a depth- d tree consists of d
sibling labels and d direction bits,
Proof.
One sibling label, one direction bit, and one compression per level, over the d levels above the leaves. □
For a set of a billion elements,
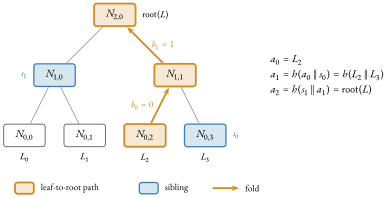
Example 10.10 (A depth-two membership proof).
Continue Example 10.3, and prove membership of
L 2 at index
| π 2 = ((L 3, 0), (h (L 0 ∥ L 1), 1)) . |
Verification folds upward:
| a 1 = h (L 2 ∥ L 3), then a 2 = h (h (L 0 ∥ L 1) ∥ a 1) = root (L), |
and the verifier accepts. The verifier never receives L 0 or L 1 , only their digest h (L 0 ∥ L 1) , and is nevertheless convinced that L 2 occupies index 2 of the committed list. Figure 16 draws this path.
10.5 Soundness: forging a path implies a collision
Soundness states that, against an honest root, a path for a value other than the genuine leaf verifies only with negligible probability.
Definition 10.11 (Path forgery).
Fix a list L of 2 d leaves with root
-
1.
The challenger samples
s ← $ K to fix h := H s , builds the tree over L , and sends s together with L —equivalently, the whole tree—to the adversary. -
2.
The adversary outputs an index i and a pair (v ∗, π ∗) .
-
3.
The game outputs 1 iff
Verify (rt, i, v ∗, π ∗) = accept and v ∗ ≠ L i .
A winning output is a path forgery at index i : the verifier accepts, against the honestly computed root, a leaf value different from the genuine one at position i .
Theorem 10.12 (Soundness of Merkle membership proofs).
Let h be collision resistant. Then no PPT adversary, given the
list L and the whole tree, produces a path forgery except with
probability negl (λ) . In constructive form: there is a
deterministic extractor that from any list L , index i , and
accepting forgery (v ∗, π ∗) with
Proof.
Run the verifier’s fold (4) on
(i, v ∗, π ∗) , obtaining the chain
The two chains disagree at the bottom,
| t ∗ := min { t : a t ∗ = a t } ∈ { 1, ..., d } |
exists, and
| X ∗ = { a t ∗ − 1 ∗ ∥ s t ∗ − 1 ∗ if b t ∗ − 1 = 0, s t ∗ − 1 ∗ ∥ a t ∗ − 1 ∗ if b t ∗ − 1 = 1, X = { a t ∗ − 1 ∥ s t ∗ − 1 if b t ∗ − 1 = 0, s t ∗ − 1 ∥ a t ∗ − 1 if b t ∗ − 1 = 1, |
where s t ∗ − 1 ∗ is the sibling claimed in π ∗ and s t ∗ − 1 the genuine sibling. Then
| h (X ∗) = a t ∗ ∗ = a t ∗ = h (X), X ∗ ≠ X, |
the inequality because the two preimages differ in the half occupied
by the running value. The pair (X ∗, X) is a collision for
h , found deterministically in O (d) work once the genuine
chain is at hand—a read-off from the built tree, or
If a PPT adversary A produces path forgeries with
probability ε (λ) , the collision finder
B that receives the key, samples or receives L , runs
A , and applies the extractor outputs a collision whenever
A succeeds—hence with probability
ε (λ) , at an overhead of building the tree over
L , which B does in any case to play the challenger,
plus one verifier run and O (d) comparisons. Collision resistance
of h therefore forces
Remark 10.13 (Scope: a fixed honest root).
Theorem 10.12 is a statement about a fixed honest root: relative to a root that genuinely is root (L) , the only leaf value admitting an accepting path at position i is L i , up to a collision in h . It does not prevent an adversary free to choose the root from committing to a maliciously crafted tree; binding (Proposition 10.5) rules that out. With an untrusted party supplying the root, both properties are necessary: binding ensures the root determines at most one list, and path soundness ensures openings are faithful to it. The vector-commitment theorem of §10.8 establishes both by a single argument.
10.6 Layer and domain separation
The soundness theorem does not cover the following structural
confusion. Suppose the leaves are arbitrary-length data, hashed into
{ 0, 1 } l by the same function used internally. Then an
internal label h (A ∥ B) is itself a well-formed leaf value—it
has the right length. An adversary presents the internal node
The remedy applies the domain-separation discipline of §3.5 within a single structure.
Definition 10.14 (Layer and domain separation).
A Merkle construction has domain separation if the function applied at distinct structural positions is forced to differ, by prepending a position-dependent tag to every hash input. Concretely, from a variable-input-length hash H define
| LeafHash (v) := H (0x00 ∥ v), NodeHash t (A, B) := H (0x01 ‖ ⟨ t ⟩ ‖ A ∥ B), |
where the byte tags 0x00 and 0x01 distinguish the layer kind—leaf versus internal node—and ⟨ t ⟩ is a fixed-length encoding of the level index, distinguishing internal nodes by depth. The tree recurrence becomes
| N 0, j = LeafHash (L j), N t + 1, j = NodeHash t + 1 (N t, 2 j, N t, 2 j + 1), |
and the verifier’s fold applies the same tagged functions at the same positions.
Proposition 10.15 (Separation forces within-domain collisions).
With the tagging of Definition 10.14, any collision extracted by the binding proof (Proposition 10.5) or the soundness proof (Theorem 10.12) is a collision for H between two inputs sharing the same leading tag: a leaf preimage against a leaf preimage, or a level- t node preimage against a level- t node preimage. In particular, no accepting forgery can substitute an internal node for a leaf, or a node at one level for a node at another, without exhibiting a within-domain collision of H —which collision resistance forbids.
Proof sketch.
The extractors of both proofs locate the smallest level at which two
disagreeing computations agree, and collide the two preimages of the
compression call at that position. Under the tagged recurrence, the
verifier’s recomputation applies the position’s prescribed function
exactly as the honest tree does: at the leaves both preimages pass
through LeafHash , at level
Remark 10.16 (Unbalanced trees, padding, and a deployed failure).
The handling of lists whose length is not a power of two has failed in deployment. Bitcoin’s transaction Merkle tree handles an odd level by duplicating its last node before hashing pairwise, and the duplication rule is not injective: a list of transactions and the same list with its tail duplicated can yield the same root. This is CVE-2012-2459, a consensus-splitting vulnerability—an attacker could present two different transaction lists sharing a root, one valid and one invalid, and nodes could be made to cache the invalid one as permanently rejected (documented in Zebra: the zebra-chain crate reproduces the upstream warning that the flawed algorithm must not be reused, and the deployed defence in zebra-consensus rejects any block whose transaction hashes are not unique). The failure yields three general rules. First, layer-separate leaves from internal nodes, as Definition 10.14 prescribes. Second, make every padding or duplication rule injective on admissible lists—for instance by binding the true leaf count into the root’s computation. Third, feed NodeHash only fixed-length inputs, so that no length-extension structure of the underlying hash (§3.5) can intervene between layers.
Remark 10.17 (Algebraic hashes in the tree; Orchard’s MerkleCRH ).
When the Merkle path is verified inside a zero-knowledge circuit
(§10.9), arithmetic gates over F p evaluate the
compression function, and the choice of h dominates the cost. A
bit-oriented hash such as SHA-256 costs tens of thousands of
constraints per call; one therefore uses an algebraic hash
with compression
Orchard’s Merkle hash MerkleCRH retains the tag
mechanism of Definition 10.14 in encoded form. Each
internal call prepends to the two 255 -bit child encodings the
10 -bit little-endian encoding of
10.7 Append-only and incrementally updatable trees
The set of note commitments of a shielded pool only grows, one leaf at a time. Rebuilding a depth- 32 tree on every insertion would cost 2 32 hashes; the frontier defined below permits the update in d hashes and O (d) state.
Definition 10.18 (Append-only Merkle tree).
Fix a maximum depth d , giving capacity 2 d , and the
level-indexed NodeHash functions of
Definition 10.14. Leaf values here enter as
level- 0 labels directly, with no LeafHash : the
leaves are already digests, and the fixed depth together with the
level tags (Remark 10.17) carries the layer
separation—the convention of deployed Orchard, whose leaf is the
extracted coordinate itself (Example 10.31). An
append-only (or incremental) Merkle tree
maintains a position counter m —the number of leaves inserted so
far,
| ⊥ t + 1 := NodeHash t + 1 (⊥ t, ⊥ t), 0 ≤ t < d . |
The root after m appends, written root m , is the root of the depth- d tree, under this recurrence, whose first m level- 0 labels are the inserted values and whose remaining ones are ⊥ 0 .
Definition 10.19 (Frontier).
The frontier of an append-only tree holding m leaves is
the minimal state needed to (i) compute the current root and (ii)
update incrementally on the next Append . For each level
The binary representation of m decomposes the inserted leaves into
completed perfect subtrees of distinct heights, one of height t for
each set bit b t , and the frontier holds exactly their roots. An
append is the Merkle analogue of incrementing a binary counter: a carry
at level t combines two height- t subtrees into one of height
Proposition 10.20 (Incremental append in logarithmic time).
From the frontier of an append-only tree holding
Proof.
The algorithm is carry propagation followed by an upward fold. Set
the running label
To obtain root m + 1 , fold upward from level z with
the just-deposited f z as the running value—it is the path
label at level z , not a sibling. For
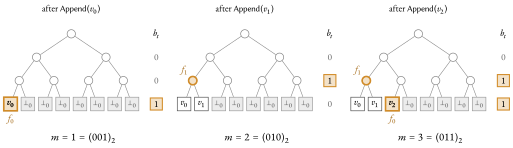
Example 10.21 (The frontier as a binary counter).
Take depth
-
•
After v 0 ,
m = 1 = (001) 2 : one completed height- 0 subtree; the frontier is { f 0 = v 0 } . -
•
After v 1 ,
m = 2 = (010) 2 : leaf v 1 at index 1 is a right child, triggering one carry c = NodeHash 1 (v 0, v 1) —a completed height- 1 subtree; the frontier is { f 1 = c } , with f 0 cleared. -
•
After v 2 ,
m = 3 = (011) 2 : leaf v 2 at index 2 is a left child and becomes a new height- 0 carry; the frontier is { f 1 = NodeHash 1 (v 0, v 1), f 0 = v 2 } —exactly the two set bits of 3 .
Each append touched only the carry chain to the new leaf, never the whole tree. (The trace involves no numeric hash values and follows mechanically from the algorithm of Proposition 10.20; the volume’s companion script replays it symbolically and checks the occupied frontier levels against the set bits of m at every step.)
Appending changes the root; the following definition fixes the root against which a proof is valid.
Definition 10.22 (History binding).
An append-only tree is history-binding when the surrounding protocol treats every historical root as an acceptable commitment in its own right: each membership proof verifies against the root it was formed for, and appending further leaves never invalidates a previously valid (root, leaf, path) triple for that root. The soundness of each individual proof is exactly Theorem 10.12 applied to the corresponding fixed root.
Deployed Orchard is history-binding by construction. The root of the
note-commitment tree at the end of each block is an anchor, and
a spend may prove membership against any historical anchor:
consensus requires the anchor named by a transaction to be the root
of the Orchard note-commitment tree as it stood at the end of some
earlier block (protocol specification
§ 3.7, ‘Action
Transfers and their Descriptions’). The deployed representation of the
growing tree, the newest leaf with its left siblings on the path to
the root, is equivalent to the frontier. When m is odd these
labels are exactly the carries of Definition 10.19.
When m is even, with lowest set bit
Remark 10.23 (Why append-only, and what it costs).
Deletion or in-place update could be supported at O (log m) per operation, given the relevant siblings; the restriction to appends is a design choice, made for monotonicity. Once a leaf is inserted it is never removed, so a membership proof valid against the root at insertion time remains valid against that historical root forever. A shielded pool requires this property: a note, once added, can be spent later by proving against some past anchor, without the spender following the current root as other parties’ insertions change it. The cost falls on the verifier, which must accept a window of historical roots rather than a single current one; in the deployed protocol that window is the set of recorded anchors.
10.8 Vector commitments
The Merkle construction instantiates the following abstraction: a commitment to an ordered vector that opens one position at a time. Its unordered counterpart, the cryptographic accumulator, certifies set membership with no notion of position; Orchard does not use it, since notes occupy positions and the position is part of the spend circuit’s witness.
Definition 10.24 (Vector commitment).
A vector commitment is a tuple of PPT algorithms (Setup, Commit, Open, Vf) :
-
•
Setup (1 λ, n) → pp produces public parameters for vectors of length n ; -
•
Commit (pp, (v 0, ..., v n − 1)) → (C, aux) outputs a short commitment and auxiliary state; -
•
Open (pp, i, aux) → π i produces a proof that position i holds v i ; -
•
Vf (pp, C, i, v, π) → { accept, reject } verifies an opening.
The scheme is correct if honest openings always verify, and
succinct if | C | and | π i | are bounded by a
fixed polynomial in λ and log n . It is
position-binding if every PPT adversary wins the following
game with probability negl (λ) : given pp , the
adversary outputs (C, i, v, v ′, π, π ′) and wins iff
Theorem 10.25 (Merkle trees are succinct position-binding vector commitments).
Instantiate the syntax by: Setup samples h (and
fixes d with
Proof.
Correctness is completeness
(Proposition 10.8), and the size bounds are
Proposition 10.9. For position-binding, suppose an
adversary outputs two accepting openings (v, π) and
(v ′, π ′) at the same index i under the same root C ,
with
Remark 10.26 (Position-binding versus path soundness).
The two theorems serve different verifiers. Path soundness (Theorem 10.12) fixes an honest root and forbids opening a position to anything but its true value, for a verifier that trusts the origin of the root. The vector-commitment theorem (Theorem 10.25) forbids opening a single position two different ways even under an adversarial root, for a verifier that received the root from an untrusted source; it expresses the intended meaning of “commitment”: a commitment C determines at most one value per position, whoever produced C . Both proofs collide two chains at their first level of agreement, forged against genuine in the first case and forged against forged in the second.
10.9 Privacy-preserving membership via zero-knowledge paths
The membership proof of §10.4 is succinct but not private: it discloses the leaf value (here, the note commitment being spent) and its index i , and the sibling labels can leak structural information about the neighbourhood of the leaf. An observer correlating spends with the appends that created their leaves would link payments end to end. The remedy proves the existence of a valid path in zero knowledge, with the entire path a private witness and only the root public.
Definition 10.27 (The membership relation).
For the domain-separated Merkle construction of depth d , with leaves entering as level- 0 labels under the convention of Definition 10.18, define
| R mem := { (rt ; (v, i, π)) : Verify (rt, i, v, π) = accept }, |
with the statement the public root rt and the witness comprising the leaf v , its index i , and the authentication path π . A zero-knowledge argument for R mem lets a prover convince a verifier that some leaf lies in the tree with root rt while revealing none of v , i , or π . We assume a zk-SNARK as §9 develops it (Definition 9.25): completeness (honest provers convince), knowledge soundness (an accepting prover “knows” a witness, formalised by an extractor), and zero knowledge (the proof reveals nothing beyond the truth of the statement, formalised by a simulator).
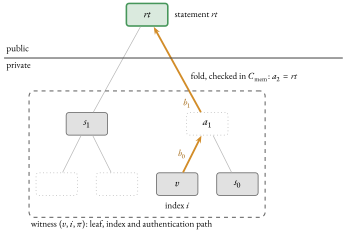
Construction 10.28 (In-circuit path verification).
The Merkle-path circuit C mem of depth d takes as
public input the root rt , and as private (witness)
inputs the leaf v , the direction bits
Theorem 10.29 (Privacy-preserving membership).
Let h be collision resistant and let (P, V) be a zk-SNARK for R mem —equivalently, for satisfiability of C mem . Then the protocol “the prover sends a SNARK proof for the statement rt ; the verifier checks it” is a membership argument that is:
-
1.
complete: a prover holding a genuine leaf and its path produces an accepting proof;
-
2.
sound: any prover producing an accepting proof for an honest root
rt = root (L) knows—via the SNARK extractor—a witness (v, i, π) with Verify (rt, i, v, π) = accept , and v equals the genuine leaf L i unless a collision in h is thereby found: the proven leaf is a real member of the committed list; -
3.
private: the proof reveals nothing about v , i , or π beyond the fact that some valid leaf exists under rt .
Proof idea.
Completeness composes SNARK completeness with tree completeness
(Proposition 10.8): the genuine
(L i, i, π i) satisfies C mem , and the honest
prover proves it. Soundness composes the SNARK knowledge extractor
with the path-forgery-to-collision extractor of
Theorem 10.12: from an accepting prover, the
SNARK extractor produces (v, i, π) accepted by
Verify ; if
Remark 10.30 (Public root, private path; deployment trade-offs).
In R mem the root must be public so that the verifier checks the proof against a state everyone agrees on—a previously published note-commitment-tree anchor—and soundness is relative to that public root, as Remark 10.13 delimits. The path must be private so that observers cannot link the spend to a particular leaf. SNARK succinctness adds a third property: the verifier checks a proof whose size is essentially independent of d —polylogarithmic—even though the witness contains d siblings, so the construction compresses the membership proof as well as hiding it.
Deployments differ in where they bear the cost of that verification. Pairing-based schemes such as KZG (§4.9) achieve constant-size proofs with fast verification, at the price of a trusted setup. Halo 2’s IPA-based proofs grow logarithmically in size, but their verification is linear in the circuit size; the deployment amortises it by batch-verifying many proofs in a single multiexponentiation. The accumulation technique of the Halo lineage—which would make per-proof verifier work sublinear by deferring the linear check across recursively composed proofs—is not deployed: each Orchard proof is verified, in batch, directly.
10.10 A shielded spend, end to end
This subsection composes the constructions of the volume into an Orchard shielded spend; every primitive it uses is constructed in this volume, and the description follows deployed Orchard.
Example 10.31 (An Orchard shielded spend).
Each shielded output of a transaction appends a note commitment cm —itself a hiding, binding Sinsemilla commitment to the note’s value, recipient, and randomness (§4.8)—as a leaf of an append-only Merkle tree built with the Sinsemilla compression function of Remark 10.17. Strictly, the leaf is the extracted x -coordinate
| cm x = ExtractP (cm), |
a 255 -bit Pallas base-field element (Math Guide, §“Pallas and Vesta assembled”) matching the child encodings of Remark 10.17. The tree as it stands at the end of each block has a root, and a transaction names one such root of an earlier block as its anchor (protocol specification § 3.7).
To spend a note, its owner:
-
1.
locates the leaf cm x in the public tree and reads off its authentication path π and position i ;
-
2.
chooses a recent anchor
rt = root m whose tree already contains the leaf—any recorded historical anchor serves, per §10.7; -
3.
proves in zero knowledge, per Theorem 10.29, the statement rt with witness (cm x, i, π) : membership of the note commitment under the anchor, well-formedness of the note opening, and correct derivation of a nullifier—a deterministic tag whose on-chain uniqueness prevents double-spending, computed from the note and the spender’s nullifier key on PRF nfOrchard of §3.8 by a construction of a later volume (the recomputed root is constrained to equal the public anchor, and the instance carries the anchor and the nullifier; protocol specification § 4.9, ‘Merkle Path Validity’, and § 4.18.4, ‘Action Statement’);
-
4.
publishes the proof and the nullifier—but neither cm , nor i , nor π .
By Theorem 10.29, the spend convinces the network that the spender owns some note genuinely added to the tree—soundness resting on the collision resistance of Sinsemilla (Proposition 4.30) and the knowledge soundness of the proof system—while the network learns nothing about which note. (In the deployed circuit the root-equals-anchor constraint is enforced for notes of nonzero value, while zero-valued dummy spends may witness an arbitrary path—by design, so that every action carries a spend whether or not a real note backs it.) The Merkle root is thus a succinct, binding, privacy-preserving commitment to the set of all notes ever created.
In the spend, the note commitment is the hiding and binding commitment of §4; the tree hash and its personalised domains apply the domain-separation discipline of §3, instantiated by Sinsemilla; the nullifier is derived from a PRF of §5 instantiated by Poseidon; the proof is a zk-SNARK of §9 for the relation R mem extended with the note’s opening; and the authorising signatures over the spend—re-randomised RedDSA for spend authority, the binding signature for value balance—are those of §8. How the pieces sit inside a transaction, per Action, with the key hierarchy and note-delivery encryption around them, is treated in a later volume of the series.