5 Waiting for confirmations
The merchant’s defence is patience: ship only after the paying transaction has confirmations (Definition 2.3). This section computes exactly how much that patience buys in the paper’s first-seen model. The paper’s model of the attack timeline has one convention worth surfacing before the theorem.
Remark 5.1 (The pre-mined block).
The paper assumes the attacker banks one block before the race is scored: “we assume one block was pre-mined by the attacker before commencing the attack” (§4). The attacker forks from the public leaf at the moment the merchant’s transaction is broadcast, and a patient attacker times the broadcast to coincide with a private block he has just found but not announced. At the moment the honest chain reaches confirmations, the attacker who has found further blocks therefore holds , and the deficit walk of Definition 4.3 starts at
The convention is a modelling choice, not a law: an attacker with no banked block starts at , and every probability below shrinks accordingly. It is also, as Theorem 5.2 shows, precisely the choice that makes the final formula collapse into a symmetric race.
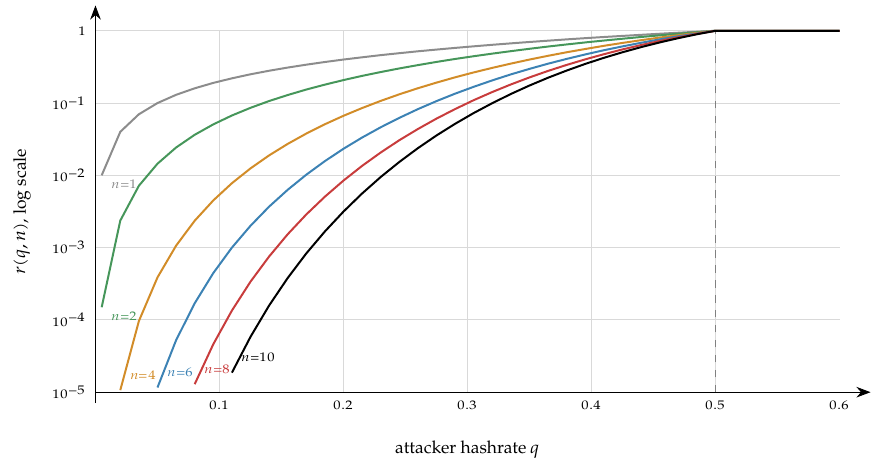
By Proposition 3.5, the number of attacker blocks found while the honest network finds its is negative binomial. Averaging the catch-up probability of Theorem 4.4 over gives the central result for the specification and Rosenfeld first-seen tie rule. Section 8.1 explains the additional success opportunity supplied by Zebra’s tie-break. The model is not an exact deployed rollback probability.
Proof.
Conditioning on and applying Theorem 4.4 at ,
valid for ; when every and immediately. For the first sum, each term transforms exactly:
which by Lemma 3.6 is the probability that the attacker’s -th block arrives while the honest network holds ; summed over , the first sum is , the probability that the attacker wins the first-to- race. The second sum is by the same lemma. Hence , the right-hand form of (2); the middle form follows from applied to one of the two copies. The printed upper limit in the paper’s equation (1) is rather than ; the term is identically zero, so the forms agree. □
Remark 5.3 (The race doubling).
The proof exposes a structure the paper’s algebra passes through silently: under the one-pre-mined-block convention, the catch-up half — the honest chain reaches first and the attacker later overtakes — has exactly the same probability as the already-ahead half, in which the attacker reaches first. A first-to- winner may have fallen behind and recovered along the way; neither half asserts otherwise. Thus the double-spend probability is twice the chance of winning a first-to- race. The identity also absorbs the boundary case: at each race half is exactly , giving with no case split, continuously with the regime. The algebra here is the paper’s; reading its two sums as the two halves of one race, and the observation that the pre-mine convention is what makes them equal, are this volume’s presentational additions (verified by script over random ; the two sums agree to floating-point precision).
Example 5.4 (A full race, exactly).
Take (a twenty-percent attacker) and . The deficit starts at , the catch-up factor is , and every quantity below is an exact rational, printed to six decimals (script-computed):
| product | |||
| catch-up half (sum of products) | |||
| already-ahead half, | |||
The two halves agree to every printed digit — they are equal exactly, by Remark 5.3 — and the closed form (2) evaluates to the same . A merchant facing a possible twenty-percent adversary who ships after six confirmations is assigned a strict-overtake probability by this model.
Remark 5.5 (Satoshi’s approximation).
The whitepaper’s §11 computes the same quantity with one approximation and two offsetting conventions: the attacker’s progress is approximated as Poisson with mean (the law on the nonnegative integers); no block is pre-mined, but success is scored at breakeven rather than strictly ahead, and those two conventions cancel exactly — the whitepaper’s catch-up factor for attacker blocks is , term for term the factor of Remark 5.1. The Poisson approximation is the entire gap. In each of the following script-computed comparisons it pushes the estimate down: at , , the whitepaper’s formula gives against the exact — an understatement by a factor of about ; at , : against ; at , : against . The direction is not uniform over all ; the reason to prefer the negative binomial model is that it is exact under the stated assumptions, not that the approximation is always one-sided.
| for every | ||||||||||